
Advisories
Android 17 Locks Accessibility Services to Verified Tools Under Advanced Protection
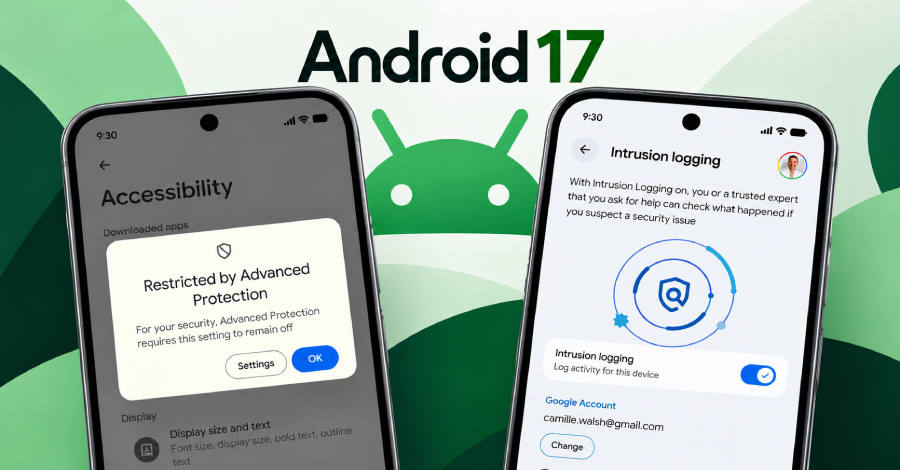
Google’s Android 17 introduces a restriction that limits the AccessibilityService API to only verified accessibility tools when Advanced Protection is enabled. This change closes a major malware vector used by banking trojans and spyware to hijack user interfaces. Defenders should enable Advanced Protection, audit installed accessibility services, and block any unverified apps from requesting these permissions.
What Happened
Google announced that starting with Android 17, the AccessibilityService API will only be granted to applications that Google verifies as Accessibility Tools when a device has Advanced Protection enabled.
Impact
Malware that previously leveraged the API to read UI events, inject fake login screens, and initiate unauthorized fund transfers will be blocked unless the app is on the verified list. Devices with Advanced Protection remain protected, while those without may still expose the vector.
What to Do
- Enable Advanced Protection on all managed devices.
- Review the list of installed accessibility services and revoke any that are not recognized as legitimate tools.
- Block sideloading of apps that request AccessibilityService permissions and enforce Play Protect.
Monitoring Recommendations
- Use device‑management consoles to audit accessibility permissions and set alerts for new services that request the API.
- Consider whitelisting only approved tools and blocking all others.
Related articles
Google Updates Android Theft Protection with Enhanced Authentication Safeguards
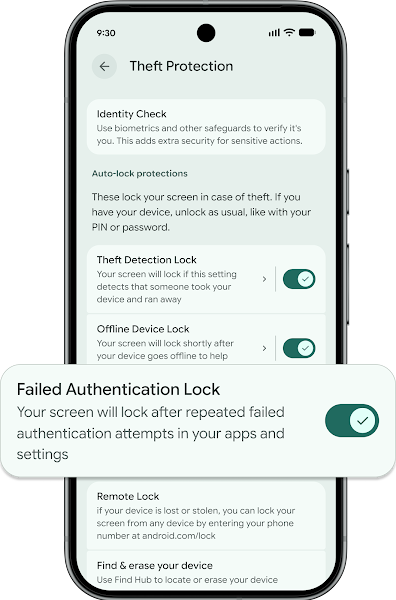
Google has announced new updates to Android's theft protection features, introducing granular controls for failed authentication locks and expanding biometric verification requirements across sensitive apps. These updates aim to mitigate physical device compromise and subsequent financial fraud on supported Android devices.
Read briefing
BTMOB Android RAT: Phishing, Fake App Stores, and Accessibility Exploit
BTMOB is an Android RAT that spreads via phishing sites and counterfeit app stores, then abuses Accessibility Services to gain full device control. The malware is sold with an APK‑builder, enabling rapid, code‑free payloads. Defenders should block malicious domains, disable unknown accessibility services, and enforce app‑store vetting.
Read briefing
Mantax Otax Malware Hybridizes Ransomware, Spyware, and Psychological Harassment on Android
Security researchers have uncovered Mantax Otax, an aggressive Android malware strain combining file encryption, data exfiltration, and psychological harassment techniques. Operating primarily through malicious side-loaded APKs, the threat abuses Accessibility services and GitHub to establish C2 connections, harvest sensitive user credentials, and lock files on older Android builds. Additionally, the malware deploys loud text-to-speech audio and jumpscare overlays to coerce victims into paying ransom demands.
Read briefing
Android pKVM Earns SESIP Level 5 Certification – Implications for Mobile Hypervisor Security
Google’s protected KVM (pKVM) hypervisor for Android has achieved SESIP Level 5 certification, the highest security assurance for consumer‑electronics software. The certification, performed by Dekra under the TrustCB scheme, validates pKVM against ISO 15408 penetration testing and resistance to advanced attackers. Defenders should review hypervisor integrity controls and update deployment practices accordingly.
Read briefing