
Threat Intel
Inside the First Hours of a Google Workspace Breach: Live Webinar Reveals What Works and What Doesn’t
BleepingComputer partners with Material Security to host a live deep‑dive on how fast‑growing firms handle Google Workspace intrusions. The session dissects real breaches where attackers used social engineering and rogue OAuth apps, highlighting the critical early decisions that can either curb damage or amplify it. Attendees learn which controls deliver the most bang for lean security teams and hear the speakers’ take on building a resilient Workspace strategy from scratch.
When a Google Workspace compromise is spotted, the clock starts ticking. The choices made in the first few hours can dictate whether a breach fizzles or turns into a full‑blown disaster.
What the Webinar Covers
- Real‑world case studies of Workspace breaches that leveraged social engineering + malicious OAuth apps.
- Key early actions that either limited impact or inadvertently widened the attack surface.
- Common blind spots that leave users, data, and connected apps exposed.
- High‑value security controls for fast‑growing companies with lean teams.
- Design‑phase lessons: what to build into a Workspace security program from day one.
Why It Matters
Fast‑growing firms often operate with minimal security staff. Making swift, informed decisions while still piecing together how an attacker got in is a tough balancing act. This webinar cuts through the jargon and shows how real responders tackled the chaos.
"The first hours after a breach can either contain or amplify the damage," says Rajan Kapoor, VP of Security at Material Security.
Who Should Attend
- Security engineers and incident‑response teams handling Google Workspace environments.
- IT leaders in fast‑moving companies looking to strengthen their Workspace posture.
- Anyone interested in practical, evidence‑based breach‑response tactics.
Register Now
Secure your spot for the September 23, 2026 webinar and get actionable insights that could save your organization from a costly breach.
Related articles
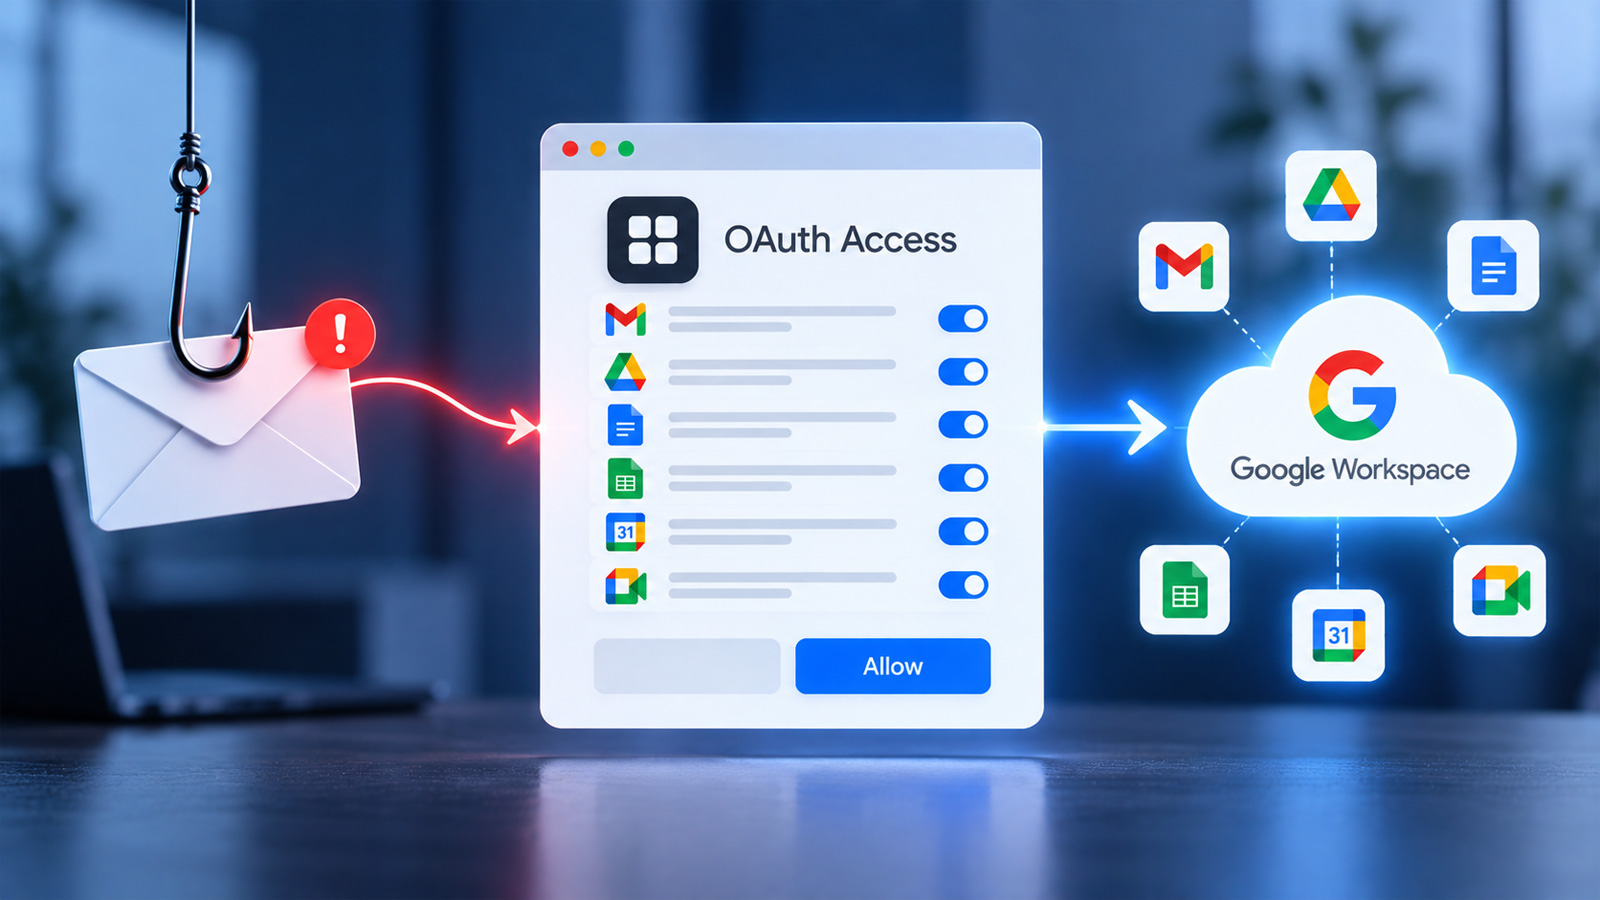
Webinar Explores How Malicious OAuth Apps Breach Google Workspace
A live session by BleepingComputer and Material Security dissected two real‑world breaches where attackers used social engineering to get users to grant permissions to rogue OAuth apps, bypassing password theft. The talk highlighted the rapid escalation of such attacks, the critical first‑hour decisions, and a prioritized list of security controls that fast‑growing firms can deploy with minimal effort.
Read briefing
Tycoon 2FA AiTM: The Phishing‑as‑a‑Service Threat That Bypasses MFA on Entra ID & Google Workspace
Tycoon 2FA, the top‑selling phishing‑as‑a‑service kit, has evolved into a sophisticated adversary‑in‑the‑middle tool that captures MFA‑protected session tokens for Microsoft 365 and Google Workspace. After a March 2026 takedown, operators pivoted to device‑code phishing and OAuth abuse, keeping the kit at the forefront of global phishing trends. Elastic’s new detection rules map telemetry fingerprints across both platforms, enabling rapid incident containment in under ten seconds via Elastic Workflows.
Read briefing
CISA Mobilizes Nationwide Cyber Defense for 2026 FIFA World Cup
CISA is coordinating with federal, state, local, tribal and private partners to identify and mitigate cyber threats targeting the 2026 FIFA World Cup. The initiative focuses on risk reduction, preparedness, and ensuring a secure, seamless experience for fans and host communities across the U.S.
Read briefing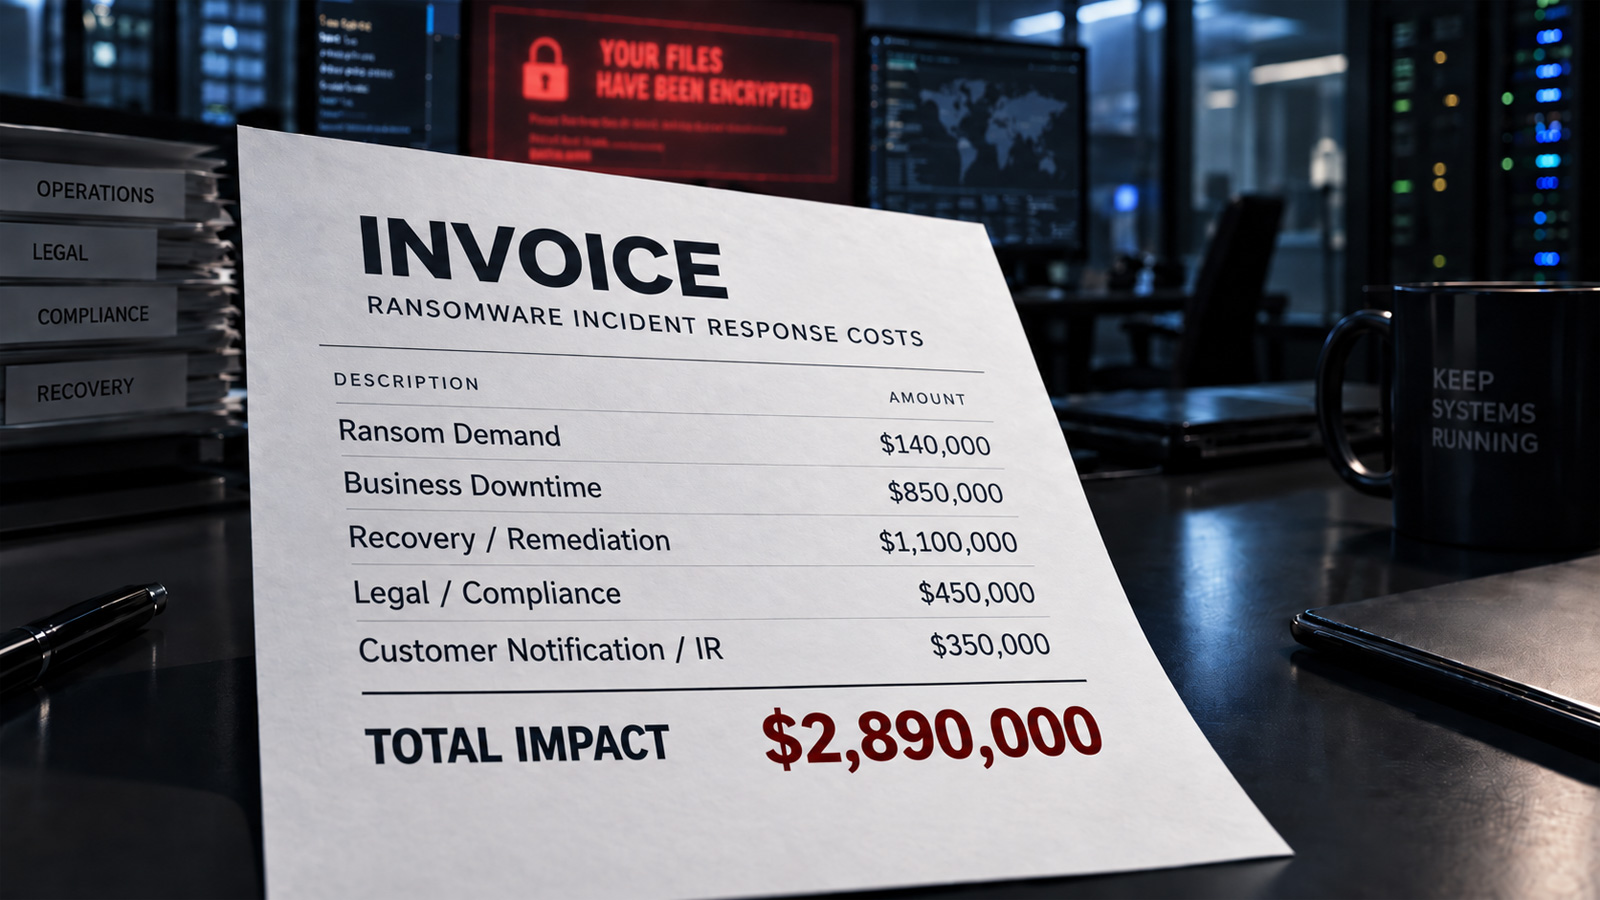
Ransomware Costs Reveal: Ransom Is Just the Tip of the Iceberg – Downtime, Recovery and Compliance Add Millions
While the headline ransom payment often steals the spotlight, the real financial damage from a ransomware hit runs into the millions. New data shows an average total cost of $5.08 million per incident, compared to a median ransom of roughly $140 k. Prolonged downtime, complex recovery, and regulatory fallout drive the bulk of the bill. Only 35 % of firms actually restore critical systems in under a day, despite 60 % claiming they can. A mature Business Continuity & Disaster Recovery (BCDR) plan can slash downtime, streamline backups and ease compliance, dramatically reducing the overall hit.
Read briefing