
Threat Intel
Ransomware Costs Reveal: Ransom Is Just the Tip of the Iceberg – Downtime, Recovery and Compliance Add Millions
While the headline ransom payment often steals the spotlight, the real financial damage from a ransomware hit runs into the millions. New data shows an average total cost of $5.08 million per incident, compared to a median ransom of roughly $140 k. Prolonged downtime, complex recovery, and regulatory fallout drive the bulk of the bill. Only 35 % of firms actually restore critical systems in under a day, despite 60 % claiming they can. A mature Business Continuity & Disaster Recovery (BCDR) plan can slash downtime, streamline backups and ease compliance, dramatically reducing the overall hit.
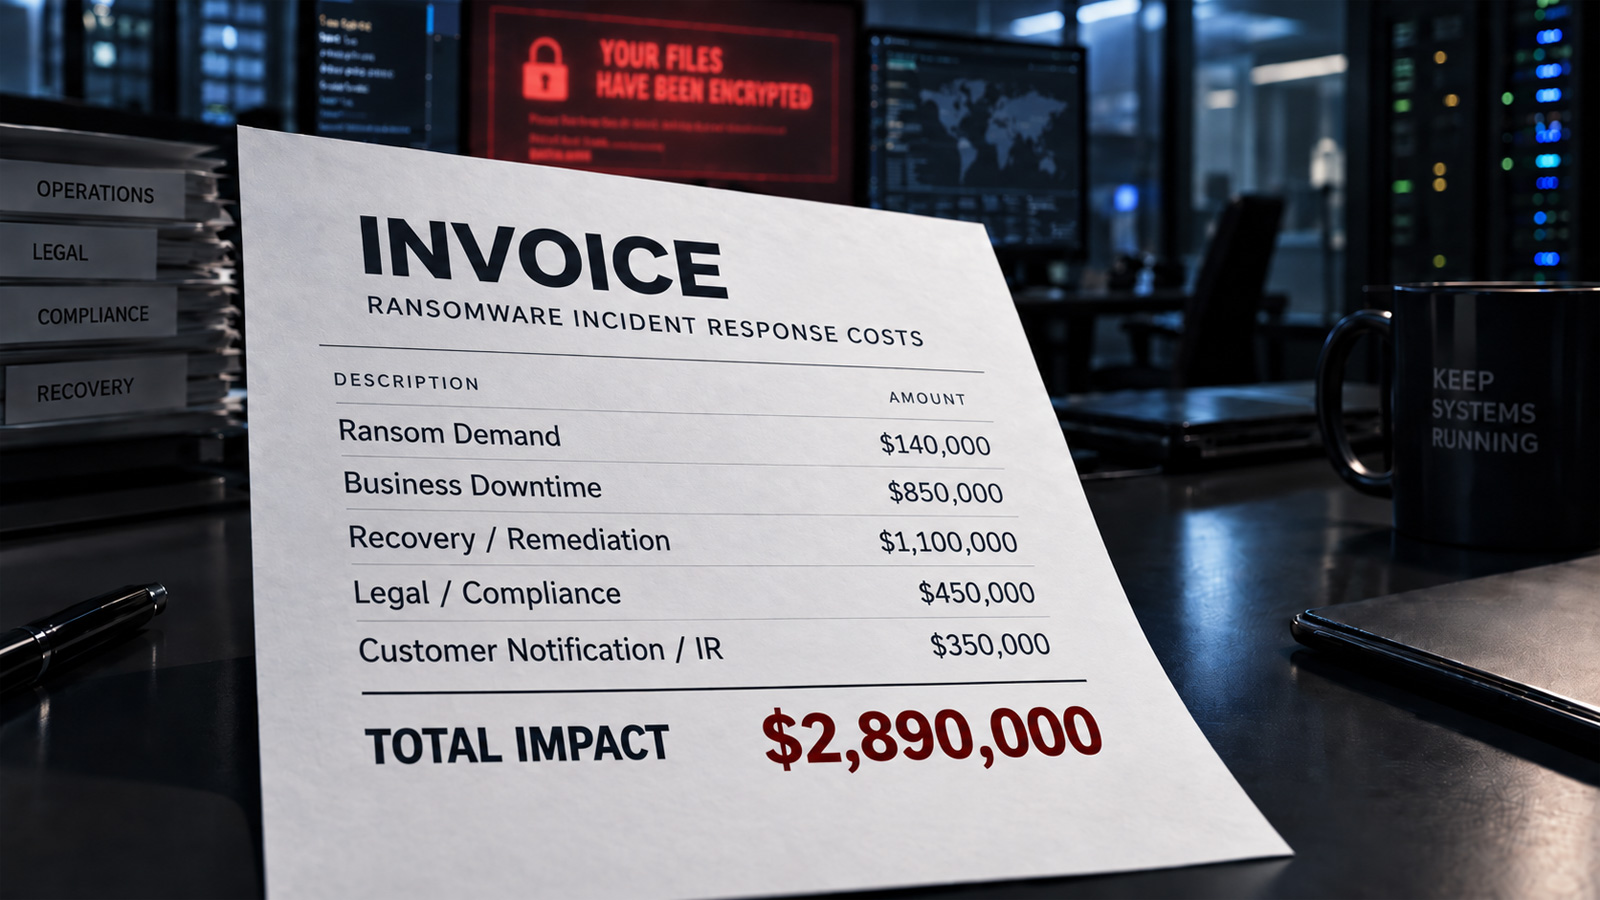
When a ransomware attack lands, the first thing on the radar is often the ransom demand. But that is merely the opening line on a multi‑page invoice.
The Ransom Is Just the Beginning
According to IBM’s 2025 Cost of a Data Breach Report, the average total cost of a ransomware incident tops $5.08 million. In stark contrast, Verizon’s 2026 Data Breach Investigations Report lists the median ransom paid at just $139,875. The gap tells a clear story: the bulk of the damage unfolds after the attack.
Downtime Drives the Price
- Every hour a critical system is offline translates into lost revenue, delayed transactions and customer churn.
- Datto’s 2025 State of BCDR Report found that 60 % of organizations believe they can recover in under a day, yet only 35 % actually do.
- For mid‑market firms, the faster you restore operations, the lower the cumulative loss.
Recovery: The Hidden Expense
Attackers now routinely target backup infrastructure. If backups are corrupted or inaccessible, recovery can require forensic investigations, system rebuilds, new software and a heavy IT workload. Even when backups exist, they must be clean, accessible and tested—something only mature BCDR programs guarantee.
Compliance: Legal Lightning Rod
- GDPR demands breach notification within 72 hours.
- SEC requires public companies to disclose material incidents within four business days.
- HIPAA, PCI‑DSS and other regulations add their own timelines and penalties.
These regulatory clocks start ticking the moment the breach is discovered, adding legal fees, investigations and potential fines to the cost stack.
BCDR Maturity Cuts the Bill
A tested recovery strategy turns a backup into a working system faster and more reliably. By reducing downtime, easing forensic work, and streamlining compliance reporting, a mature BCDR plan can shave millions off the total cost.
“Ransomware is a multi‑layered financial threat. The ransom is just the tip of the iceberg.”
Related articles
Ransomware Gangs Exploit Critical VMware vCenter RCE (CVE‑2026‑59310) – CISA Urges Urgent Patching
CISA has flagged the July‑patched VMware vCenter flaw CVE‑2026‑59310 as actively abused by ransomware operators. The directory‑traversal bug in the vCenter Syslog server lets unauthenticated attackers run arbitrary code, enabling reverse‑SSH back‑doors and data exfiltration. Over 450 exposed vCenter instances and more than 360 compromised IPs across 47 countries have been identified. CISA now demands all federal agencies secure their vCenter deployments within three days and urges private sector customers to apply the patch immediately.
Read briefing
Ukrainian Conti Ransomware Operative Gets 4 Years Behind Bars
A 44‑year‑old Ukrainian national, Oleksii Lytvynenko, was sentenced to four years in U.S. prison for his role in the Conti ransomware campaign that hit over 1,000 victims worldwide and raked in more than $150 million in ransom. Arrested in Ireland and extradited to the U.S., Lytvynenko admitted to developing a loader, managing stolen data, and sending ransom notes between 2021‑2022. The case underscores the growing pressure on Conti’s remnants and the broader crackdown on the cyber‑crime syndicate that spawned groups like BlackCat and Hive.
Read briefing
Mantax Otax Malware Hybridizes Ransomware, Spyware, and Psychological Harassment on Android
Security researchers have uncovered Mantax Otax, an aggressive Android malware strain combining file encryption, data exfiltration, and psychological harassment techniques. Operating primarily through malicious side-loaded APKs, the threat abuses Accessibility services and GitHub to establish C2 connections, harvest sensitive user credentials, and lock files on older Android builds. Additionally, the malware deploys loud text-to-speech audio and jumpscare overlays to coerce victims into paying ransom demands.
Read briefing
AI‑Powered Attack Hits 395 PaperCut Servers Across 48 Countries
A likely Russian‑speaking threat actor leveraged hundreds of AI agents to craft, test, and launch a global campaign against PaperCut NG/MF servers, exploiting CVE‑2026‑81578 and CVE‑2026‑82078. Within hours of launching, the attackers achieved remote code execution, escalated to domain admin in minutes, and compromised 395 organizations—roughly half in education—across 48 nations. The operation used pass‑the‑hash, DCSync, and custom Rust utilities to harvest credentials and domain secrets. Immediate patching of the two CVEs is mandatory.
Read briefing