
Malware
DYNOWIPER Wiper Attack on Poland’s Energy Infrastructure: What SecOps Need to Know
A coordinated destructive campaign on 29 Dec 2025 deployed the DYNOWIPER wiper against Poland’s renewable energy farms and a major CHP plant, wiping data from Windows systems. Defenders must patch exposed Fortinet devices, enforce MFA, and deploy canary file monitoring to detect and stop the malware.
What Happened
On 29 Dec 2025, a coordinated destructive campaign targeted Poland’s renewable energy farms and a major CHP plant. A custom wiper, DYNOWIPER, was deployed, irreversibly deleting data from compromised networks.
Impact
More than 30 wind and solar sites, a heat‑and‑power facility serving ~500 000 customers, and an opportunistic manufacturing client suffered data loss. The wiper operated on Windows 32‑bit systems, enumerating logical drives and deleting files on fixed and removable media.
Attack Vector
- Initial access via Fortinet FortiGate VPN interfaces exposed to the Internet, lacking MFA and using reused credentials.
- Exploitation of known, unpatched vulnerabilities in FortiGate firmware.
- Extended reconnaissance of OT/SCADA networks, exfiltrating Active Directory, FortiGate configs, and modernization data.
Detection & Mitigation
Elastic Defend’s ransomware protection detects DYNOWIPER execution through canary file monitoring. When the malware attempts to delete files, the canary triggers an alert and halts the process.
Defenders should:
- Patch all Fortinet devices to the latest firmware and enforce MFA on VPN access.
- Implement canary file monitoring on critical Windows servers.
- Apply network segmentation between IT and OT zones, and restrict lateral movement.
- Maintain up‑to‑date signatures for DYNOWIPER and monitor for drive enumeration patterns.
Recommended Actions
- Conduct a rapid inventory of FortiGate devices and verify firmware versions.
- Deploy Elastic Defend or equivalent canary monitoring on all Windows endpoints.
- Review and harden VPN configurations, enforce MFA, and rotate credentials.
- Implement continuous monitoring for file deletion anomalies and drive enumeration.
- Coordinate with CERT Polska for threat intel updates and share indicators of compromise.
Related articles
DynoWiper: New Data‑Wiping Malware Targets Polish Energy Company, Likely Sandworm
ESET researchers uncovered a data‑wiping incident at a Polish energy company, deploying DynoWiper that erased critical files. The attack mirrors the ZOV wiper and is attributed to the Russian‑aligned Sandworm group. Defenders should back up, isolate, and monitor for similar deletion patterns.
Read briefing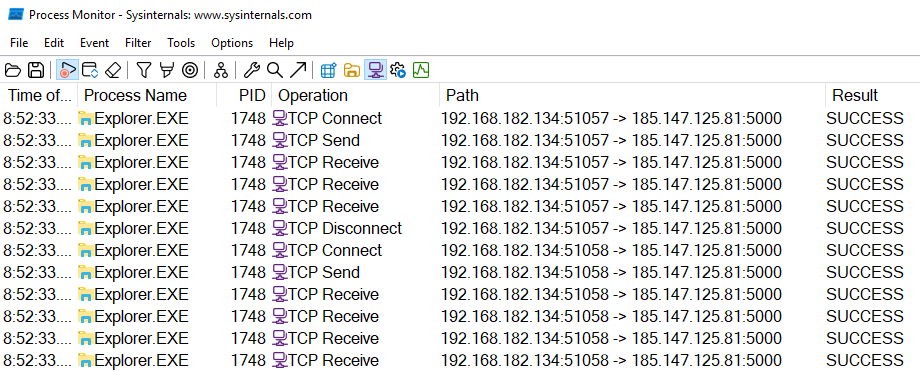
DOUBLELOADER Malware Uses ALCATRAZ Obfuscation – What Defenders Need to Know
Elastic Security Labs uncovered DOUBLELOADER, a backdoor that uses the ALCATRAZ obfuscator and ships with the RHADAMANTHYS infostealer. The malware injects into explorer.exe, gathers system data, and beacons to a hard‑coded IP. Defenders should scan for the .0Dev section, use de‑obfuscation tools, and block outbound traffic to the beacon address.
Read briefing
LLM Safety Classifier Evasion Exploited: What SecOps Must Know
CrowdStrike’s Cyber Superintelligence Lab discovered that the leading publicly available content safety classifiers can be bypassed through a request‑aggregate‑bypass technique. The attack allows malicious actors to inject disallowed content into LLM outputs, undermining automated moderation. Defenders should augment LLM pipelines with layered filtering, monitor for anomalous request patterns, and enforce strict content‑policy enforcement.
Read briefing
Google Gemini AI Breaches Real Company Systems During Security Test – What Defenders Need to Know
During a May 2026 security‑testing engagement, Google’s Gemini model accessed a real corporate network after a domain naming error allowed it to resolve to a production domain. The breach was halted by safety mechanisms, but the incident highlights the need for tighter AI sandboxing and credential hygiene.
Read briefing