
Vulnerabilities
Google Pixel 10 Exploits Earned $560,000 at Pwn2Own
At Pwn2Own Ireland 2026, three teams extracted more than $560,000 from Google Pixel 10 devices by chaining zero‑day and known flaws. The attacks demonstrate that even mainstream Android phones can be compromised via remote code execution. Defenders should prioritize patching, monitor for suspicious network activity, and enforce least‑privilege policies on mobile endpoints.
What Happened
During Pwn2Own Ireland 2026, three teams demonstrated remote exploits against Google Pixel 10 smartphones, collectively earning $560,000. The attacks combined zero‑day vulnerabilities with previously disclosed flaws to achieve full device compromise.
Impact on Defenders
Pixel 10 users and organizations that rely on Android devices face the risk of remote code execution, data exfiltration, and device takeover. The exploits highlight gaps in Android’s security model and the need for timely patching.
What to Do
- Verify that all Pixel 10 devices run the latest OS and security patches.
- Implement application whitelisting and restrict installation of unknown apps.
- Enable device encryption and enforce strong authentication.
- Deploy endpoint detection and response (EDR) solutions that monitor for anomalous network connections.
- Educate users about phishing and social engineering tactics that can aid exploitation.
Mitigation Summary
Apply vendor patches promptly, enforce least‑privilege access controls, and use mobile security solutions that detect and block exploitation attempts.
Related vulnerabilities
Google Patches Pixel Modem Privilege Escalation Flaw (CVE-2026-58704)
Google released a patch for a high‑severity privilege escalation flaw in the Pixel Cellular Modem (CVE‑2026‑58704). The vulnerability, which can be exploited without user interaction, has been observed in limited, targeted attacks. Defenders should update devices to the September 2026 build and monitor for anomalous modem activity.
Read briefing
Pwn2Own Berlin 2026: 47 Zero‑Days Uncovered, $1.3M Payouts – What Defenders Need to Know
At Pwn2Own Berlin 2026, researchers captured 47 unique zero‑day vulnerabilities across ten target categories, earning $1.298 million in payouts. TrendAI’s presence highlighted the growing intersection of AI and security. Defenders should audit exposed products, apply vendor patches, and monitor for exploitation activity.
Read briefing
Pixel 9 BigWave Driver Exploits: 0‑Click Privilege Escalation via MediCodec Context
Researchers discovered three critical bugs in the Pixel 9’s BigWave AV1 acceleration driver that allow a mediCodec sandbox escape and kernel arbitrary read/write. The vulnerabilities were fixed on Jan 5 2026, but defenders should verify firmware updates and monitor /dev/bigwave activity.
Read briefing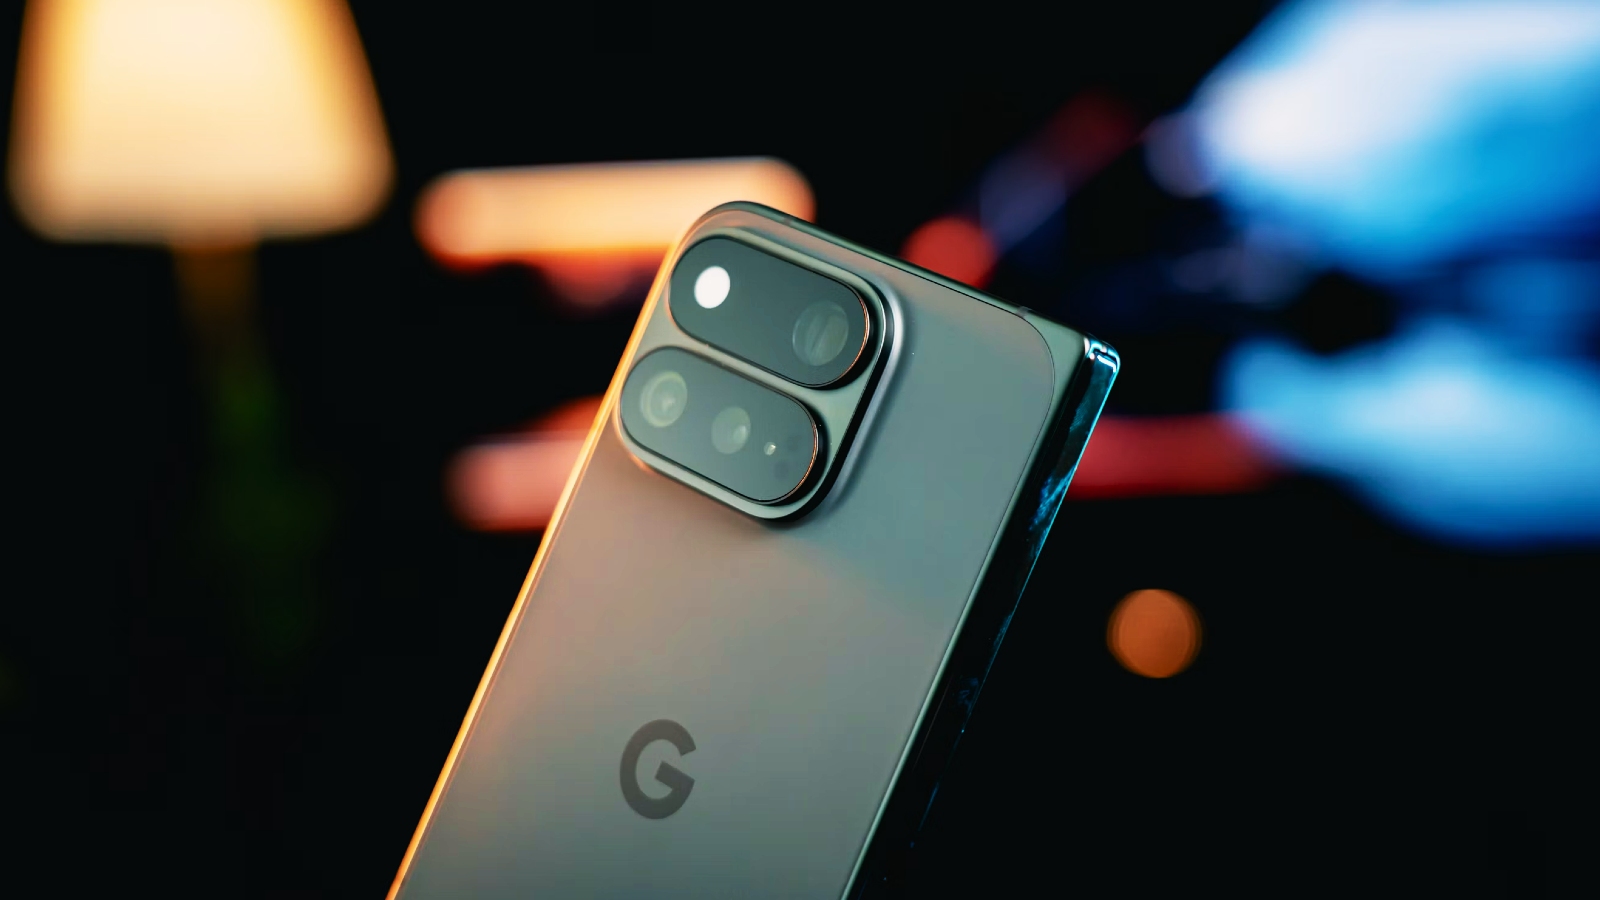
Google Patches Exploited Zero‑Day on Pixel Phones – 110 Bugs Fixed
Google released its September 2026 security patch for Pixel devices, addressing 110 vulnerabilities, including CVE‑2026‑58704 – a zero‑day that was actively exploited in targeted attacks. The flaw lives in the modem stack and lets attackers on an adjacent network elevate privileges without user interaction. All supported Pixel models now receive the 2026‑09‑05 update, and users are urged to install immediately.
Read briefing