
Vulnerabilities
Microsoft October 2026 Patch Tuesday: 1,413 CVEs, 3 Zero‑Days, 75 Critical Vulnerabilities
Microsoft released security updates for 1,413 CVEs, including three zero‑days—one actively exploited—and 75 critical flaws. The update covers Windows, Office, and Azure services. Defenders should apply patches immediately, verify affected components, and monitor for exploitation attempts.
What Happened
On October 10, 2026, Microsoft issued Patch Tuesday updates addressing 1,413 CVEs. Among them were three zero‑day vulnerabilities: one actively exploited in the wild and two publicly disclosed. The patch set also includes 75 critical‑severity flaws across Windows, Office, and Azure platforms.
Impact
Systems running affected Windows versions, Office suites, or Azure services are at risk of remote code execution, privilege escalation, or data exfiltration. Attackers could leverage the zero‑days for initial footholds or pivot to higher‑privilege targets.
What to Do
- Run Windows Update or use WSUS to deploy the latest cumulative updates for all affected OS versions.
- Apply Office security updates via the Office Deployment Tool or update channel.
- Update Azure virtual machines and services with the latest security patches through Azure Update Management.
- Verify that all endpoints are running the patched versions; use tools like Microsoft Baseline Security Analyzer (MBSA) or PowerShell scripts.
- Monitor logs for indicators of exploitation, such as anomalous PowerShell activity, unusual SMB traffic, or unexpected privilege changes.
- Consider implementing additional mitigations (e.g., disabling SMBv1, enforcing least privilege, enabling Windows Defender Exploit Guard).
Additional Resources
Microsoft Security Response Center (MSRC) provides detailed advisory notes and remediation guidance for each CVE. Refer to the official MSRC website for version‑specific instructions.
Related vulnerabilities
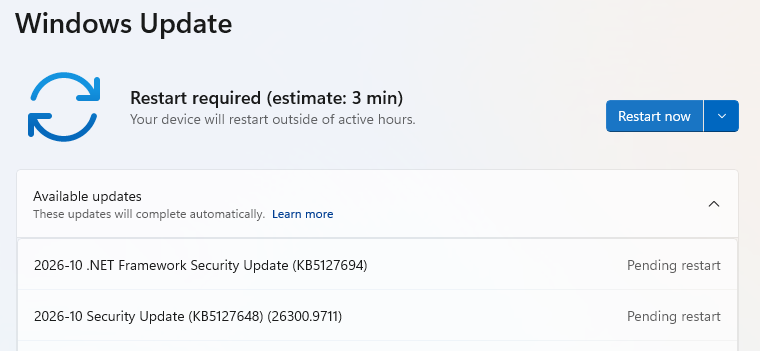
Microsoft Patch Tuesday Oct 2023: 1,413 Vulnerabilities, Including Actively Exploited Windows Shell Zero‑Day
Microsoft’s October Patch Tuesday released a record 1,413 fixes, including CVE‑2026‑96951, a Windows Shell zero‑day already in use, and two other publicly disclosed zero‑days. Defenders must apply the updates immediately, verify patch status, and monitor for exploitation patterns.
Read briefing
Microsoft Patch Tuesday 2026: 972 CVEs, 2 Exploited Zero‑Days, 113 Critical Vulnerabilities
Microsoft released updates for 972 CVEs on September 2026 Patch Tuesday, including two actively exploited zero‑days and 113 critical flaws. Defenders must prioritize patching Windows, Office, and Exchange, verify deployment, and monitor for exploitation attempts.
Read briefing
Microsoft Patch Tuesday: 972 CVEs, 2 Exploited Zero-Days, 113 Critical Vulnerabilities
Microsoft released security updates for 972 CVEs in September 2026 Patch Tuesday, including two zero-days that were actively exploited and 113 critical flaws. Defenders should prioritize patching affected systems, validate deployment, and monitor for exploitation indicators.
Read briefing
Microsoft Patch Tuesday 2026: Two Zero‑Days Exploited, 113 Critical Vulnerabilities Fixed
Microsoft released updates for 972 CVEs, including two zero‑days that were actively exploited and 113 critical flaws. The patches affect Windows 10/11, Windows Server 2022, and Microsoft 365 services. Defenders should immediately apply the updates, verify patch status, and monitor for exploitation indicators.
Read briefing