
Advisories
ABB Ability Edgenius Hit by CVE‑2026‑31431: Linux Kernel Privilege Escalation
ABB’s industrial gateway platform, Ability Edgenius, is vulnerable to the CVE‑2026‑31431 “Copy Fail” Linux kernel flaw, allowing local or container‑based attackers to gain root privileges. Versions 3.2.0.0‑3.2.4.0 are affected and are fixed in 3.2.4.1. The flaw originates in the kernel’s cryptographic subsystem and poses a serious risk to critical manufacturing, energy, water, and chemical facilities worldwide. Operators should apply the patch ASAP and limit SSH/cockpit access to reduce exposure.
ABB’s Ability Edgenius industrial gateway is now exposed to a critical Linux kernel vulnerability, CVE‑2026‑31431, also known as the “Copy Fail” flaw. The issue can elevate a locally authenticated user—or a compromised container workload—to root, granting full system control.
Vulnerability Overview
The flaw lies in the Linux kernel’s cryptographic subsystem and has been present in kernels released since 2017. Successful exploitation requires local code execution, but in shared or containerized environments the risk escalates dramatically.
Affected Products
- ABB Ability Edgenius versions 3.2.0.0 through 3.2.4.0 (inclusive)
- All devices running these releases on the ABB Ability Edgenius Gateway – bE100
Risk Assessment
- CVSS score: 7.8 (High)
- Root access enables full system compromise, data exfiltration, and potential sabotage of critical infrastructure.
- Industries impacted: critical manufacturing, energy, water & wastewater, chemical.
- Global deployment – the vulnerability is relevant to installations worldwide.
Mitigation & Fix
- Patch now: Upgrade to Ability Edgenius 3.2.4.1, the first release containing the fix.
- Operational hardening: Restrict SSH and cockpit access to trusted users only; by default no lower‑privilege accounts exist on Edgenius installations.
- Follow ABB PSIRT guidance for additional security hardening and monitoring.
ABB recommends applying the update at the earliest convenience to eliminate the root‑privilege escalation risk.
Impact on Critical Infrastructure
Given the platform’s use in manufacturing, energy, water, and chemical sectors, a successful exploit could lead to significant operational disruption or safety hazards. Immediate remediation is essential for all operators.
Related vulnerabilities
Linux Kernel 'Copy Fail' (CVE‑2026‑31431) Hits All Mainstream Distros – Immediate Action Needed
A high‑local privilege escalation flaw dubbed "Copy Fail" (CVE‑2026‑31431) now affects every mainstream Linux distribution using a kernel built since 2017. A public proof‑of‑concept exists, but no vendor patches have been released yet. The mainline kernel fix landed on April 1, 2026, yet distribution updates lag behind. CERT‑EU urges users to deploy the interim mitigation right away, especially on Kubernetes nodes and CI/CD runners exposed to untrusted workloads.
Read briefing
Siemens SIPLUS and SIMATIC Products – Copy Fail Vulnerability (CVE-2026-31431)
Siemens has identified a Copy Fail vulnerability affecting multiple SIPLUS and SIMATIC products. The flaw, CVE‑2026‑31431, allows attackers to read or modify files on affected systems. Defenders should upgrade to the latest firmware or apply Siemens‑issued countermeasures.
Read briefing
CVE-2026-70104: Windows Win32k Privilege Escalation Vulnerability
A local privilege escalation flaw in the Windows Win32 kernel subsystem allows an authenticated user to gain elevated rights by dereferencing an untrusted pointer. Microsoft has issued a patch; defenders should update systems immediately and verify that the kernel component is patched.
Read briefing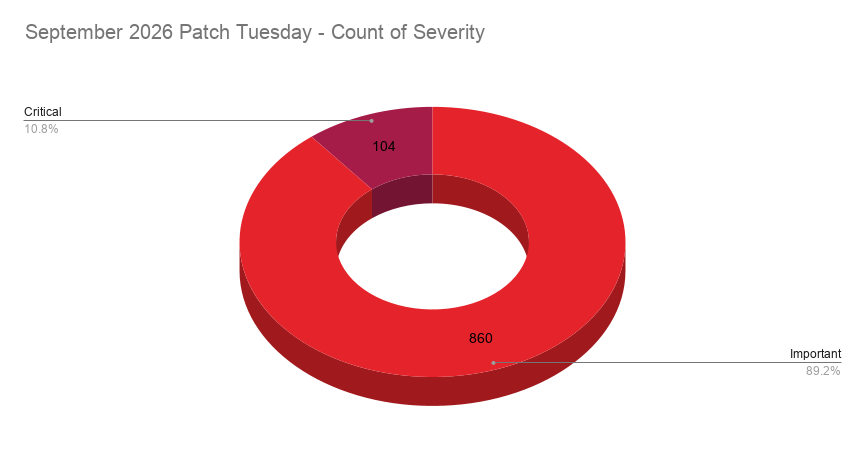
Microsoft September 2026 Patch Tuesday: 964 CVEs, Including Two Zero-Day Exploits (CVE-2026-81963, CVE-2026-85880)
Microsoft released its largest Patch Tuesday to date, addressing 964 CVEs—104 critical and 860 important—including two zero‑day vulnerabilities exploited in the wild. Defenders must prioritize applying updates to affected components such as .NET, Active Directory services, Azure services, Office, and Windows kernel drivers, and verify system integrity.
Read briefing