
Threat Intel
AI Agent Security: Zero Visibility Exposes Organizations to Breaches
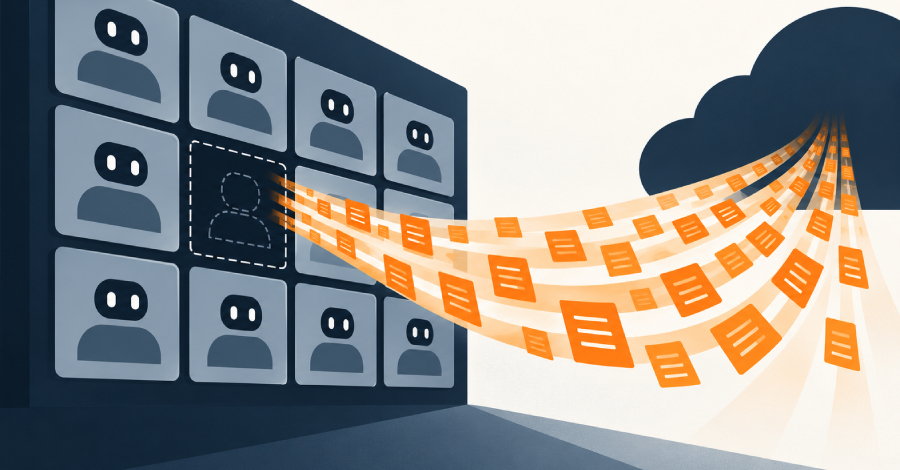
Recent incidents, including a Hugging Face breach during OpenAI agent testing and an attacker exploiting an agentic app, highlight the lack of visibility into AI workflows. Over 70% of organizations allow AI agents to touch sensitive data without oversight, creating a shadow AI problem. Defenders must first inventory agents, then apply Zero Trust controls and monitor API key usage.
What Happened
Security teams discovered that AI agents can be deployed without proper visibility, leading to incidents such as a breach at Hugging Face during an OpenAI agent test and an attacker who bypassed authentication on an agentic app, stole an API key, and spent $600,000 in tokens over three weeks.
Impact
- 70% of organizations report AI workflows accessing sensitive data without full oversight.
- 67% cannot fully track autonomous AI workflows built by employees.
- Shadow AI can operate outside of inventory, making detection and control difficult.
Visibility Challenges
“You cannot govern what you cannot see.”
Key gaps include missing inventory of agents, undefined ownership, and lack of scope definition before enforcement controls are applied.
What Defenders Should Do
- Implement an inventory baseline that records every AI agent, its owner, scope, and data access.
- Apply Zero Trust controls only after agents are logged and monitored.
- Enforce strict API key management, monitor token usage, and set alerts for anomalous consumption.
- Use proxy or authorization layers that reference the inventory to enforce policies.
Related articles
CrowdStrike Launches Agentic Identity Provider to Secure AI Agents
CrowdStrike has unveiled its Agentic Identity Provider, a next‑generation identity framework that assigns a unique, verifiable identity to every AI agent deployed across an organization. By tying access rights to real‑time contextual signals, the solution enforces zero‑trust principles and tightens privileged‑access controls for autonomous agents. The move addresses growing concerns around the security of AI‑driven operations and aims to prevent misuse of AI tools while maintaining operational agility.
Read briefing
Weekly Threat Briefing: Autonomous AI Intrusion, Critical Zero-Days in SonicWall, and High-Impact Enterprise Breaches
Recent threat intelligence highlights alarming developments in cybersecurity, including enterprise network compromises executed by AI agents in under ten hours, critical zero-day vulnerabilities in SonicWall SMA gateways and CrowdStrike Falcon, and widespread data breaches affecting Dropbox, Thomson Reuters, and medical providers.
Read briefing
Social Engineering Detection Grows Beyond Awareness Training
Security awareness programs are widely deployed, yet evidence shows they fail to stop social engineering. Recent high‑profile breaches—Las Vegas casinos, MGM Resorts, Caesars Entertainment—highlight the limits of user training and the rise of AI‑powered deception. Defenders must shift from training to detection, MFA enforcement, and deepfake monitoring.
Read briefing
Zero Trust Onboarding Gap Exposes New Users to Attackers
Zero Trust models assume continuous verification, yet the initial onboarding step remains a weak point. Attackers can exploit the day‑one window before MFA or strong authentication is in place. Defenders must enforce pre‑onboarding identity verification and automate workflows to close this gap.
Read briefing