
Defensive Security
Automating Edge Defense: Mitigating Web Fuzzing and Probing via Elastic Security and Cloudflare
Exposed web infrastructure regularly encounters automated scanners looking for sensitive endpoints and vulnerable applications. By analyzing Traefik proxy logs in Elastic Security using ES|QL detection rules, defenders can spot statistical anomalies in HTTP 404 responses and automatically block malicious IP addresses at the Cloudflare edge.
Turning Reverse Proxy Logs into Active Defense
Self-hosted web applications and enterprise portals exposed to the internet constantly attract automated scanners searching for administrative panels, unpatched vulnerabilities, and misconfigurations. While host-based security tools can enforce local blocks, shifting detection to a centralized security engine allows defenders to drop malicious traffic at the edge provider before requests ever hit the internal network.
Detecting Fuzzing Patterns with ES|QL
Automated directory brute-forcing and vulnerability scanning create clear telemetry signatures in reverse proxy access logs, primarily characterized by rapid bursts of HTTP 404 (Not Found) responses from a single source address. Scanners commonly target path patterns like legacy scripts, WordPress plugin directories, and unlinked administrative portals.
By ingesting proxy telemetry into Elastic Security and standardizing fields using the Elastic Common Schema (ECS), security teams can deploy statistical ES|QL rules. Rather than relying solely on signature matching, threshold rules analyze HTTP error rates within brief time windows to accurately detect automated fuzzing while minimizing false positives from standard browsing errors.
Automated Edge Enforcement
When a source IP breaches the defined request threshold, Elastic Security triggers an automated response action that leverages Cloudflare's API to enforce an immediate edge block. This architecture provides several operational advantages:
- Bandwidth and Host Protection: Unwanted traffic is mitigated at the edge, protecting local network capacity and web server resources.
- Centralized Management: Defenders orchestrate alerts and response workflows within a single interface rather than managing disparate server scripts.
- Extensible Integration: The automated edge-blocking workflow can be repurposed across other Elastic rules to counter SQL injections, cross-site scripting, and local file inclusion attempts.
By combining centralized log analysis with edge API enforcement, organizations can transform standard access logs into an active perimeter defense.
Related articles
Microsoft Edge Vulnerability CVE‑2026‑106412: Race Condition in Chromium
A race condition in Chromium (CVE‑2026‑106412) affects Microsoft Edge users. The flaw can enable arbitrary code execution via malicious web content. Defenders should update Edge to the patched version and monitor for suspicious activity.
Read briefing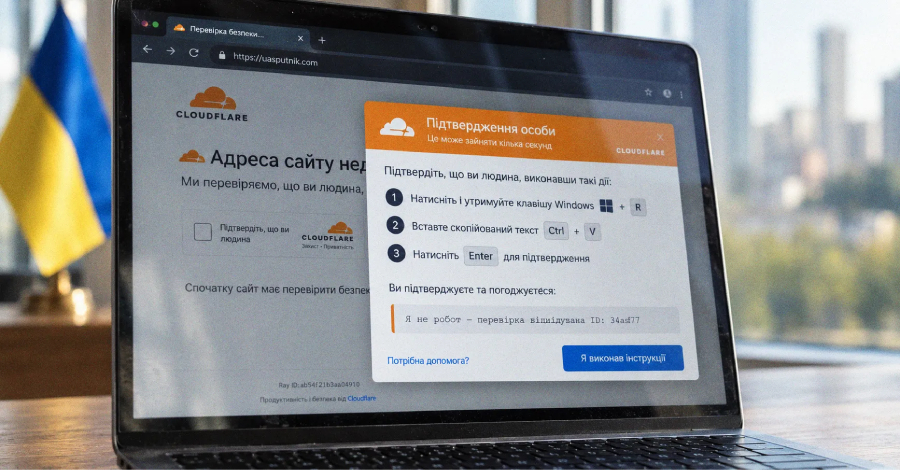
ClickFix Campaign Compromises Ukrainian Sites, Deploys Psychedelic Stealer via Fake Cloudflare Verification
An active ClickFix campaign has injected fake Cloudflare verification pages into legitimate Ukrainian business sites, tricking visitors into running an MSI installer that delivers the Psychedelic stealer. The malware harvests credentials, cryptocurrency wallet data, and establishes persistence via scheduled tasks. Defenders should block the attacker domains, detect MSI executions, and harden web applications against iframe injection.
Read briefing
Chromium CVE‑2026‑95356: Use‑After‑Free in WindowDialog
A use‑after‑free flaw in Chromium’s WindowDialog component (CVE‑2026‑95356) can enable arbitrary code execution via malicious web content. Microsoft Edge, which incorporates Chromium, is affected until the patch is applied. Defenders should update to the latest Edge release and monitor for anomalous browser activity.
Read briefing
Brevo Supply‑Chain Breach: Cloudflare Key Theft Fuels ClickFix Malware Injection
Brevo’s hard‑coded Cloudflare API key fell into attackers’ hands, enabling a malicious Cloudflare Worker that ran for over five hours on September 14. The worker injected ClickFix scripts into Brevo’s own sites and the JavaScript libraries customers embed on their pages, distributing a backdoor WordPress plugin and other malware. Affected sites include brevo.com, sendinblue.com, and several customer‑facing URLs. Brevo quickly revoked the key, removed the Worker, and purged edge caches, but up to 100 000 third‑party sites may have been compromised. The incident underscores the risk of embedding
Read briefing