
Vulnerabilities
BeyondTrust Remote Support Zero‑Day CVE‑2026‑102764 Exploited by Armory Castle
A China‑linked threat actor, Armory Castle, used a CVE‑2026‑102764 zero‑day in BeyondTrust Remote Support to compromise a self‑hosted appliance on August 29, 2026. The flaw allows remote file operations via improper origin validation. All SaaS customers are patched; self‑hosted users must apply BT26‑05‑RS or upgrade.
A single self‑hosted BeyondTrust Remote Support appliance was taken over on August 29, 2026 by the China‑linked group Armory Castle. The attack leveraged CVE‑2026‑102764, a CVSS 9.3 flaw that permits remote file manipulation through an internal messaging component that fails to validate message origin.
Impact
Compromise of the appliance grants the attacker full control, including the ability to deploy web shells such as SAWFLY. The breach potentially exposes all remote support sessions and any data transmitted through the affected device.
What to Do
- Verify if you run BeyondTrust Remote Support SaaS – all customers received a patch on October 9, 2026.
- Self‑hosted users of versions 24.3.1 through 26.2.3 must apply the BT26‑05‑RS patch immediately.
- Users on versions older than 24.3.1 must upgrade to a newer release that includes the fix.
- Conduct a rapid inventory of all Remote Support appliances, confirm patch status, and monitor for anomalous file operations or web shell activity.
Additional Context
Armory Castle has a track record of exploiting zero‑days in Citrix NetScaler, Ivanti Connect Secure, and other security devices to conduct long‑term espionage across multiple sectors.
Related vulnerabilities
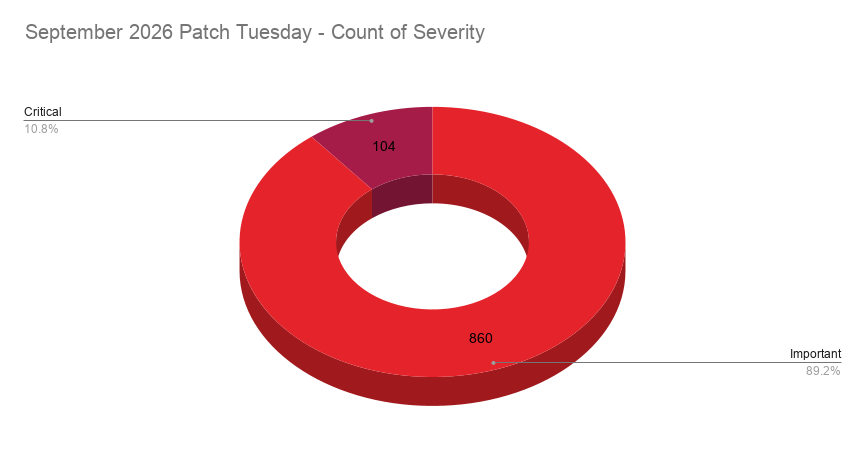
Microsoft September 2026 Patch Tuesday: 964 CVEs, Including Two Zero-Day Exploits (CVE-2026-81963, CVE-2026-85880)
Microsoft released its largest Patch Tuesday to date, addressing 964 CVEs—104 critical and 860 important—including two zero‑day vulnerabilities exploited in the wild. Defenders must prioritize applying updates to affected components such as .NET, Active Directory services, Azure services, Office, and Windows kernel drivers, and verify system integrity.
Read briefing
SAP Exposes Critical Kernel & Message Server Flaws: CVE-2026-44756 & CVE-2026-58240
SAP’s September Security Patch Day revealed two critical vulnerabilities that can be exploited remotely without authentication. The memory‑corruption flaw in SAP Extended Passport (OVERPASS, CVE‑2026‑44756) and the missing‑auth bug in NetWeaver Message Server (S4GET, CVE‑2026‑58240) both allow attackers to run arbitrary OS commands as the SAP installation user, risking full system takeover. Immediate application of SAP Security Notes 3747649 and 3759472 is mandatory.
Read briefing
OpenOffice Versions <4.1.17 Vulnerable to Remote Code Execution (CVE‑2026‑59265, CVE‑2026‑63277)
Multiple CVEs have been identified in OpenOffice versions older than 4.1.17 that enable remote code execution. The flaws allow an attacker to trigger arbitrary code on a target system via crafted documents. Defenders must apply the vendor’s patches immediately or upgrade to a supported release.
Read briefing
CVE‑2026‑83780: Windows CCFFilter Driver Remote Code Execution via Use‑After‑Free
Microsoft has disclosed a remote code execution flaw in the CCFFilter driver (CVE‑2026‑83780). The vulnerability, triggered by a use‑after‑free condition, can be exploited over the network by an unauthenticated attacker. Defenders should apply the latest security update, disable the driver on vulnerable systems, and enforce network segmentation.
Read briefing