
Vulnerabilities
BragJack: Malicious Extension Hijacks AI Browser Assistants
A proof‑of‑concept attack named BragJack demonstrates how a single malicious browser extension can hijack AI assistants in Chrome, Edge, Opera Neon, Perplexity Comet, and Claude in Chrome. The technique abuses browser‑level privileges, allowing the attacker to read data and act on the user’s behalf without interaction. Defenders should remove suspicious extensions, enforce strict extension policies, and keep browsers updated.
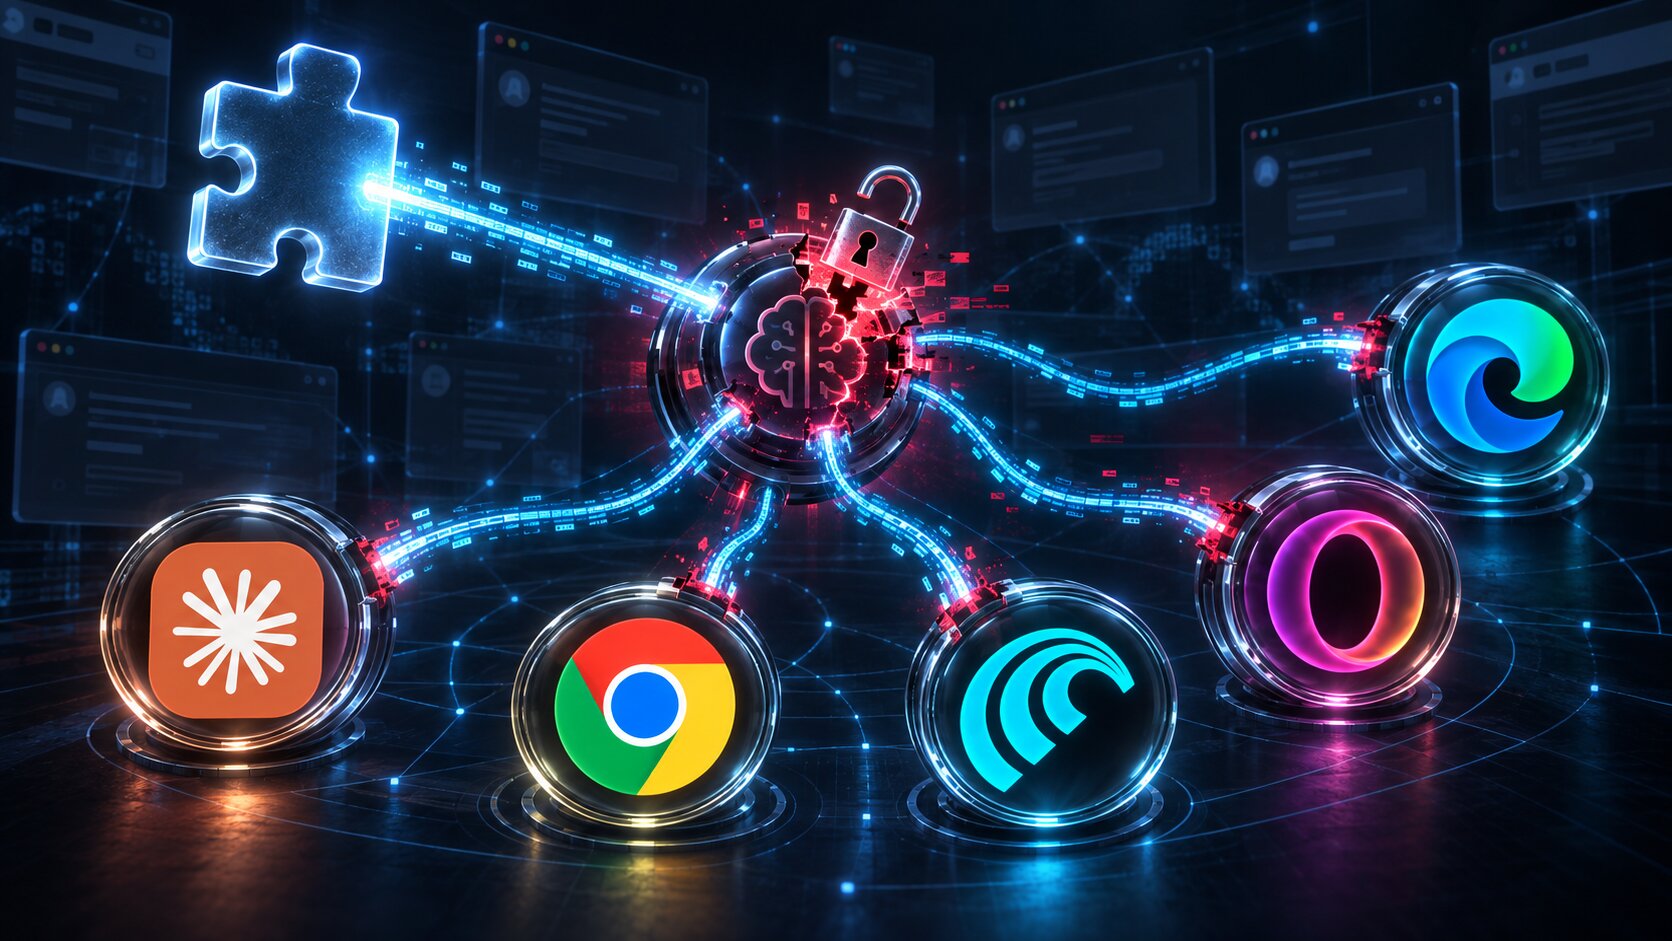
BragJack is a proof‑of‑concept that shows a malicious extension can take control of AI assistants built into Chromium‑based browsers.
What Happened
The attacker installs a single extension that, once present, can issue commands to the AI assistant and leverage its browser privileges. The proof‑of‑concept targeted Gemini Live in Chrome, Microsoft Edge, Opera Neon, Perplexity Comet, and Claude in Chrome.
Affected Systems
- Google Chrome (Gemini Live)
- Microsoft Edge
- Opera Neon
- Perplexity Comet
- Claude in Chrome
Impact
Once hijacked, the AI assistant can read or exfiltrate sensitive data, execute arbitrary browser actions, and act on the user’s behalf without any additional interaction.
What to Do
- Audit and remove any untrusted or unknown extensions.
- Configure browsers to allow extensions only from verified sources.
- Keep browsers and extensions up to date; vendors have patched the CVEs.
- Monitor for unusual AI assistant activity and restrict its permissions where possible.
Related vulnerabilities
CVE-2026-70190: .NET Elevation of Privilege Vulnerability – No New Fix Required
CVE‑2026‑70190 is an elevation‑of‑privilege flaw in .NET 11.0 that was already addressed in earlier releases. Microsoft has updated its Security Updates table to include KB article links for .NET 11.0 and Visual Studio, but the fixed builds remain unchanged. Defenders should confirm that their systems run the latest patched .NET 11.0 and Visual Studio versions and apply any pending KB updates.
Read briefing
Multiple RCE, Data Breach, and DoS Vulnerabilities in F5 NGINX Products
F5 has disclosed multiple critical vulnerabilities affecting its NGINX-based products, including remote code execution, data confidentiality and integrity compromise, and denial‑of‑service. Affected versions span F5 DoS for NGINX 4.x <4.11.0, F5 WAF for NGINX 5.x <5.16.0, and several other NGINX components. Defenders should verify product versions, apply vendor patches, and monitor for anomalous activity.
Read briefing
CISA Adds Four Exploited Vulnerabilities to KEV Catalog
CISA has added four CVEs—CVE‑2026‑0322, CVE‑2026‑76519, CVE‑2026‑105133, CVE‑2026‑105134—to its Known Exploited Vulnerabilities catalog. The vulnerabilities affect Palo Alto Networks PAN‑OS, Cisco Secure Email Gateway, and Ahsay AhsayCBS, and grant attackers full control of exposed assets. Defenders should prioritize patching and verify no compromise before applying updates.
Read briefing
CVE-2026-102850: Microsoft Office Access Remote Code Execution via Heap Overflow
A heap‑based buffer overflow in Microsoft Office Access (CVE‑2026‑102850) allows an unauthenticated attacker to execute code over a network. The flaw can be triggered by a crafted Access file. Defenders should apply the latest Office updates immediately and consider disabling Access on untrusted networks.
Read briefing