
Threat Intel
Chinese Espionage Group Deploys New SparroWocky Backdoor in Latin America
FamousSparrow, a China‑linked threat actor, has moved beyond its old SparrowDoor tool and rolled out the modular C++ backdoor SparroWocky against government entities across Latin America. The malware uses sophisticated anti‑analysis tricks—DLL side‑loading, RC4‑encoded payloads, dynamic API resolution, and CreateThread hooking—to evade detection. It can execute commands, exfiltrate data, capture high‑frequency screenshots, proxy traffic, and even wipe its own traces. ESET’s analysis pinpoints 18 C2 endpoints and shows the operation has been active for over a year, targeting Argentina, Ecuador,
Chinese‑linked espionage outfit FamousSparrow has shifted its attack toolkit, replacing its older SparrowDoor backdoor with a new, more stealthy weapon called SparroWocky. The move has been in play for more than a year and has focused on government organizations across Latin America.
What SparroWocky Can Do
- Execute arbitrary commands and launch executables.
- Load and run Beacon Object Files entirely in memory.
- Harvest system, network, user, domain, and Windows version details.
- Enumerate drives, directories, files, displays, and active user sessions.
- Upload, download, copy, move, rename, and delete files.
- Take screenshots every 500 ms, sending only changed screen regions after the first full image.
- Create processes in other logged‑in users’ sessions.
- Act as a TCP proxy and forward connections.
- Remove its own persistence and delete its files to clean up evidence.
Stealthy Delivery and Evasion
SparroWocky is delivered via DLL side‑loading. A loader decrypts an RC4‑encoded payload stored in a .dat file and maps it directly into memory, bypassing file‑based detection. The malware then employs a suite of evasion tactics:
- Call‑stack and threat‑origin spoofing.
- Dynamic API resolution.
- Disguising in‑memory code and DLLs as legitimate Windows components.
- Hooking the CreateThread API with the MinHook library so that threads appear to start at the harmless AnimateWindow function, tricking security products.
Persistence Mechanisms
- Registers itself as a Windows service named
ProcAuditManager. - Creates a registry key (
SnapCart) under HKLM or HKCU, depending on privilege level.
Command‑and‑Control Profile
At least 18 C2 addresses have been identified, communicating over port 443 or 8080, or via HTTP and SOCKS5 proxies. The traffic is predominantly HTTPS, making it harder for perimeter defenses to flag.
Target Landscape
From mid‑2025 onward, the focus has been on Latin American governments: Argentina, Ecuador, Guatemala, Honduras, Panama, Peru, Puerto Rico, and Venezuela. The objective appears to be gathering intelligence on how these governments respond to increasing U.S. pressure on Chinese economic interests.
Defensive Takeaway
Security teams should add the listed indicators of compromise to their detection rules, monitor for unusual screenshot activity, and watch for DLL side‑loading patterns. Keeping host‑based EDRs updated and enforcing strict DLL signing policies can help blunt the attack surface.
Related articles
Chinese‑speaking gang hijacks Brazilian government sites to weaponise SEO for phishing and gambling scams
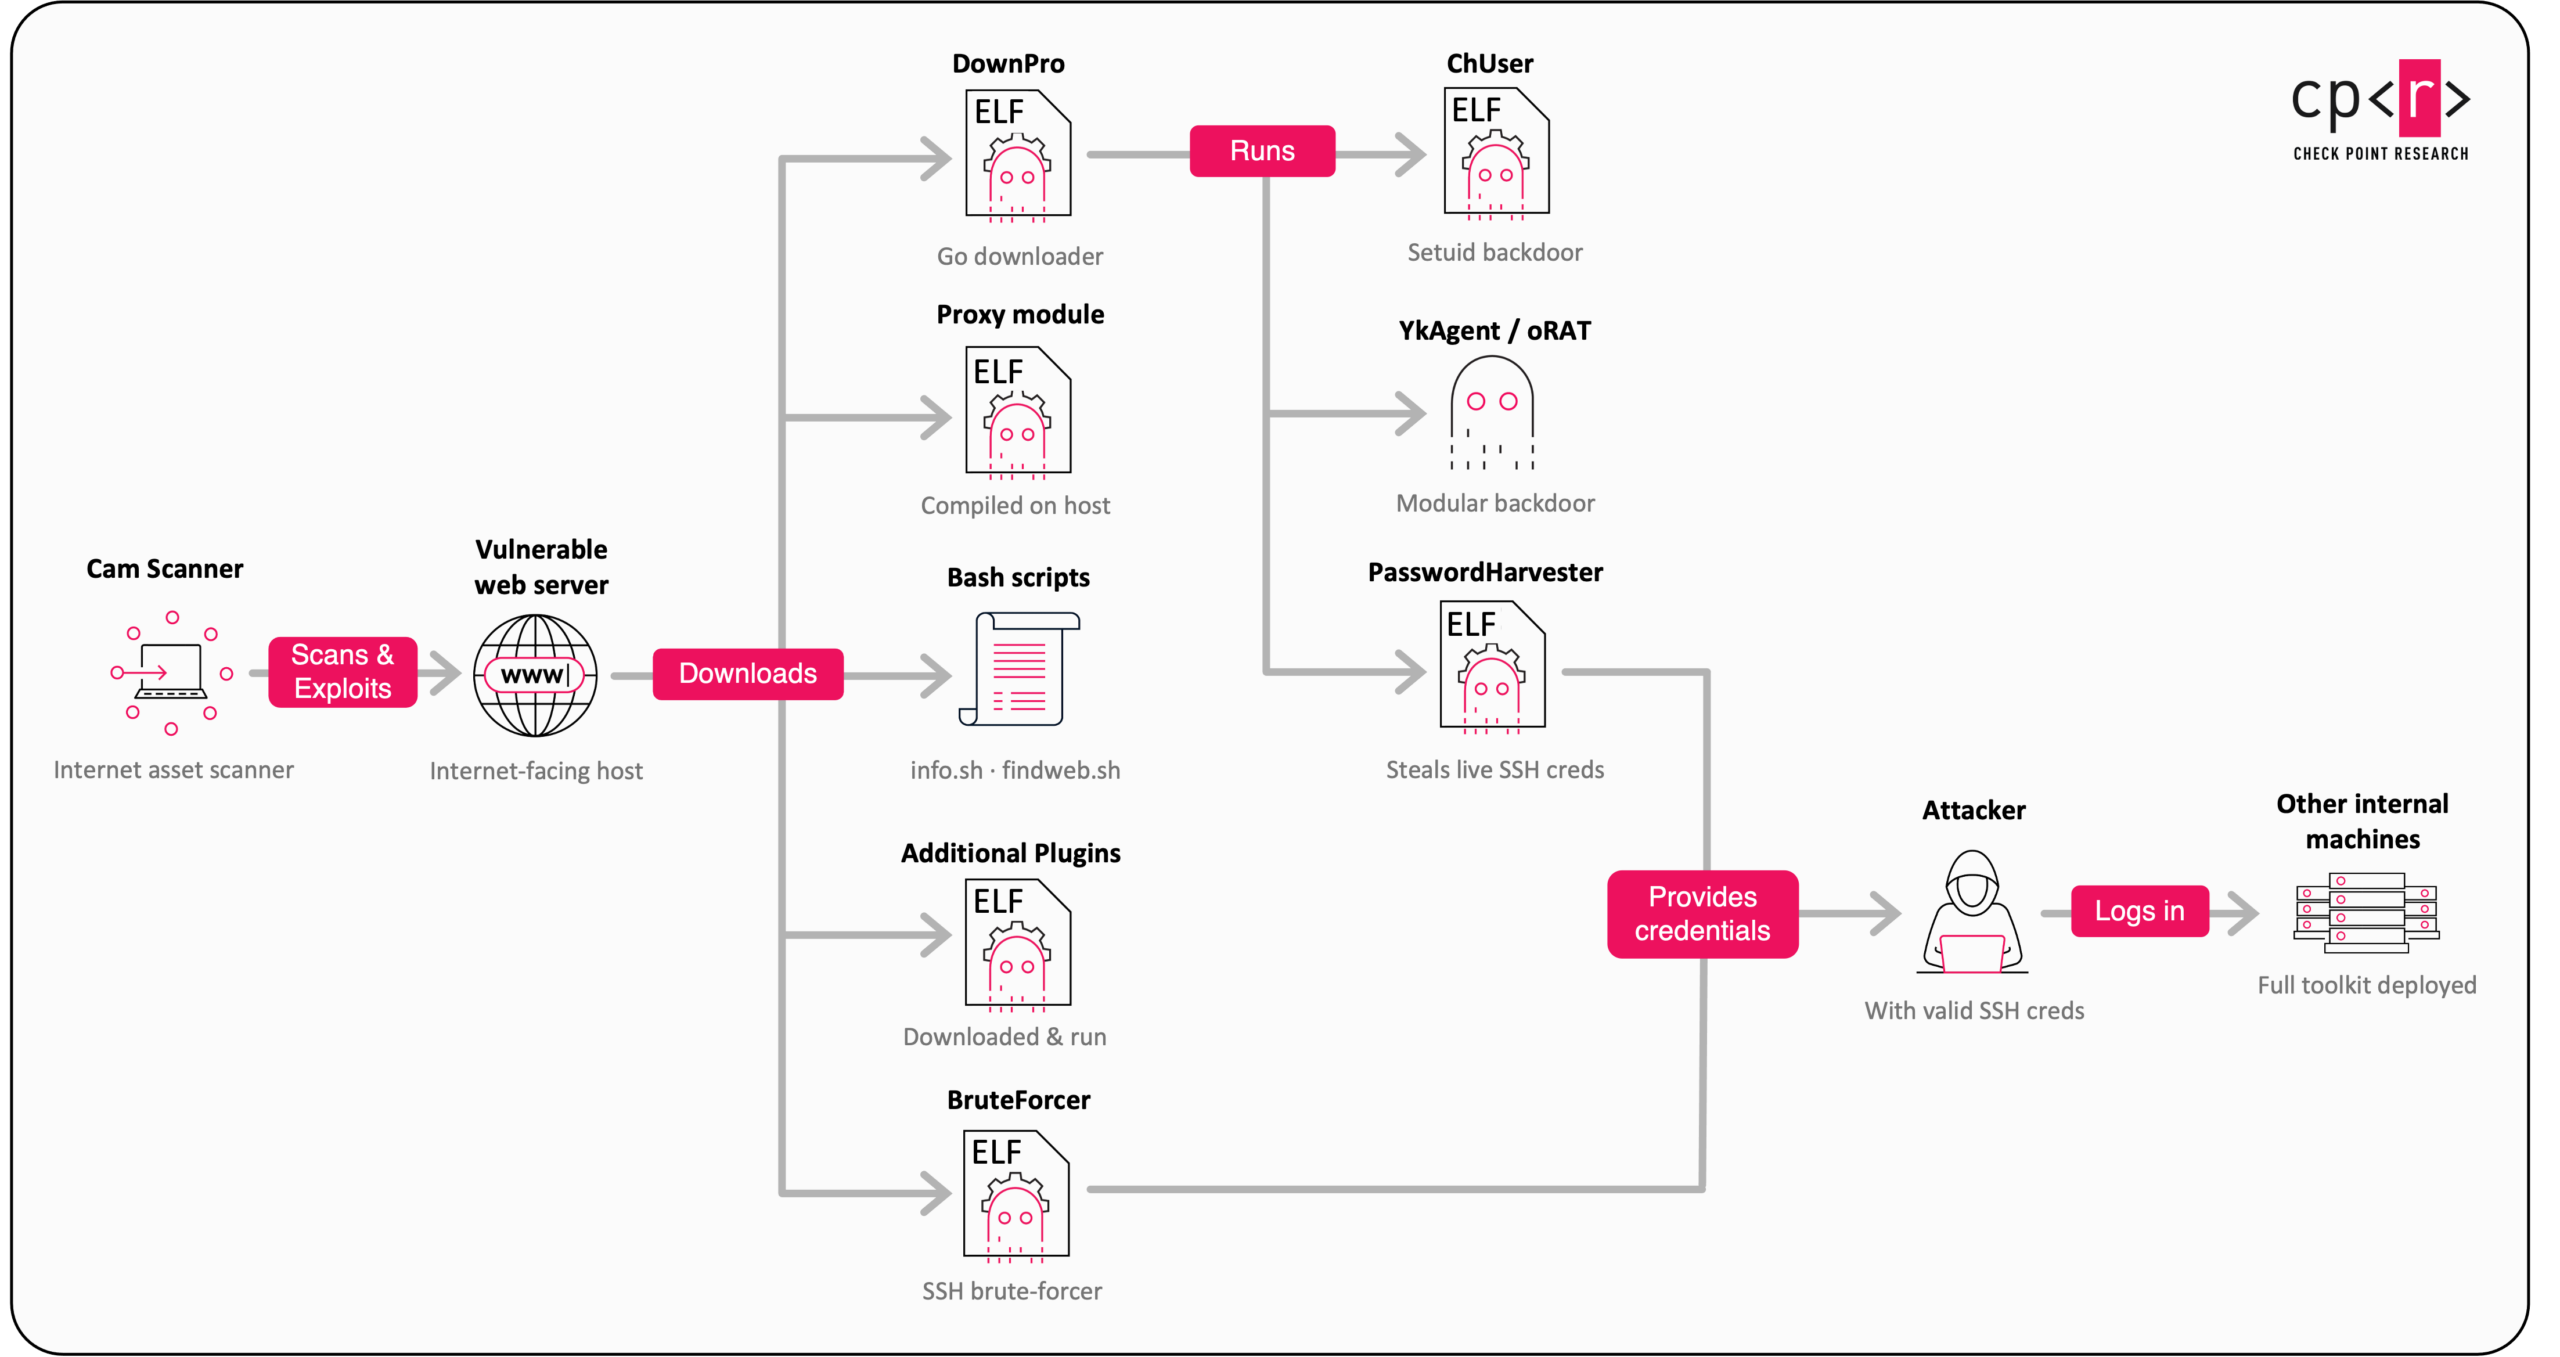
Since mid‑2025, a Chinese‑speaking cyber‑crime cluster dubbed Gambling Goblin has been infiltrating Brazilian government and educational web servers. By installing custom Apache modules, the attackers silently reverse‑proxy visitors to a vast network of phishing pages that masquerade as trusted app stores. The compromised high‑reputation domains are then leveraged to boost the attackers’ own content in search results, driving traffic to gambling and sports‑betting sites. The group deploys a heavily obfuscated Linux toolkit—including backdoors, credential stealers and reconnaissance agents—maki
Read briefing
CrowdStrike Deploys On‑Device AI for Real‑Time Data Classification in Falcon Data Security
CrowdStrike, in partnership with Intel, has unveiled a next‑generation feature for Falcon Data Security that leverages on‑device language models running on dedicated AI hardware. The new capability instantly tags and classifies sensitive information—such as PII, PHI, and financial data—directly on endpoints, eliminating the need to ship raw data to the cloud. This reduces latency, preserves privacy, and tightens compliance controls while maintaining the same high detection accuracy that Falcon is known for. The move underscores CrowdStrike’s commitment to edge‑AI security and sets a new standa
Read briefing
North Korean APT Breaches South Korean Media and Auto Firms via New Linux Toolkit on HAProxy Load Balancers
A suspected North Korean APT deployed a previously undocumented Linux espionage toolkit, dubbed "TED," to compromise HAProxy load balancers in South Korean media and automotive companies. The attackers leveraged the compromised appliances to harvest credentials, redirect traffic, and execute drive‑by downloads, fitting the DPRK pattern of long‑term espionage via trusted software. Rapid7 links the activity to APT37 with medium confidence, highlighting the dual focus on information control and manufacturing IP.
Read briefing
BambooToken Malware Exploits MQTT to Command Windows and Linux Systems
A stealthy, previously unknown malware family called BambooToken has been active since 2023 and now leverages the MQTT protocol for command‑and‑control. The framework infects Windows and Linux hosts via side‑loading signed USB‑token software or by masquerading as the Kingsoft Office suite, then subscribes to broker topics to receive instructions. Researchers uncovered dead code hinting at keylogging, clipboard theft, and media capture, while the latest Linux variant (v2.1) can spawn shells and move files. Roughly a dozen enterprises—mostly in Asia and South America—were hit, with mobile‑app ba
Read briefing