
Threat Intel
Chinese‑speaking gang hijacks Brazilian government sites to weaponise SEO for phishing and gambling scams
Since mid‑2025, a Chinese‑speaking cyber‑crime cluster dubbed Gambling Goblin has been infiltrating Brazilian government and educational web servers. By installing custom Apache modules, the attackers silently reverse‑proxy visitors to a vast network of phishing pages that masquerade as trusted app stores. The compromised high‑reputation domains are then leveraged to boost the attackers’ own content in search results, driving traffic to gambling and sports‑betting sites. The group deploys a heavily obfuscated Linux toolkit—including backdoors, credential stealers and reconnaissance agents—maki
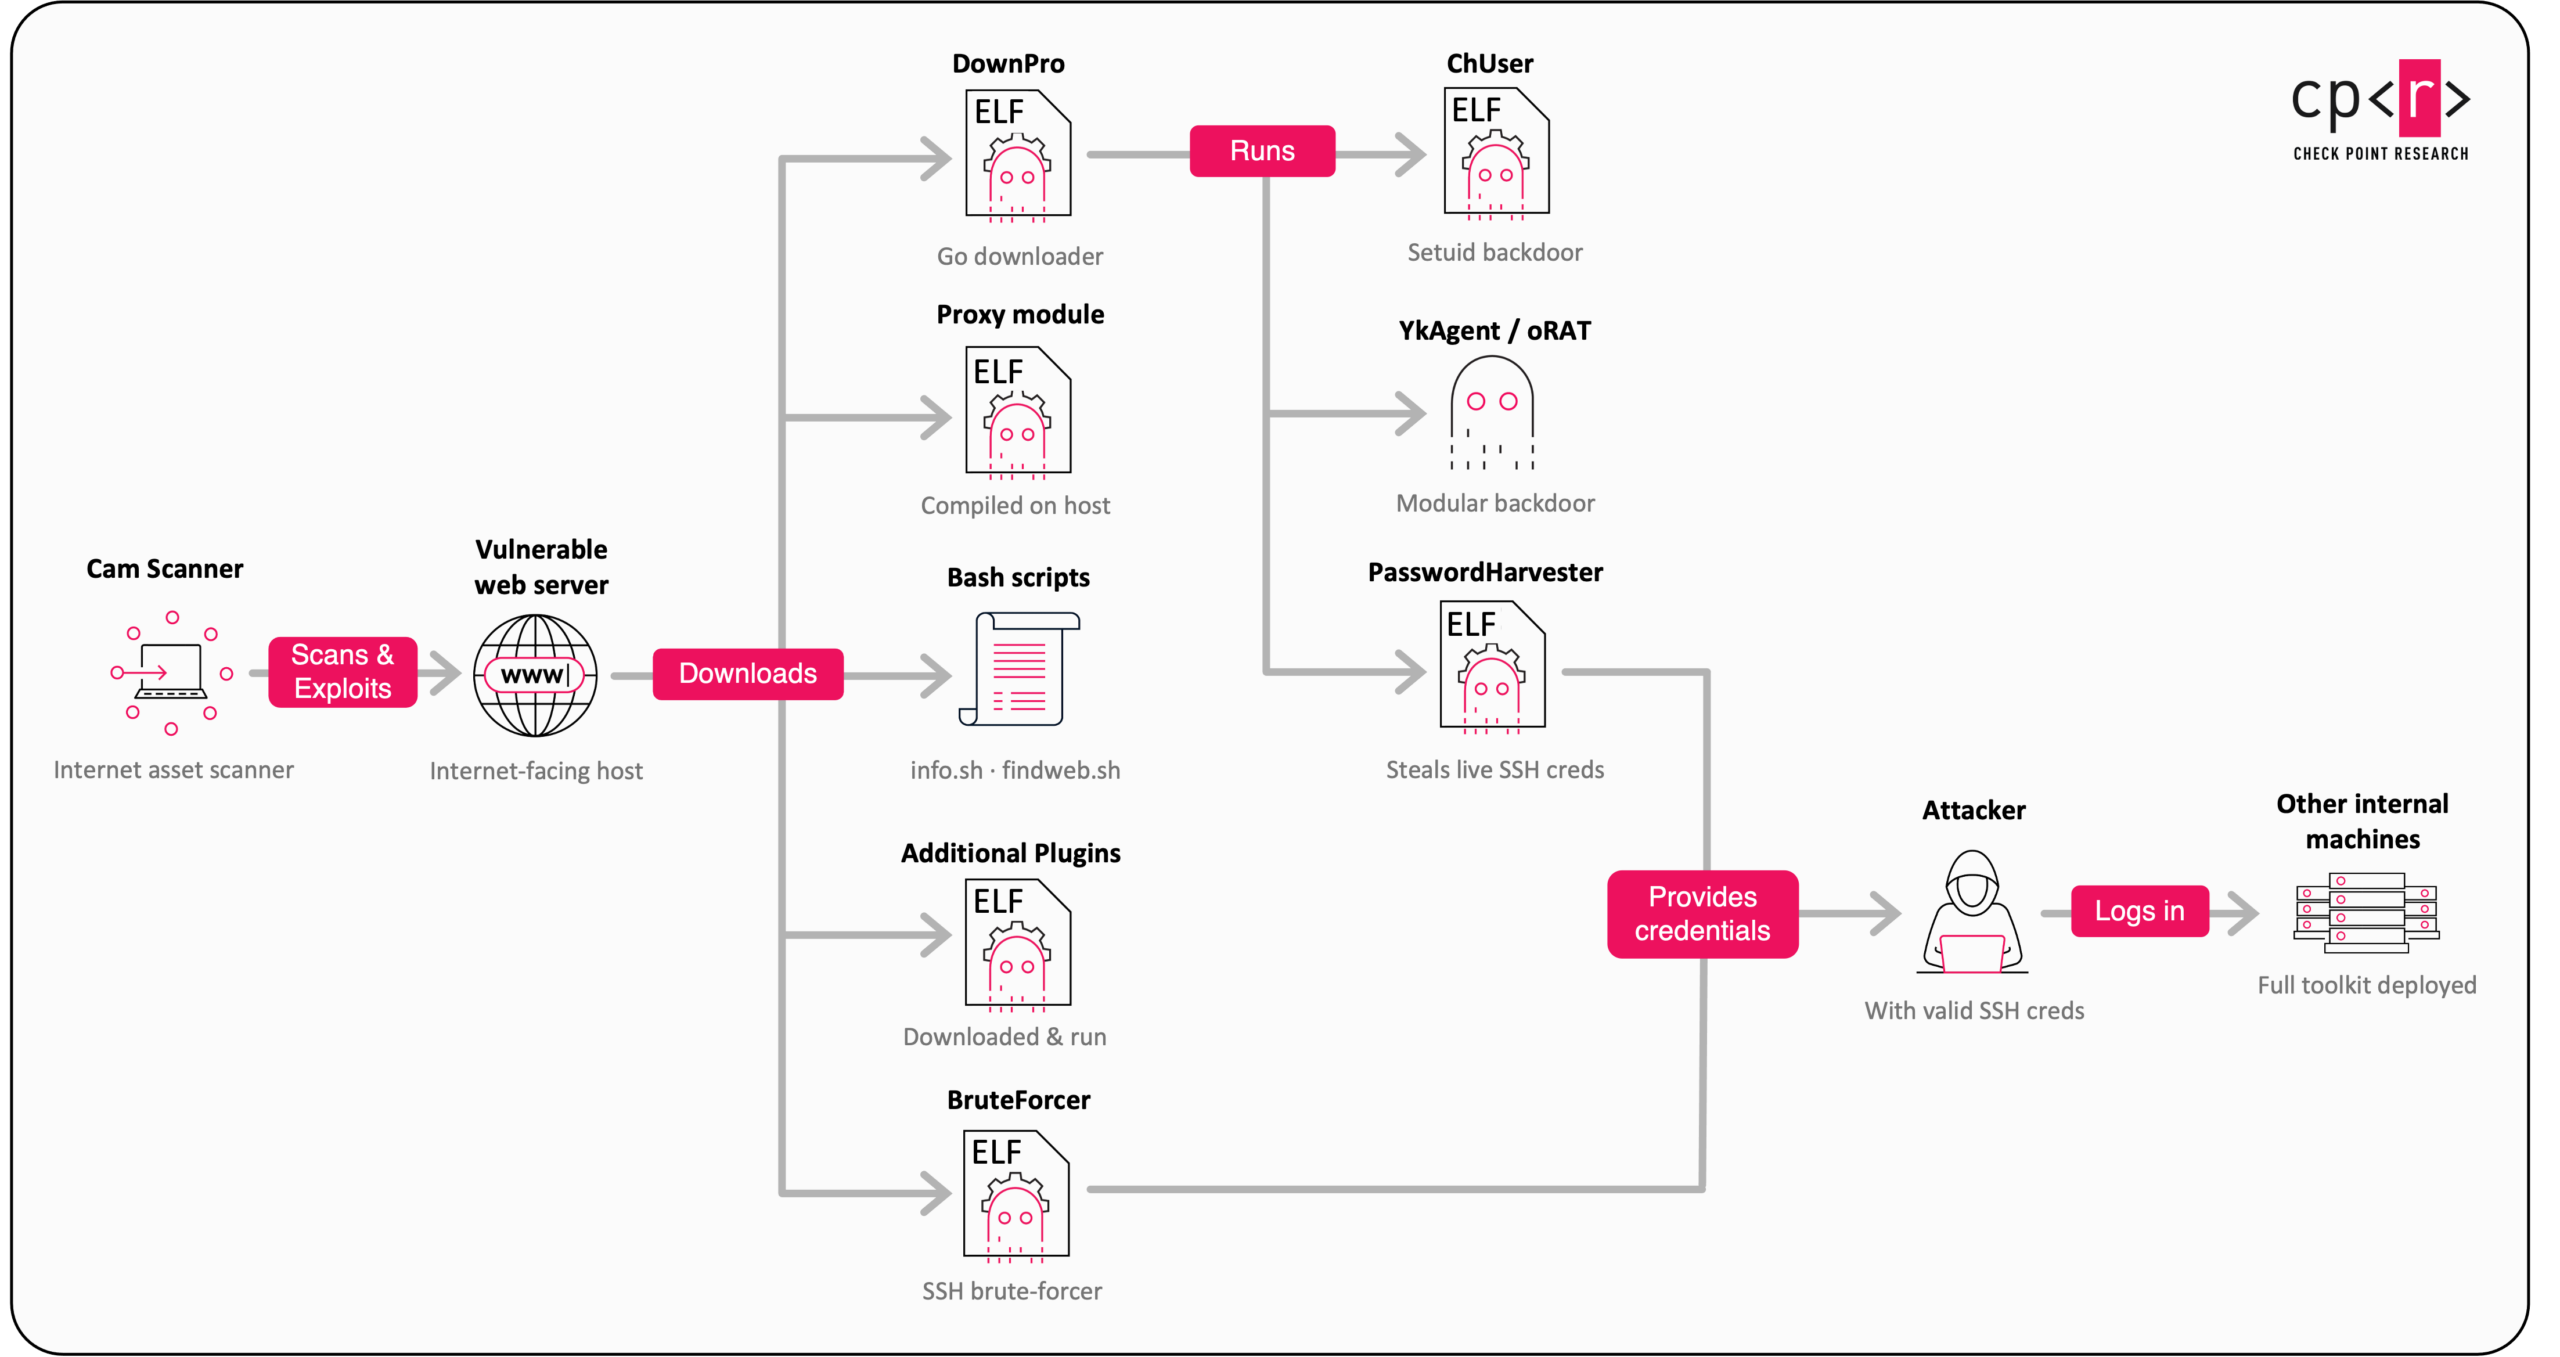
Since the summer of 2025, Check Point Research has been tracking a persistent campaign that targets Brazilian government and educational institutions. The operation is run by a Chinese‑speaking cyber‑crime cluster that Check Point has dubbed Gambling Goblin, linked to the earlier Earth Berberoka group that once focused on Asian gambling sites.
How the Attack Works
Once inside a victim’s web server, the gang drops a custom Apache module that quietly acts as a reverse‑proxy. Visitors to the legitimate domain are silently redirected to a sprawling set of phishing pages hosted on the compromised servers. Because the traffic still appears to come from the original, reputable domain, search engines and users are tricked into trusting the content.
The phishing pages are designed to look like legitimate app‑store destinations – Google Play, Microsoft Store, Amazon – and then push users toward online gambling and sports‑betting offers. The attackers chain together dozens of high‑reputation Brazilian government sites, inflating their search rankings and hijacking legitimate traffic at scale.
Toolset and Tradecraft
- Custom downloader (DownPro) that fetches additional payloads.
- Modular backdoors such as AlphaAgent and the oRAT RAT.
- A 3‑snake‑based credential stealer that harvests usernames and passwords.
- SSH brute‑forcers and a plugin‑driven reconnaissance agent.
- All components are heavily obfuscated with layered virtualization and packing to slow analysis and evade detection.
SEO Manipulation & Future Threat
By exploiting the authority of government domains, Gambling Goblin can manipulate search engine rankings, making their phishing pages appear higher in search results. The same infrastructure is already being used to run parallel phishing campaigns in Vietnamese, Spanish and English, indicating a design for rapid geographic expansion.
Because the phishing pages already mimic app‑store downloads, the attackers are only a configuration change away from delivering malware directly to victims. This latent escalation risk means the operation could shift from search‑fraud to a full‑blown malware campaign at any time.
"The attackers are turning trusted domains into stealthy proxies, effectively turning the web into an SEO weapon," said Amit Yardeni, Check Point Research.
Related articles
Chinese Espionage Group Deploys New SparroWocky Backdoor in Latin America
FamousSparrow, a China‑linked threat actor, has moved beyond its old SparrowDoor tool and rolled out the modular C++ backdoor SparroWocky against government entities across Latin America. The malware uses sophisticated anti‑analysis tricks—DLL side‑loading, RC4‑encoded payloads, dynamic API resolution, and CreateThread hooking—to evade detection. It can execute commands, exfiltrate data, capture high‑frequency screenshots, proxy traffic, and even wipe its own traces. ESET’s analysis pinpoints 18 C2 endpoints and shows the operation has been active for over a year, targeting Argentina, Ecuador,
Read briefing
Black Axe Syndicate Leaders Extradited to U.S. on Wire Fraud and Money Laundering Charges
Five alleged leaders of the notorious Black Axe cybercrime gang were flown from South Africa to the United States on September 11 to face wire‑fraud, money‑laundering and aggravated identity‑theft charges. Prosecutors say the group ran a decade‑long romance‑scam scheme that tricked U.S. victims into sending money, using social‑media profiles, dating sites and VoIP calls. The extradition follows a global operation that saw 58 arrests across 22 countries, highlighting the U.S. commitment to bring transnational fraudsters to justice.
Read briefing
PhantomRaven: Bug‑Bounty Hunter Turns AI‑Generated Stealer Into Profit Machine
A financially motivated threat actor, posing as a bug‑bounty hunter, has crafted and distributed the JavaScript‑based information stealer PhantomRaven. Leveraging large‑language‑model code generation, the tool harvests credentials, session tokens and other sensitive data from compromised web pages. CrowdStrike’s analysis reveals the actor’s distribution tactics, the malware’s persistence mechanisms, and actionable detection and mitigation steps for defenders.
Read briefing
PhantomRaven: LLM‑Powered JavaScript Stealer Created by a Bug‑Bounty Hunter
CrowdStrike has exposed PhantomRaven, a JavaScript‑based information stealer crafted with large language model techniques and distributed by a financially motivated threat actor who pretends to be a bug‑hunter. The malware siphons credentials, session tokens, and other sensitive data from web apps, leveraging the same expertise used to discover and report bugs. RootPwn breaks down how LLMs are enabling rapid, low‑cost stealers and outlines the signs defenders should watch for.
Read briefing