
Advisories
Denmark CPR Data Breach: 8.8M Records Exposed via Private Company Account
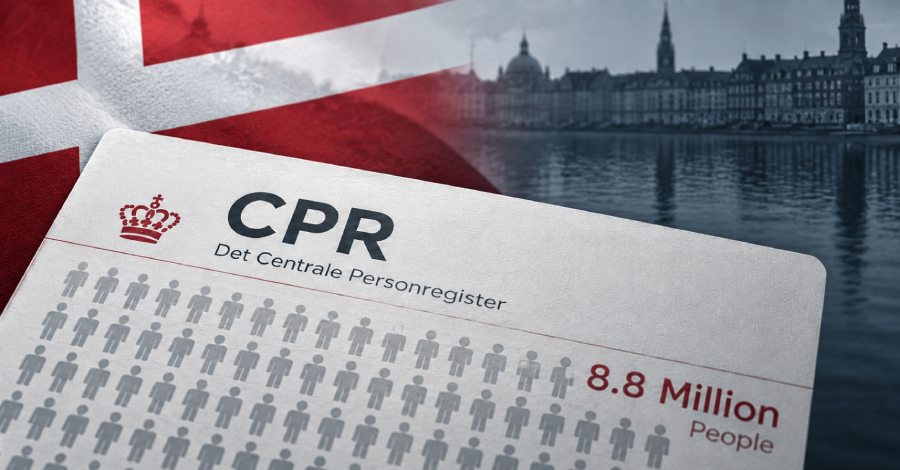
Unauthorized actors accessed names, addresses and CPR numbers for 8.8 million people in Denmark’s Central Person Register through a private company’s legitimate lookup account. The breach, lasting about ten days in September, exposed sensitive personal identifiers that can fuel identity theft.
What Happened
Between early September and mid‑September, unauthorized actors accessed the Central Person Register (CPR) through a private Danish company’s legitimate lookup account. Automated queries extracted names, addresses and CPR numbers for roughly 8.8 million individuals, including living residents, deceased persons and those who have left Denmark.
Impact
The breach covers about 80 % of the 11 million entries in the register. The exposed data includes unique personal identification numbers that can be used for identity theft, phishing, and targeted fraud.
What Defenders Should Do
- Verify that any third‑party access to national registers is strictly limited to authorized personnel and enforce least‑privilege.
- Audit logs for anomalous bulk lookups and set alerts for high‑volume queries.
- Ensure all credentials are stored in a password manager and use multi‑factor authentication for all privileged accounts.
- Notify affected users if you are a service that may have processed CPR data, and provide guidance on monitoring for identity‑theft.
Current Status
Denmark’s Digitalisation Ministry has disabled the company’s access, reported the incident to Datatilsynet, and police are conducting an investigation. The full list of compromised records is still being verified.
Related articles
Denmark CPR Registry Breach Exposes 8.8 Million Citizens' Personal Data
In September 2026 a breach of Denmark’s Central Population Register (CPR) exposed names, addresses, CPR numbers and other personal details for 8.8 million individuals. The attack leveraged a private company’s legitimate access and brute‑forced valid CPR identifiers. Defenders should audit access controls, monitor for credential misuse, and enforce MFA on registry interfaces.
Read briefing
Astrana Health Discloses Data Breach Stemming from Employee Social Engineering
Astrana Health reported a data breach impacting private and confidential records after attackers used targeted social engineering, including phone number spoofing, to impersonate internal personnel and access company servers. The healthcare management firm has enacted credential rotations, restricted remote access tools, and initiated system restorations from clean backups.
Read briefing
CenterPoint Energy Breach: 7.5 Million Customer Records Exposed via Unsecured Public API
Houston‑based utility CenterPoint Energy confirmed that an attacker stole and leaked 7.49 million customer records, including names, phone numbers, addresses, account numbers, billing amounts and partial SSNs. The intruder accessed the data by repeatedly querying a public API that lacked rate limiting, a web application firewall and other safeguards. CenterPoint has filed with the SEC, is working with third‑party experts, and has already faced class‑action lawsuits. The company reports that electric and gas services remain unaffected and believes the breach will not materially impact its finan
Read briefing
Frontline Education breach exposes school district employee data via third-party software flaw
Frontline Education told school districts that attackers used a vulnerability in a third-party application to access part of its environment and steal employee records, including Social Security numbers. The company identified the issue on August 14, 2026, remediated it, and engaged law enforcement, but has not named the affected product or the initial access date. Districts should treat the incident as a potential PII exposure and begin credential, identity, and monitoring follow-up.
Read briefing