
Advisories
MISP Hit by Cluster of Critical Vulnerabilities – Remote DoS, Data Breach, Integrity Flaws
French CERT has identified a wave of CVEs affecting all MISP releases older than 2.5.45. The flaws allow attackers to trigger remote denial‑of‑service, exfiltrate sensitive data, corrupt stored information, and exploit SSRF, XSS, and CSRF vectors. Patches are already available; operators must update immediately.
Security teams using the MISP threat‑intel platform should act fast. A series of CVEs discovered on 3 and 7 September 2026 expose the system to a range of attacks that can cripple services, leak confidential data, and corrupt the integrity of stored intelligence.
Key Risks
- Remote denial‑of‑service (DoS)
- Data confidentiality breach
- Data integrity compromise
- Server‑side request forgery (SSRF)
- Cross‑site scripting (XSS)
- Cross‑site request forgery (CSRF)
- Policy bypass and unauthorized request injection
Affected Versions
All MISP releases prior to 2.5.45 are vulnerable. The CVE list includes:
- CVE‑2026‑85216, 85221, 85226, 85227, 85230, 85236, 85237, 85238, 85239
- CVE‑2026‑86342, 86347, 86351
- CVE‑2026‑86408, 86417, 86418, 86419, 86440, 86441, 86452
Recommended Actions
- Immediately upgrade to the latest MISP release (≥ 2.5.45).
- Apply the vendor‑issued patches for the listed CVEs.
- Verify configuration settings to prevent SSRF and CSRF exploitation.
- Conduct a quick audit of stored data for signs of tampering.
- Monitor logs for unusual request patterns or denial‑of‑service attempts.
“Failure to patch MISP now could expose an entire threat‑intel ecosystem to compromise.” – CERT‑FR Advisory
Related vulnerabilities
Multiple RCE, Data Breach, and DoS Vulnerabilities in F5 NGINX Products
F5 has disclosed multiple critical vulnerabilities affecting its NGINX-based products, including remote code execution, data confidentiality and integrity compromise, and denial‑of‑service. Affected versions span F5 DoS for NGINX 4.x <4.11.0, F5 WAF for NGINX 5.x <5.16.0, and several other NGINX components. Defenders should verify product versions, apply vendor patches, and monitor for anomalous activity.
Read briefing
Critical Apache Zookeeper Vulnerabilities Threaten Data Integrity & Confidentiality – Patch Immediately
A batch of CVEs—CVE‑2026‑59739, ‑59969, ‑79993, ‑84439, ‑84501—has been uncovered in Apache Zookeeper 3.8.x (pre‑3.8.7) and 3.9.x (pre‑3.9.6). These flaws enable attackers to read sensitive data, tamper with stored values, and bypass security controls. Immediate patching and configuration hardening are required to mitigate the risk of data breaches and integrity violations.
Read briefing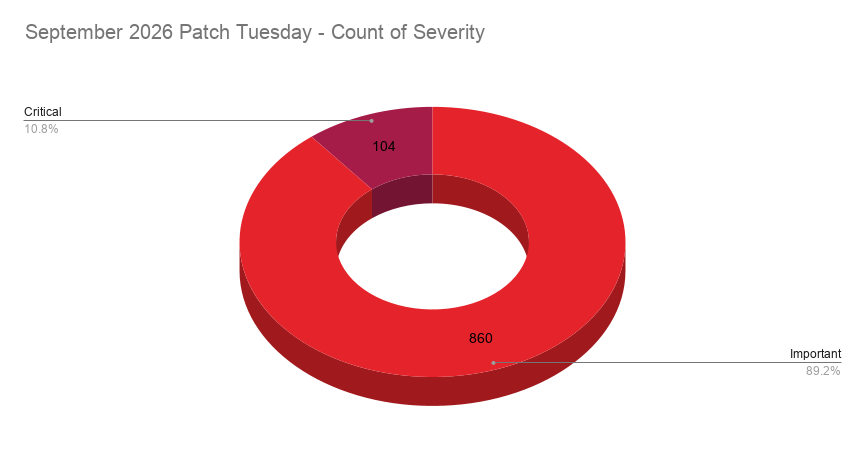
Microsoft September 2026 Patch Tuesday: 964 CVEs, Including Two Zero-Day Exploits (CVE-2026-81963, CVE-2026-85880)
Microsoft released its largest Patch Tuesday to date, addressing 964 CVEs—104 critical and 860 important—including two zero‑day vulnerabilities exploited in the wild. Defenders must prioritize applying updates to affected components such as .NET, Active Directory services, Azure services, Office, and Windows kernel drivers, and verify system integrity.
Read briefing
Mozilla Products Hit by 20+ Critical Vulnerabilities
The French CERT released an alert on September 16, 2026, detailing a suite of 22 CVEs affecting older releases of Firefox, Firefox ESR, Thunderbird, and Thunderbird ESR. The flaws enable attackers to elevate privileges, launch remote denial‑of‑service attacks, and exfiltrate sensitive data. Patches are available through Mozilla’s MFSA 2026‑90 to 2026‑95 advisories. All affected users should update immediately.
Read briefing