
Cybersecurity
Mobile App Permissions Continue to Pose Security Risks for Organizations
Recent analysis shows that mobile apps still request excessive permissions, exposing devices to privacy and security threats. Defenders should audit permission requests, enforce least‑privilege policies, and monitor for anomalous usage. Implementing device‑policy controls and user education can mitigate risks.
What Happened
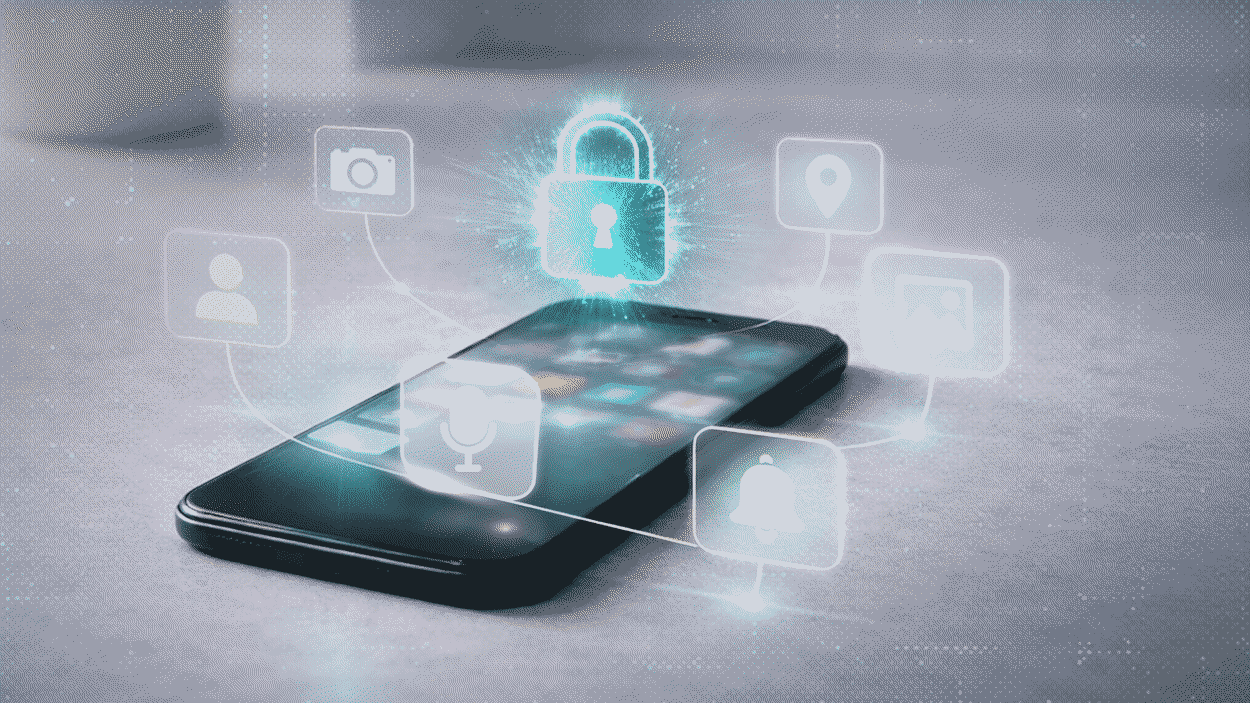
When users install or enable features in mobile apps, the OS presents permission dialogs. Android 6.0+ separates normal and dangerous permissions; iOS surfaces all sensitive permissions at runtime. Many apps request more than they need, including background location, microphone, contacts, and notifications.
Permissions are the gatekeepers of device data.
Impact
Excessive permissions can lead to data leakage, unauthorized tracking, and privilege escalation. Attackers can exploit mis‑configured permissions to exfiltrate personal data or gain persistence on a device.
What Defenders Should Do
Audit the permission sets of all deployed apps, enforce least‑privilege, and block or restrict unnecessary permissions via MDM or device‑policy tools. Monitor for anomalous permission usage and educate users about the risks of granting all prompts.
Mitigation Steps
- Use mobile‑device‑management (MDM) to control permission grants.
- Implement app‑whitelisting and restrict background location.
- Configure OS settings to require explicit user consent for sensitive data.
- Deploy SIEM to flag unusual permission changes.
- Provide regular training on safe permission practices.
Related articles
Enterprise AI Shifts to Risk Management: Governance, Cybersecurity, and Workforce Readiness Become Critical
As AI moves from experimentation to enterprise-wide deployment, organizations face new execution risks. CompTIA research shows cybersecurity concerns rank second to human‑AI balance, highlighting the need for governance structures, robust security practices, and workforce training. Defenders should prioritize AI‑specific risk frameworks, secure integration, and staff readiness.
Read briefing
Hirudo Android Malware Hijacks Banking Apps to Steal Credentials
Hirudo is an Android malware that replaces legitimate banking apps with malicious copies, disabling security checks to harvest credentials and remotely control devices. It targets banks in Indonesia, China, India, Mexico, Morocco, and Thailand, and is delivered via apps that masquerade as shopping or entertainment services. Defenders should verify app signatures, enforce Play Integrity, restrict Accessibility permissions, and deploy mobile security solutions to detect hooking engines.
Read briefing
Group-IB Launches Attack Surface Management to Counter Shadow IT Risks
Group-IB’s new Attack Surface Management tool helps defenders map and secure external assets, mitigating shadow IT risks. It integrates with existing security stacks and delivers real‑time threat intelligence. Defenders should assess their external footprint, enforce policies, and monitor for anomalies.
Read briefing
2026 Cybersecurity Reset: How to Rebuild Resilience with Unified Risk Platforms
Security teams must adapt to AI‑driven attacks, supply‑chain threats, and cloud misconfigurations. A Unified Risk Platform, integrated XDR, and real‑time threat intel can close visibility gaps and reduce dwell time. Follow these steps to align strategy with emerging risks.
Read briefing