
Threat Intel
Signed PUP Exploits Update Mechanism to Deploy AV Killers with SYSTEM Privileges
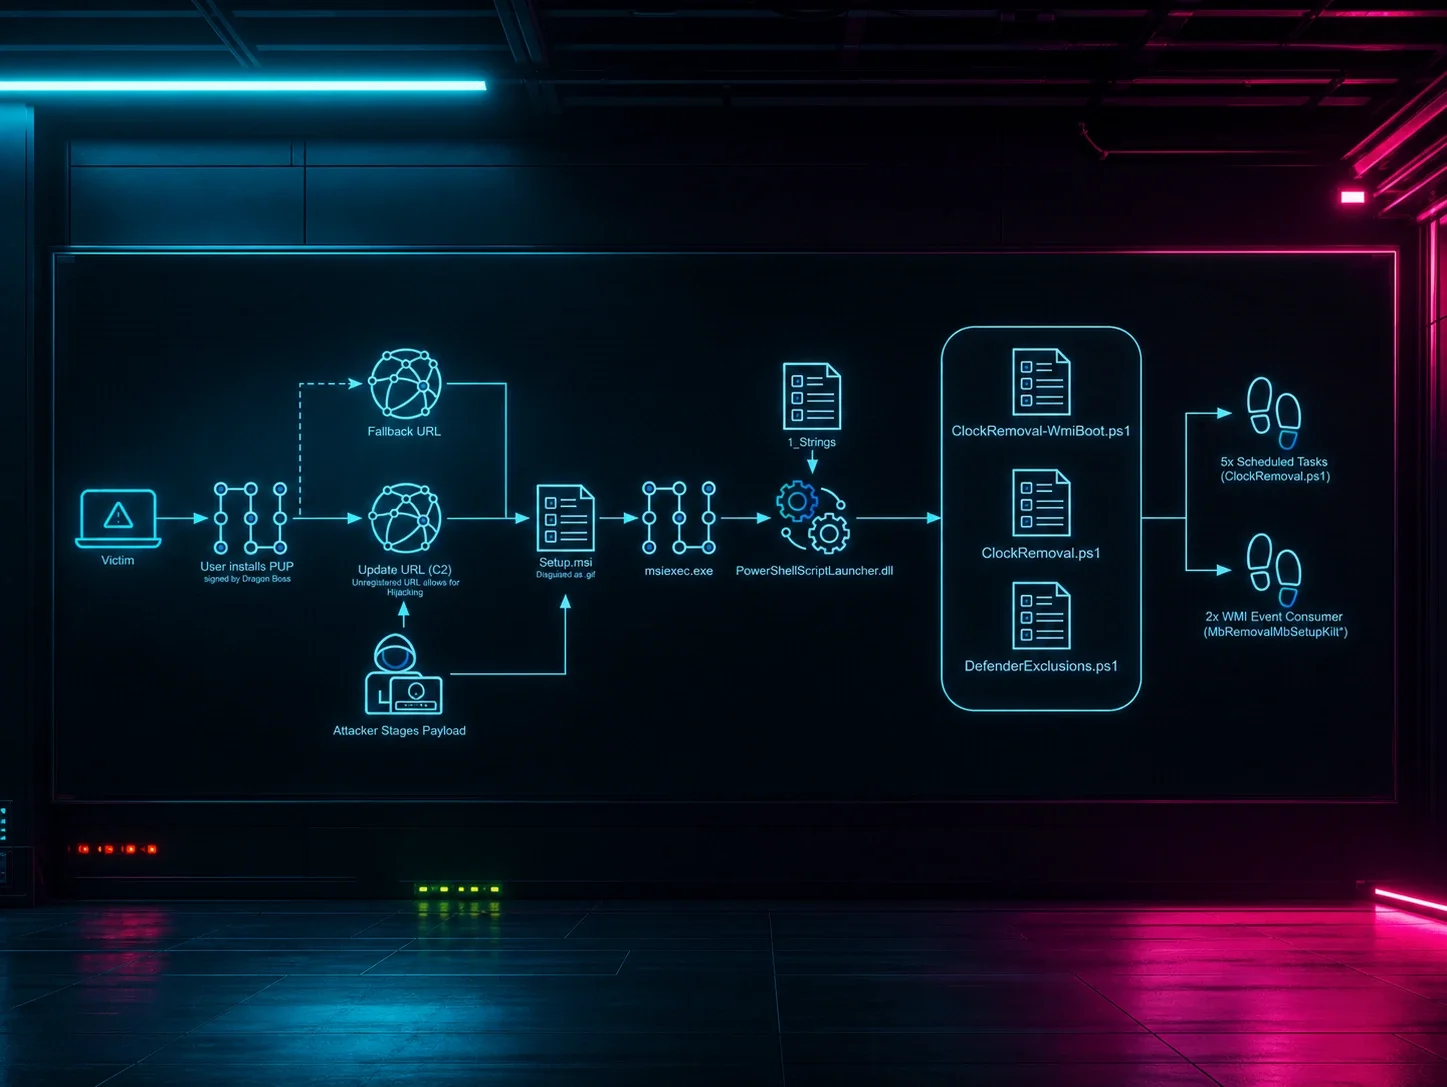
Huntress identified a malware campaign that leverages a signed potentially unwanted program (PUP) to install antivirus‑killers with SYSTEM rights. The operation abuses the software’s update channel, allowing attackers to gain full control over endpoints. Defenders should audit signed binaries, monitor privileged process creation, and enforce least‑privilege update mechanisms.
What happened
Huntress discovered a malware operation that uses a signed PUP to deliver antivirus‑killer payloads. The PUP is distributed through a legitimate update mechanism, which the attackers hijack to inject malicious code that runs with SYSTEM privileges.
Impact
- Full SYSTEM access to compromised endpoints.
- Ability to disable or bypass endpoint protection solutions.
- Potential lateral movement across the network.
How to detect
- Watch for unexpected signed binaries that are not part of known vendor releases.
- Monitor for new processes that spawn with SYSTEM rights and target AV components.
- Check update logs for anomalies or missing digital signatures.
Mitigations
- Validate the integrity of all signed installers and updates using hash checks.
- Implement application whitelisting and restrict update channels to trusted sources.
- Enforce least‑privilege for update processes; run them under non‑SYSTEM accounts.
- Deploy endpoint detection that flags privileged process creation and AV‑killer patterns.
- Keep all endpoint protection software up to date and monitor for disabled or stopped services.
'If the update mechanism can be hijacked, the entire endpoint is compromised.'
Related vulnerabilities
EDR Killers: How Attackers Exploit Drivers to Disable Endpoint Detection
ESET researchers analyzed nearly 90 EDR‑killer tools used in ransomware campaigns, revealing that attackers routinely deploy vulnerable drivers or driverless tactics to suspend or block EDR software before launching encryption. The study shows driver reuse across unrelated toolsets and highlights the pitfalls of attributing attacks solely by driver signatures. Defenders should monitor driver installation, block unauthorized driver loads, and enforce EDR integrity checks.
Read briefing
TrendAI Apex One Security Agent Local Privilege Escalation via Cache Mechanism (CVE-2025-71416)
TrendAI Apex One Security Agent is vulnerable to a local privilege escalation that allows an attacker with low‑privileged code execution to gain root privileges. The flaw stems from missing cache key validation during signature verification. Defenders should apply the vendor‑issued patch immediately and verify that the Apex One agent is updated.
Read briefing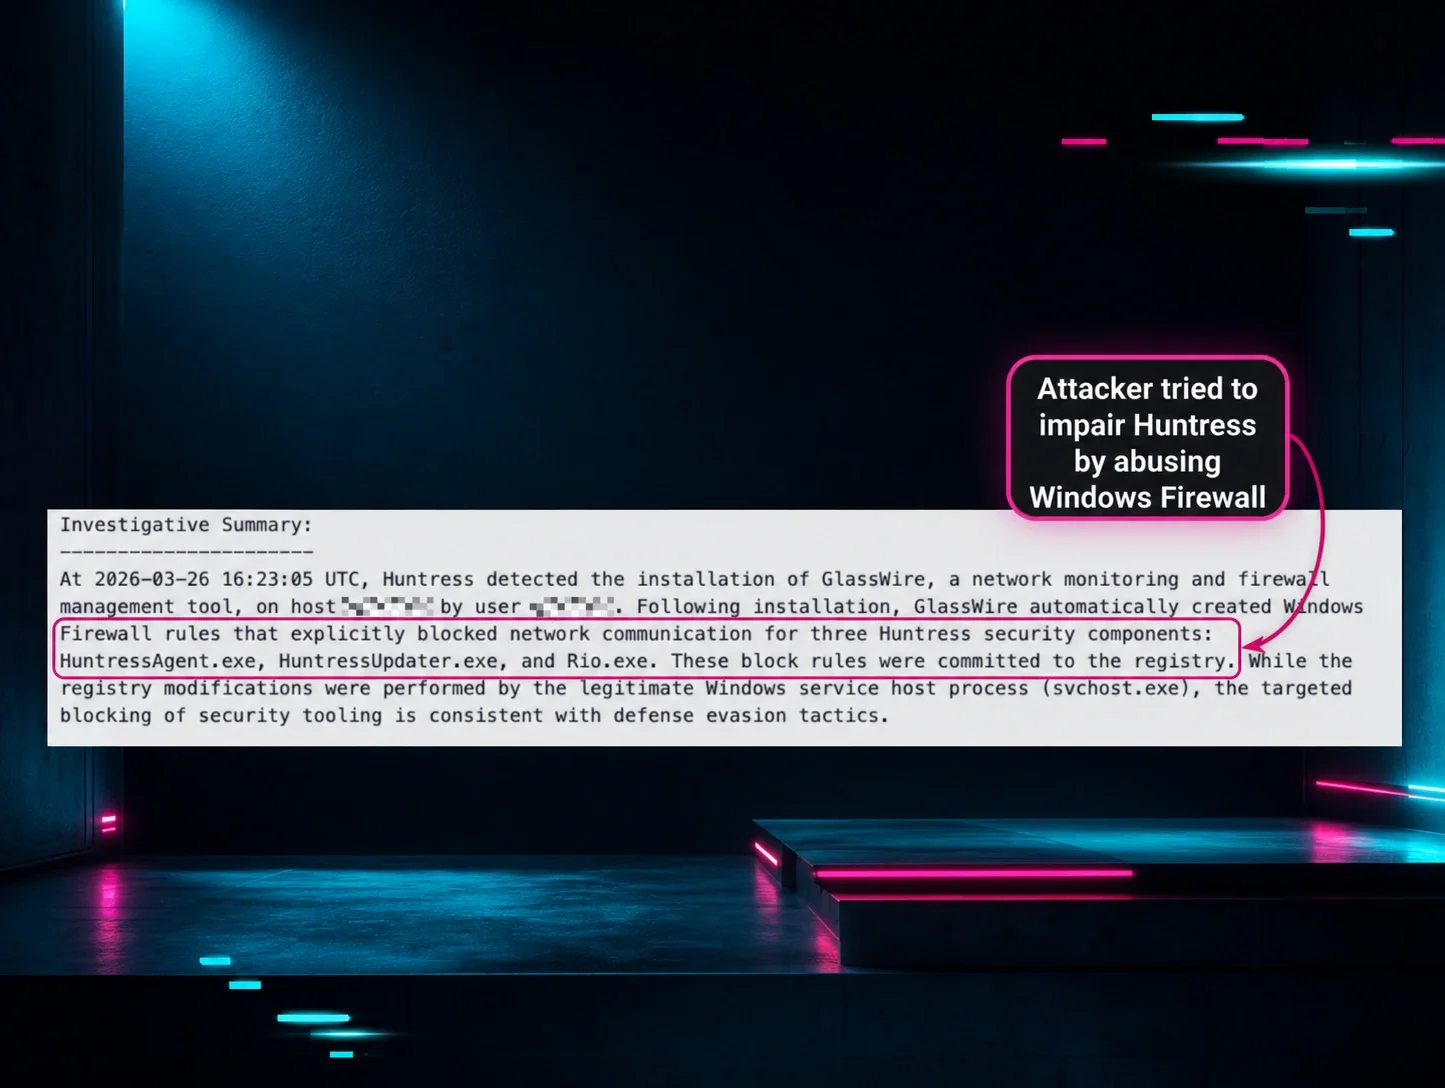
Threat Actors Target Security Tools: Disabling AV/EDR via Vulnerable Drivers, Tampering, and Malicious Firewall Rules
Recent intelligence shows attackers are actively disabling endpoint protection by exploiting vulnerable drivers, tampering with system components, and injecting malicious firewall rules. Defenders should audit driver integrity, enforce signed‑driver policies, monitor firewall changes, and apply the latest patches to mitigate these tactics.
Read briefing
Milk Dragon Phishing Kit Exploits Social‑Media Discount Ads
Milk Dragon, an AiTM phishing kit launched in October 2025, lures victims with fake discount offers on Facebook and TikTok marketplace ads. The campaign targets consumers shopping for consumer goods and can compromise credentials and personal data. Defenders should block suspicious links, verify ad URLs, and deploy XDR and MFA.
Read briefing