
Threat Intel
TONResolver RAT Targets Japanese Hospitality Sector via Booking.com Phishing
A targeted phishing campaign observed in May 2026 deployed the TONResolver RAT against hotels and accommodation providers in Japan. Threat actors utilized Booking.com-themed lures to deliver the malware, which uniquely abuses the TON blockchain for command-and-control operations.
What Happened
Security researchers identified a malicious phishing campaign launched in May 2026 specifically targeting the Japanese hospitality industry. The attackers weaponized accommodation-themed lures, specifically leveraging Booking.com communications, to trick personnel into opening malicious attachments or links. The campaign delivers a novel remote access trojan known as TONResolver RAT.
Attack Mechanics
Unlike traditional malware that relies on standard HTTP or HTTPS command-and-control (C2) infrastructure, the TONResolver RAT uniquely abuses the TON (The Open Network) blockchain for its operations. This blockchain-backed mechanism allows the threat actors to obfuscate traffic, evade standard perimeter detection controls, and maintain resilient communication channels with compromised systems.
Impacted Entities
Hotels, ryokans, and other accommodation facilities in Japan represent the primary target demographic for this campaign. Because these businesses frequently process sensitive customer reservation data and financial transactions through portal accounts, a successful compromise exposes both operational networks and guest privacy.
What Defenders Should Do
SecOps and sysadmins managing infrastructure in the hospitality sector should take immediate defensive actions:
- Monitor email gateways for spear-phishing messages mimicking Booking.com and reservation management platforms.
- Inspect endpoint telemetry for unauthorized processes interacting with blockchain networks or unusual outbound connection patterns.
- Conduct security awareness training focusing on reservation-themed social engineering tactics targeting front-desk and administrative staff.
- Verify that EDR and SIEM rules are updated to flag suspicious script execution and anomalous network traffic signatures associated with emerging RAT families.
Related articles
Bloody Wolf Spear‑Phishing Surge in Central Asia: Immediate Defender Actions
Bloody Wolf has ramped up spear‑phishing emails impersonating government agencies in Central Asia since late June 2025. Public‑sector employees are the primary targets. Defenders should verify sender authenticity, strengthen email protection, and enforce MFA.
Read briefing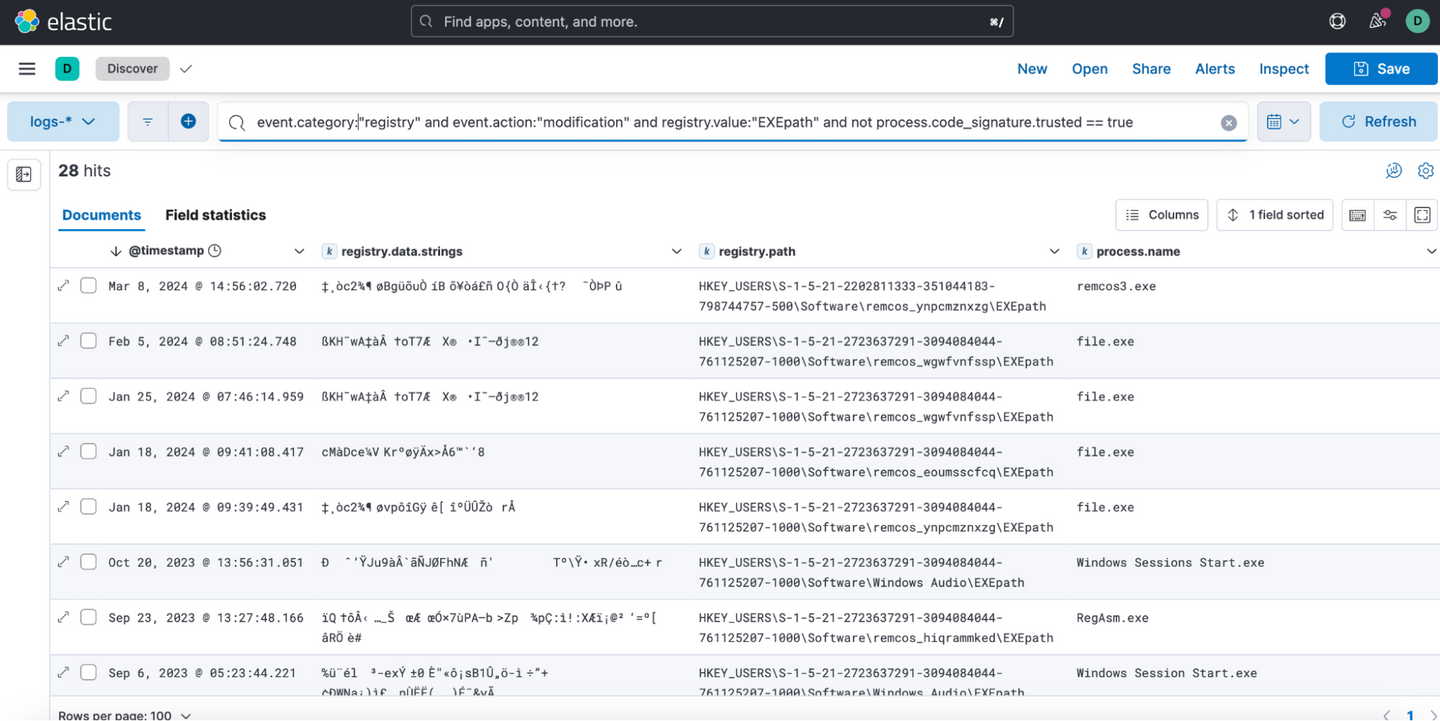
REMCOS RAT 2024: Persistence, UAC Bypass, and Browser Data Erasure – Detection Guidance
The REMCOS RAT, active in 2024, establishes persistence via the Run key, injects into svchost.exe and Internet Explorer, bypasses UAC with ICMLuaUtil, disables UAC, clears browser cookies, and logs keystrokes. Defenders should monitor registry modifications to EXEPath, unsigned process injections, and file deletions, and enforce UAC and signed‑binary policies.
Read briefing
BTMOB Android RAT: Phishing, Fake App Stores, and Accessibility Exploit
BTMOB is an Android RAT that spreads via phishing sites and counterfeit app stores, then abuses Accessibility Services to gain full device control. The malware is sold with an APK‑builder, enabling rapid, code‑free payloads. Defenders should block malicious domains, disable unknown accessibility services, and enforce app‑store vetting.
Read briefing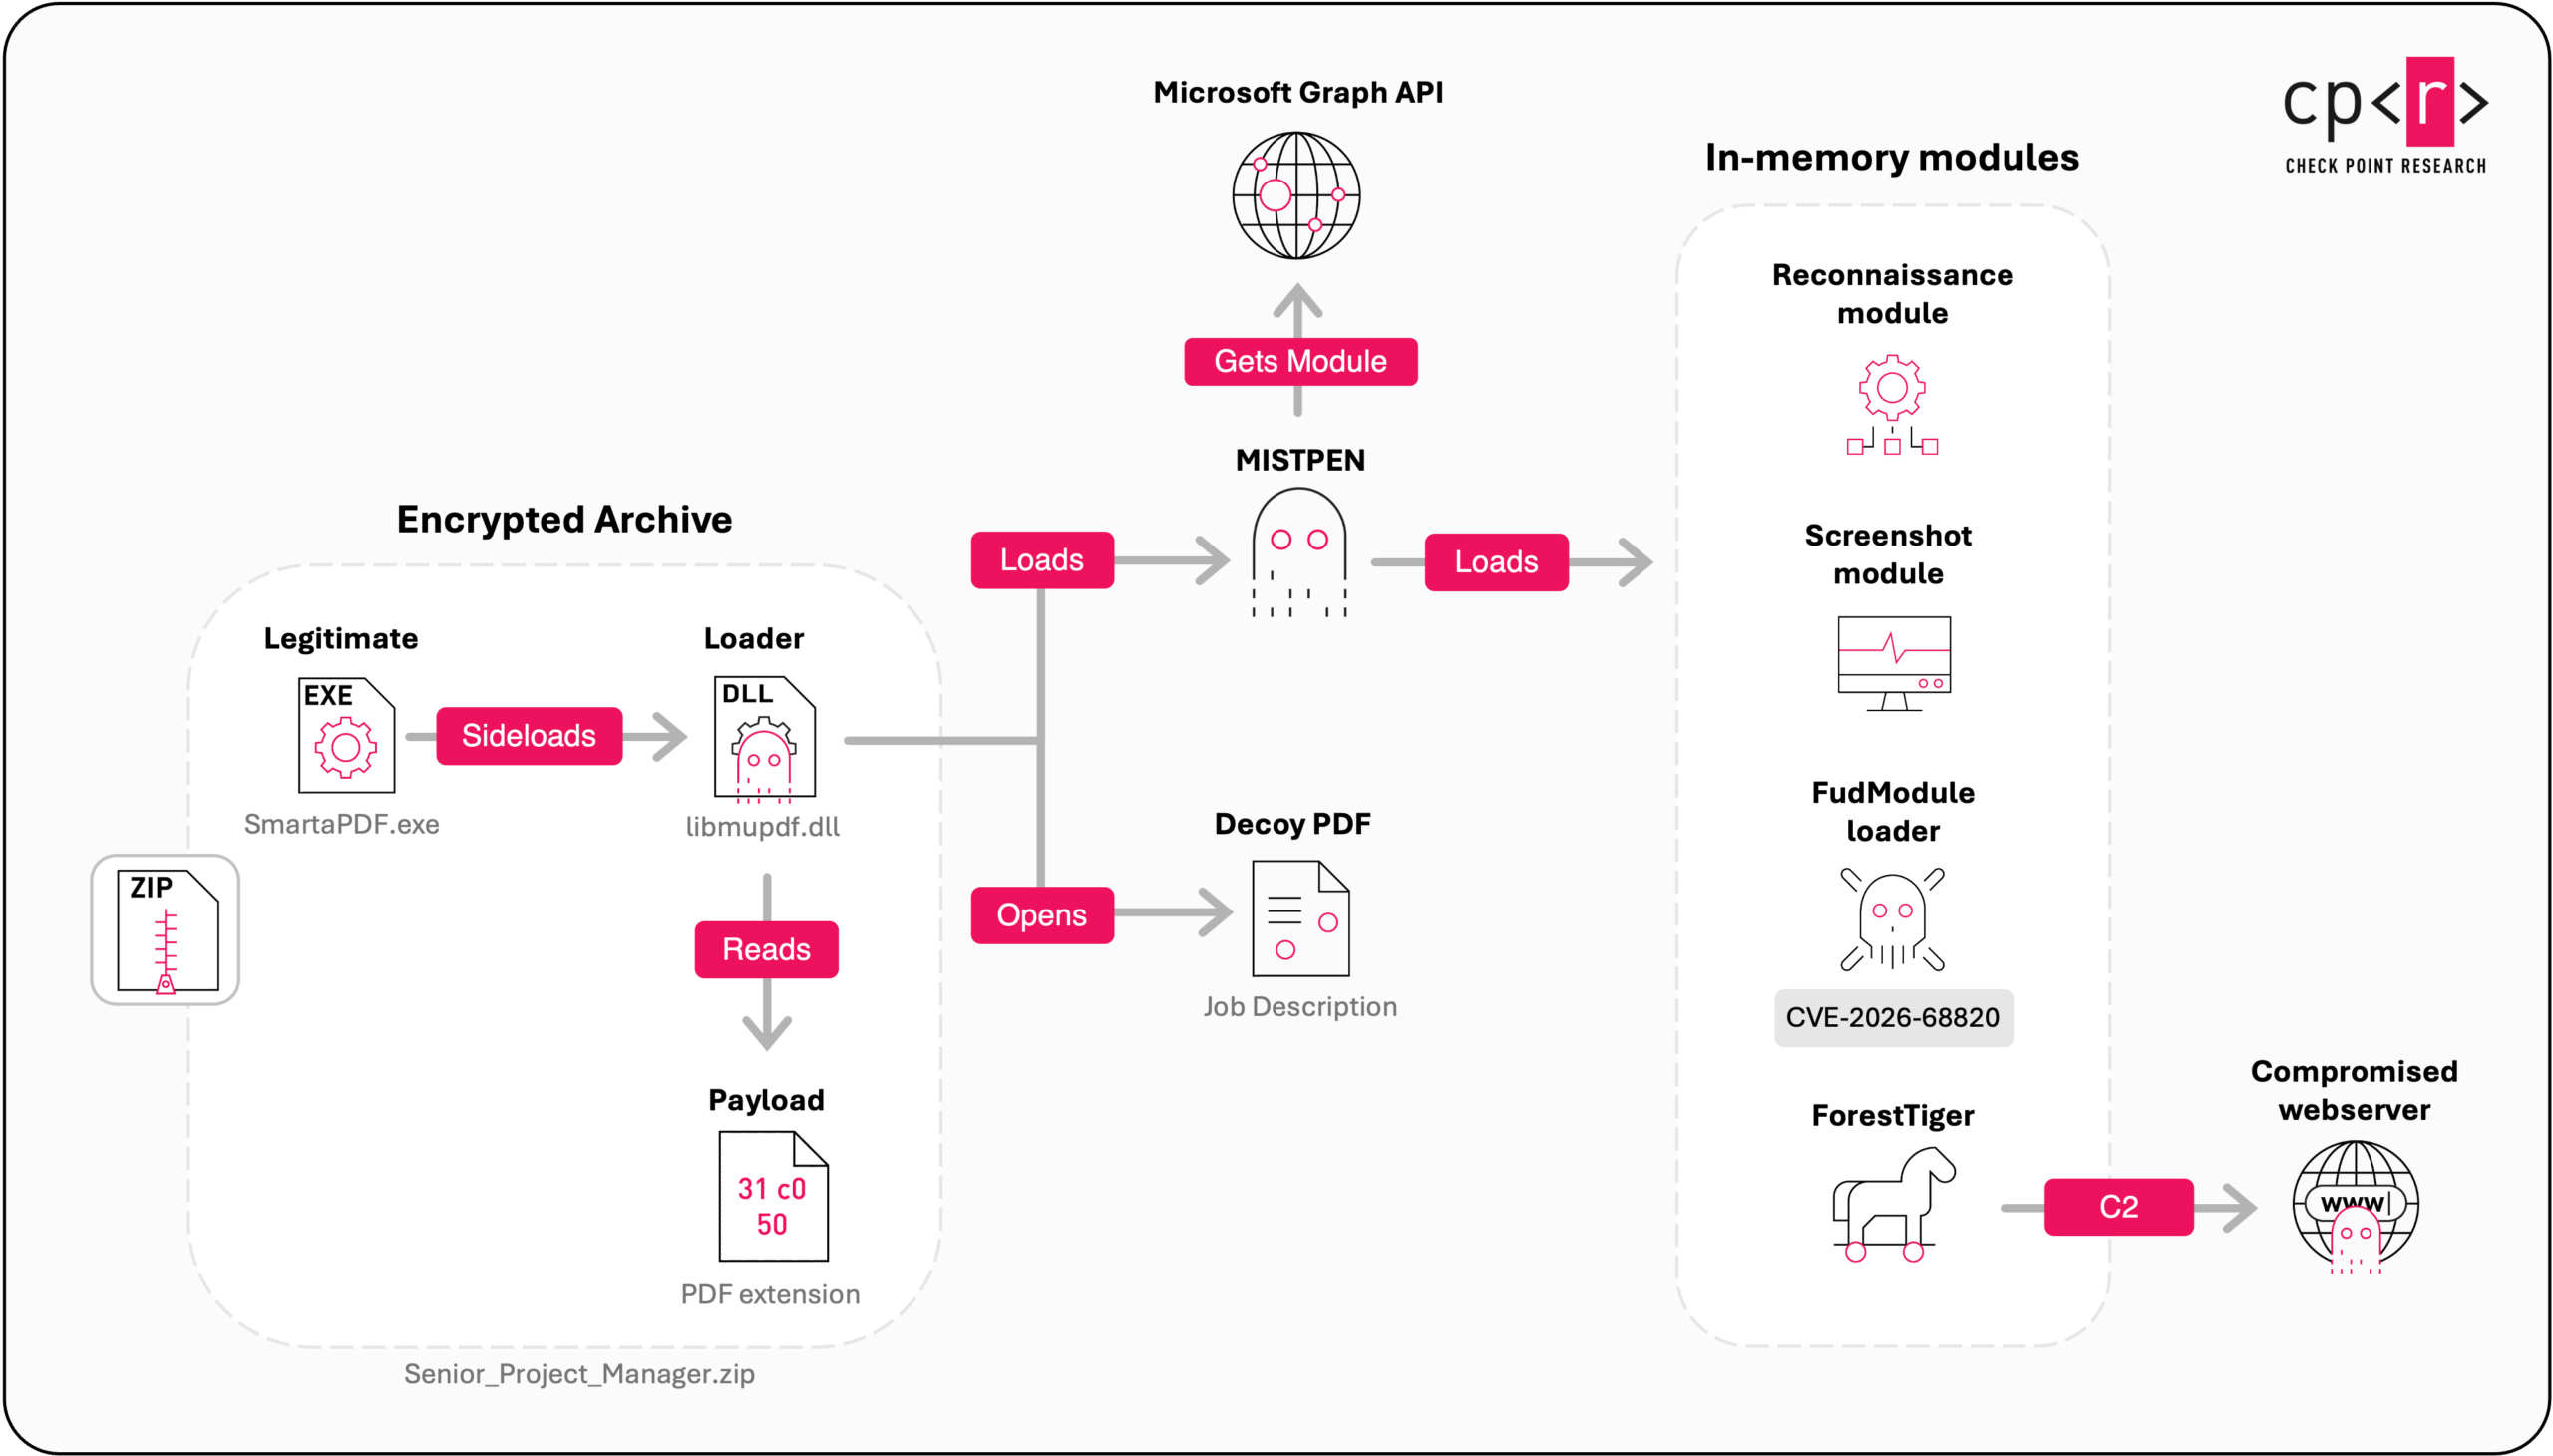
Operation Dream Job: From Job Offers to Zero‑Day Attacks on Defense Sectors
Check Point Research has traced a fresh wave of the Operation Dream Job campaign, a Lazarus‑linked effort that turns enticing job ads into a multi‑stage breach. The attackers now use a trojanized PDF viewer, the SecurityPDF app, to deliver a new kernel‑mode rootkit (FudModule) via the zero‑day CVE‑2026‑68820 in Microsoft’s AFD.sys driver. They also weaponize CVE‑2025‑49113 in Roundcube to plant RelayShell webshells, turning compromised servers into covert C2 relays. The campaign targets aerospace, aviation and defense firms worldwide, leveraging spear‑phishing, SEO‑boosted fake recruitment sit
Read briefing