
Vulnerabilities
AD RMS Certificate Export Allows Offline Decryption of All Protected Documents
A flaw in AD Rights Management Service lets a Service Group account export the Server Licensor Certificate private key, enabling attackers to decrypt every document the deployment has protected, even after the deployment is rebuilt. Defenders should audit Service Group permissions, rotate certificates, and monitor for unauthorized key exports.
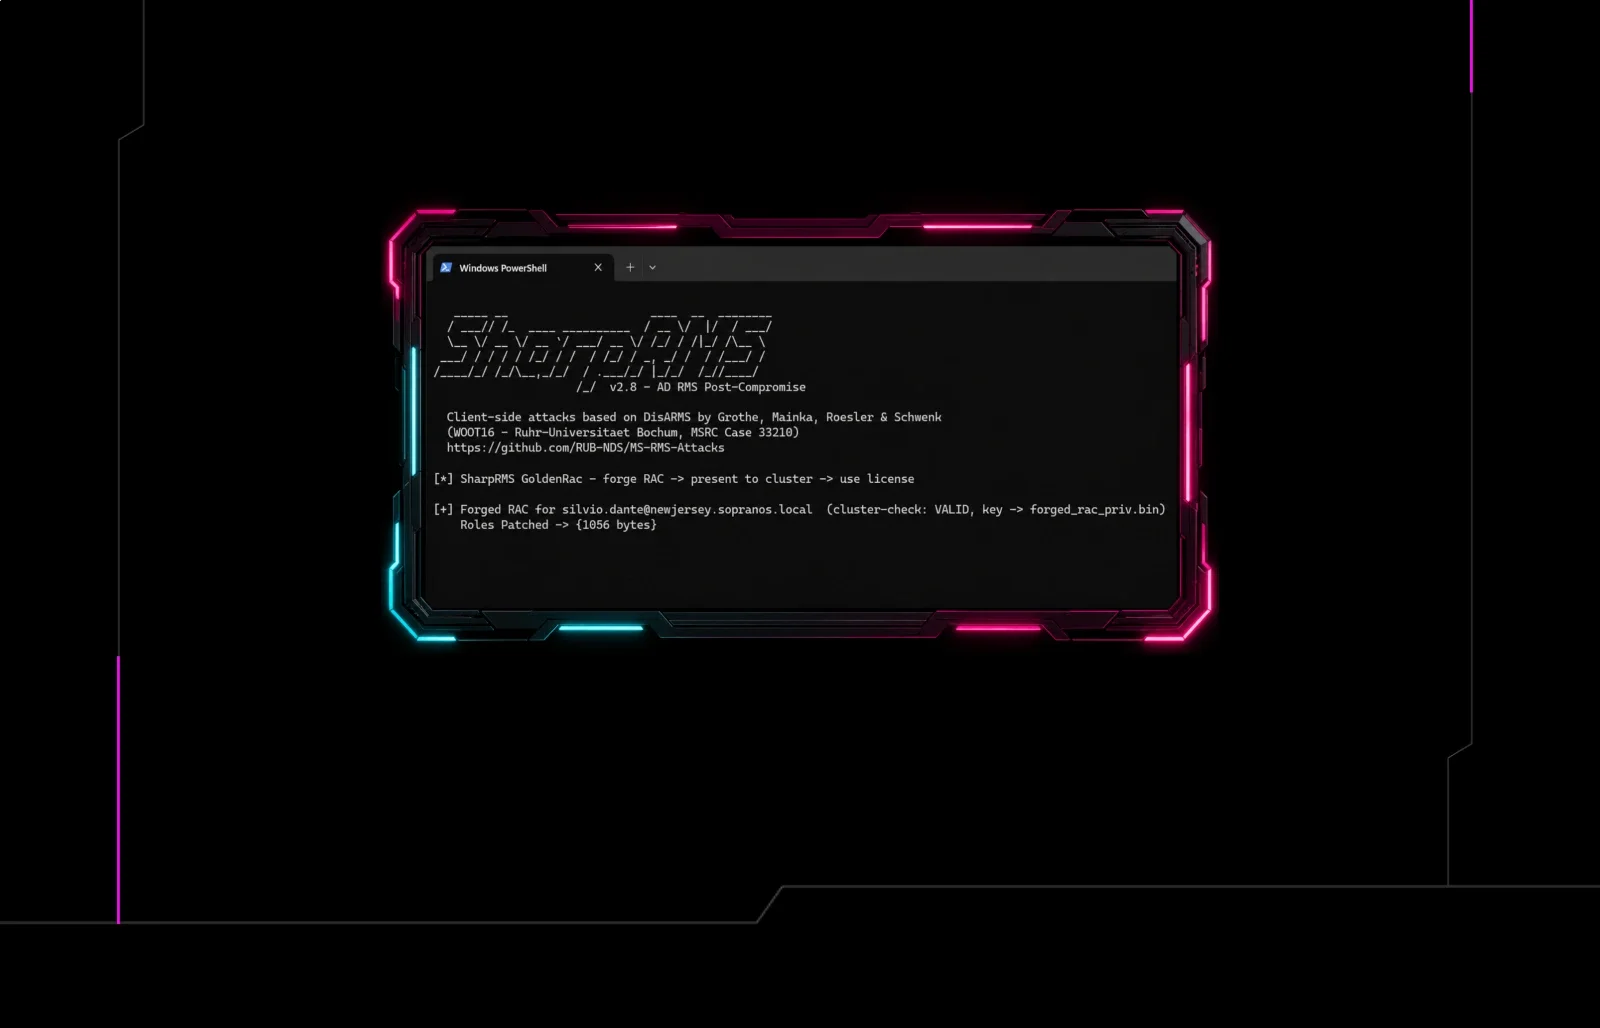
What Happened
An AD Rights Management Service (AD RMS) deployment can export the private key of the Server Licensor Certificate via the Service Group account. The 1,172‑byte key can decrypt all documents ever protected by that deployment.
Impact
Once the key is extracted, attackers can decrypt any stored or transmitted AD RMS‑protected file offline. The key remains valid after the AD RMS deployment is rebuilt, so the risk persists until the certificate is rotated.
Mitigation Steps
- Audit Service Group accounts and remove any that have export rights to the Server Licensor Certificate.
- Enforce least‑privilege on AD RMS Service Group accounts.
- Rotate the Server Licensor Certificate and update all protected documents.
- Disable the export capability if not required for business processes.
- Apply any vendor‑released patches that restrict key export.
Monitoring Recommendations
Enable audit logging for certificate export events and review logs for anomalous activity. Set alerts for any export of the Server Licensor Certificate and for changes to Service Group permissions.
Related vulnerabilities
StrongSwan Remote DoS Vulnerability (CVE‑2026‑78123) – Immediate Patching Required
A critical remote denial‑of‑service flaw has been discovered in StrongSwan VPN software, identified as CVE‑2026‑78123. The vulnerability allows attackers to crash the daemon on any system running a version older than 6.1.0, potentially taking networks offline. It is triggered by malformed IKE packets and can be mitigated by applying the vendor‑released patch. All affected deployments should update immediately.
Read briefing
CVE-2026-105598: Microsoft Office Access Heap Overflow Enables Remote Code Execution
A heap-based buffer overflow in Microsoft Office Access (CVE‑2026‑105598) allows attackers to run arbitrary code over a network. The flaw is exploitable without user interaction and can be triggered by crafted Access files. Defenders should apply the latest Office updates and restrict network exposure of Access documents.
Read briefing
FortiOS & FortiProxy Agentless ZTNA Portal Certificate Validation Flaw Enables MITM
Fortinet disclosed a CVSS 7.3 certificate validation flaw in FortiOS and FortiProxy Agentless ZTNA portal that allows unauthenticated attackers to perform MITM between the portal and backend sites. The vulnerability (CWE‑295) can be exploited remotely without credentials. Immediate patching and enforcement of strict TLS validation is required.
Read briefing
CVE-2026-69967: Windows Overlay Filter Out‑of‑Bounds Read Enables Local Information Disclosure
Microsoft identified an out‑of‑bounds read in the Windows Overlay Filter that allows a local user to read protected memory. The flaw exists in Windows 10 and 11 and is fixed by the latest cumulative update. Administrators should apply the patch and verify service configuration immediately.
Read briefing