
Vulnerabilities
BeyondTrust Remote Support Zero‑Day Exploited by Chinese State‑Backed Group
A zero‑day (CVE‑2026‑102764) in BeyondTrust Remote Support appliances was used by the Chinese state‑backed group Armory Castle to gain privileged access and move laterally in target networks. The vendor released a patch and issued mitigations; any internet‑exposed appliance should be treated as compromised until reviewed.
What Happened
On October 16, 2026, BeyondTrust confirmed that a previously unknown vulnerability in its Remote Support appliances was actively exploited by the Chinese state‑backed group Armory Castle (UNC5221). The flaw, identified as CVE‑2026‑102764, allowed attackers to elevate privileges, exfiltrate stored credentials, and modify persistent configuration files.
Impact
Attackers leveraged custom malware—Sawfly and Bareclaw—to maintain footholds and conduct long‑term intelligence collection. Targets included legal services, SaaS providers, business‑process outsourcers, technology firms, and government entities. Any appliance reachable from the internet is considered potentially compromised until a thorough review is completed.
Mitigations & Patch
BeyondTrust released a patch on October 16 that addresses the privilege‑escalation flaw. In the interim, administrators should:
- Isolate or shut down exposed appliances.
- Disable remote support services that are not required.
- Apply the vendor’s recommended configuration hardening steps.
- Monitor for anomalous credential usage and lateral movement.
Defender Actions
Security teams should verify that all Remote Support appliances are updated to the latest firmware. Conduct a rapid assessment of any device that was exposed to the internet during the exploitation window. If an appliance was found running the vulnerable version, treat it as compromised and perform a full forensic review.
Related vulnerabilities
BeyondTrust Remote Support Zero‑Day CVE‑2026‑102764 Exploited by Armory Castle
A China‑linked threat actor, Armory Castle, used a CVE‑2026‑102764 zero‑day in BeyondTrust Remote Support to compromise a self‑hosted appliance on August 29, 2026. The flaw allows remote file operations via improper origin validation. All SaaS customers are patched; self‑hosted users must apply BT26‑05‑RS or upgrade.
Read briefing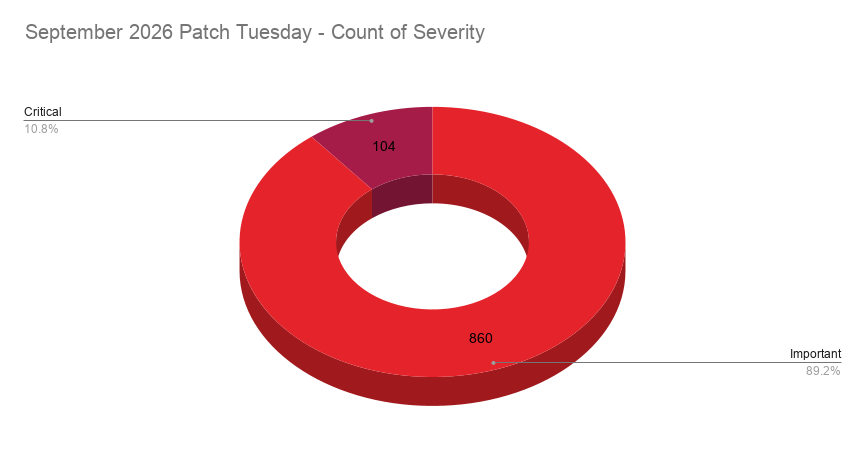
Microsoft September 2026 Patch Tuesday: 964 CVEs, Including Two Zero-Day Exploits (CVE-2026-81963, CVE-2026-85880)
Microsoft released its largest Patch Tuesday to date, addressing 964 CVEs—104 critical and 860 important—including two zero‑day vulnerabilities exploited in the wild. Defenders must prioritize applying updates to affected components such as .NET, Active Directory services, Azure services, Office, and Windows kernel drivers, and verify system integrity.
Read briefing
Cisco Secure Email Gateway CVE-2026-76461 Zero-Day Exploited in the Wild
Cisco has patched a critical SQL injection vulnerability, tracked as CVE-2026-76461, in the AsyncOS software used by Cisco Secure Email Gateway. The flaw allows unauthenticated, remote attackers to achieve root-level command execution via crafted emails and is actively exploited in the wild. SecOps and sysadmins must immediately apply the vendor-supplied firmware updates.
Read briefing
Ivanti Connect Secure Zero‑Day Exploited: Immediate Patch Required
An actively exploited authentication‑bypass zero‑day (CVE‑2026‑104935) has been found in Ivanti Connect Secure. The flaw affects versions 22.8R2.4 and earlier, 25.1.2.2 and earlier, and 25.1.1.1 and earlier, allowing unauthenticated remote attackers to run arbitrary commands. Defenders must patch immediately and run the Integrity Checker Tool.
Read briefing