
Vulnerabilities
Ivanti Connect Secure Zero‑Day Exploited: Immediate Patch Required
An actively exploited authentication‑bypass zero‑day (CVE‑2026‑104935) has been found in Ivanti Connect Secure. The flaw affects versions 22.8R2.4 and earlier, 25.1.2.2 and earlier, and 25.1.1.1 and earlier, allowing unauthenticated remote attackers to run arbitrary commands. Defenders must patch immediately and run the Integrity Checker Tool.
What happened
Ivanti has disclosed that an authentication‑bypass zero‑day (CVE‑2026‑104935) is actively being exploited against its Connect Secure remote‑access gateway.
Impact
The flaw is present in Connect Secure versions 22.8R2.4 and earlier, 25.1.2.2 and earlier, and 25.1.1.1 and earlier. Attackers who do not have any privileges can exploit the vulnerability with low complexity, without user interaction, to execute arbitrary commands on the appliance.
What to do
Defenders should:
- Verify if they are running any of the affected versions.
- Apply the vendor‑released patch or upgrade to the latest version immediately.
- Run the Integrity Checker Tool regularly to detect any unauthorized changes.
- Monitor logs for suspicious authentication attempts and command execution.
Ivanti stated it is aware of limited exploitation in the wild and is working with impacted organizations.
Related vulnerabilities
Ivanti Connect Secure Zero‑Day Exploited in the Wild (CVE‑2026‑104935)
A high‑severity authentication bypass in Ivanti Connect Secure allowed unauthenticated attackers to execute arbitrary commands. The flaw was already exploited before disclosure, prompting CISA to add it to the KEV catalog. Defenders must patch immediately and harden VPN access.
Read briefing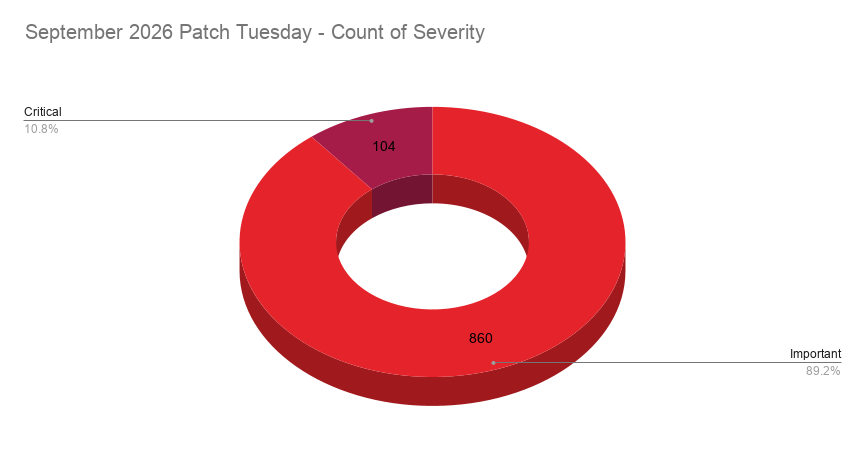
Microsoft September 2026 Patch Tuesday: 964 CVEs, Including Two Zero-Day Exploits (CVE-2026-81963, CVE-2026-85880)
Microsoft released its largest Patch Tuesday to date, addressing 964 CVEs—104 critical and 860 important—including two zero‑day vulnerabilities exploited in the wild. Defenders must prioritize applying updates to affected components such as .NET, Active Directory services, Azure services, Office, and Windows kernel drivers, and verify system integrity.
Read briefing
SAP Exposes Critical Kernel & Message Server Flaws: CVE-2026-44756 & CVE-2026-58240
SAP’s September Security Patch Day revealed two critical vulnerabilities that can be exploited remotely without authentication. The memory‑corruption flaw in SAP Extended Passport (OVERPASS, CVE‑2026‑44756) and the missing‑auth bug in NetWeaver Message Server (S4GET, CVE‑2026‑58240) both allow attackers to run arbitrary OS commands as the SAP installation user, risking full system takeover. Immediate application of SAP Security Notes 3747649 and 3759472 is mandatory.
Read briefing
CVE-2026-12345: CPython Data Integrity Vulnerability – Immediate Patch Required
A critical data‑integrity flaw (CVE‑2026‑12345) was disclosed in CPython, allowing attackers to corrupt program state. Systems running unpatched CPython versions are at risk. Apply the PSF‑2026‑42 patch and verify the update immediately.
Read briefing