
Vulnerabilities
Cisco Secure Email Gateway CVE-2026-76461 Zero-Day Exploited in the Wild
Cisco has patched a critical SQL injection vulnerability, tracked as CVE-2026-76461, in the AsyncOS software used by Cisco Secure Email Gateway. The flaw allows unauthenticated, remote attackers to achieve root-level command execution via crafted emails and is actively exploited in the wild. SecOps and sysadmins must immediately apply the vendor-supplied firmware updates.
What Happened
Cisco disclosed a critical zero-day vulnerability, designated CVE-2026-76461, affecting Cisco AsyncOS Software deployed on Cisco Secure Email Gateway appliances. Carrying a maximum CVSS v3.1 base score of 9.8, the flaw stems from a SQL injection vulnerability within the email processing pipeline. Because these gateways routinely ingest external inbound and outbound messages, exploitation requires no prior authentication or administrative access. An attacker can trigger arbitrary command execution with root privileges simply by routing a crafted email through a vulnerable appliance.
Impact
The vulnerability grants unauthenticated attackers complete system compromise at the root level. Because Cisco Secure Email Gateway sits at the network perimeter to filter spam, phishing, and malware, successful exploitation compromises a critical boundary defense component. CISA has added the flaw to its Known Exploited Vulnerabilities (KEV) catalog, confirming active in-the-wild exploitation prior to disclosure. While no public proof-of-concept exploit code or definitive threat actor attribution has been released, active zero-day abuse demands immediate defensive action.
What to Do
Defenders and system administrators should bypass standard maintenance windows and immediately update affected Cisco Secure Email Gateway deployments to the appropriate fixed version:
- Version 15.5 and earlier: Upgrade to 15.5.5-014
- Version 16.0: Upgrade to 16.0.4-302
- Version 16.5: Upgrade to 16.5.0-780
Review gateway logs for anomalous message traffic and unexpected process execution originating from the AsyncOS email ingestion pipeline.
Related vulnerabilities
Cisco Secure Email Gateway Vulnerability Enables Remote Root Execution
A critical flaw (CVE-2026-76461) in Cisco AsyncOS Email Gateway allows unauthenticated remote attackers to execute commands as root. The issue stems from insufficient email parsing validation and is actively exploited. Defenders should patch immediately and monitor for anomalous activity.
Read briefing
Critical SQL Injection in Cisco Secure Email Gateway Grants Root Access
A new flaw in Cisco’s AsyncOS email parsing logic lets unauthenticated attackers send a crafted message that injects SQL, triggering arbitrary commands with root privileges on the host. The vulnerability, CVE‑2026‑76461, is critical and has no workaround—only a patch. Cisco has released updates; systems must upgrade immediately to avoid a full compromise.
Read briefing
Cisco Secure Email Gateway & AsyncOS: Multi‑Vulnerability Alert – RCE, DoS, SQLi
A wave of security flaws has been uncovered across Cisco’s Secure Email Gateway, Secure Email and Web Manager, and AsyncOS platforms. Several of the bugs enable attackers to execute arbitrary code remotely, crash the system, and inject malicious SQL statements. Cisco’s CVE‑2026‑76461 is already being actively exploited. Immediate patching is mandatory for all affected versions, and network operators should verify that hardening guidelines are in place.
Read briefing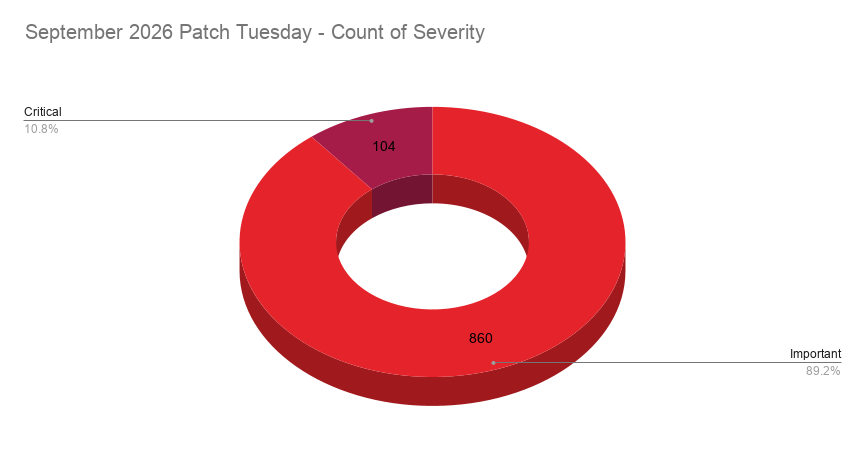
Microsoft September 2026 Patch Tuesday: 964 CVEs, Including Two Zero-Day Exploits (CVE-2026-81963, CVE-2026-85880)
Microsoft released its largest Patch Tuesday to date, addressing 964 CVEs—104 critical and 860 important—including two zero‑day vulnerabilities exploited in the wild. Defenders must prioritize applying updates to affected components such as .NET, Active Directory services, Azure services, Office, and Windows kernel drivers, and verify system integrity.
Read briefing