
Advisories
Adobe June 2026 Patch Tuesday: 11 Bulletins, 123 CVEs, CVSS 10.0 in Campaign Classic
Adobe released 11 security bulletins in June 2026, addressing 123 CVEs across multiple products. The highest severity CVSS 10.0 is in Campaign Classic, with other critical CVEs in ColdFusion and Acrobat Reader. Defenders should prioritize patching Campaign Classic first, then ColdFusion and Acrobat Reader, and monitor for exploitation.
What Happened
Adobe released 11 security bulletins in June 2026, covering 123 unique CVEs across Acrobat Reader, ColdFusion, Experience Manager, InDesign, InCopy, Substance 3D Sampler, Content Credentials SDK, Dreamweaver, Format Plugins, and Campaign Classic.
Impact
Highest severity is CVSS 10.0 in Campaign Classic (APSB26‑66). Other critical CVEs (CVSS 7.8‑9.6) affect ColdFusion, Acrobat Reader, and several design tools. No active exploitation has been reported, but the high CVSS scores indicate potential for serious impact if left unpatched.
Deployment Priorities
1. Campaign Classic – CVSS 10.0, critical priority.
2. ColdFusion – CVSS 9.6, critical priority.
3. Acrobat Reader – CVSS 7.8, critical priority.
4. Remaining Adobe products – critical or important severity, apply as soon as possible.
What to Do
Apply the latest patches immediately. Verify deployment with Adobe’s update catalog and confirm that affected versions are no longer present. Monitor logs for anomalous activity related to the CVEs, and consider temporary mitigations such as disabling vulnerable features or restricting network access to unpatched systems.
Related vulnerabilities
Microsoft Unleashes 972 CVE Fixes on Patch Tuesday, Including 2 Exploited Zero‑Days and 113 Critical Flaws
Microsoft’s September 2026 Patch Tuesday update tackles 972 CVEs—two of which are actively exploited zero‑days and 113 critical vulnerabilities. The patch covers Windows, Office, and other Microsoft components, tightening defenses across the ecosystem. Security teams should apply the fixes immediately and monitor for any lingering exploitation attempts.
Read briefing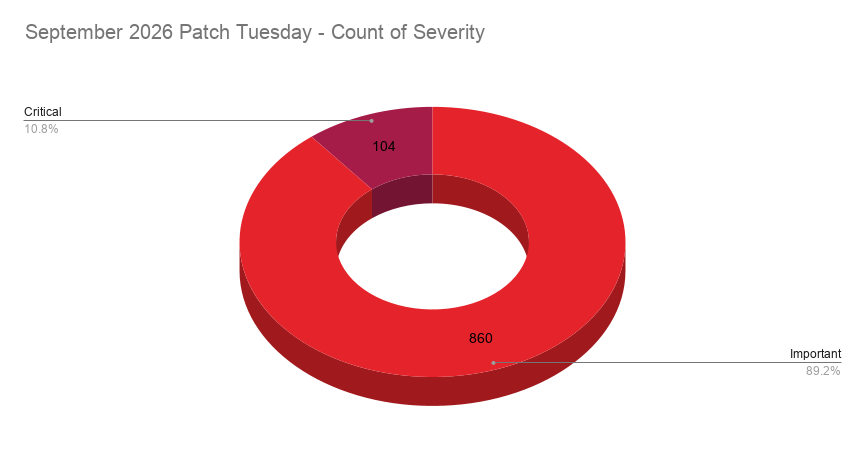
Microsoft September 2026 Patch Tuesday: 964 CVEs, Including Two Zero-Day Exploits (CVE-2026-81963, CVE-2026-85880)
Microsoft released its largest Patch Tuesday to date, addressing 964 CVEs—104 critical and 860 important—including two zero‑day vulnerabilities exploited in the wild. Defenders must prioritize applying updates to affected components such as .NET, Active Directory services, Azure services, Office, and Windows kernel drivers, and verify system integrity.
Read briefing
CVE‑2026‑108455: PowerPoint Information Disclosure – Update Omission Clarified
Microsoft Office PowerPoint’s information disclosure vulnerability (CVE‑2026‑108455) was fixed in the October 2026 security update, but the CVE was omitted from the advisory list. Defenders should verify the update is installed; no further action is required if already updated.
Read briefing
Critical Cisco Hardening Release: ASA, FTD, FMC Patch Internal Exploits
Cisco’s security team has rolled out a hardening update for its Secure Firewall Adaptive Security Appliance, Threat Defense, and Management Center software, addressing a suite of internally discovered flaws. Eight CVEs (CVE‑2026‑20329 through CVE‑2026‑20336) cover issues ranging from static credential exposure to authentication bypass, with two vulnerabilities already being actively exploited. No workarounds exist; customers must install the patches promptly to mitigate the critical risk.
Read briefing