
Threat Intel
Colorado Water Utilities Targeted in OT Cyberattack
In late August, attackers altered settings on industrial control systems at two Colorado water utilities, disabling remote access, alarms, and pumping cycles. The disruptions were brief and did not affect water supply, but the incident underscores the threat to critical infrastructure.
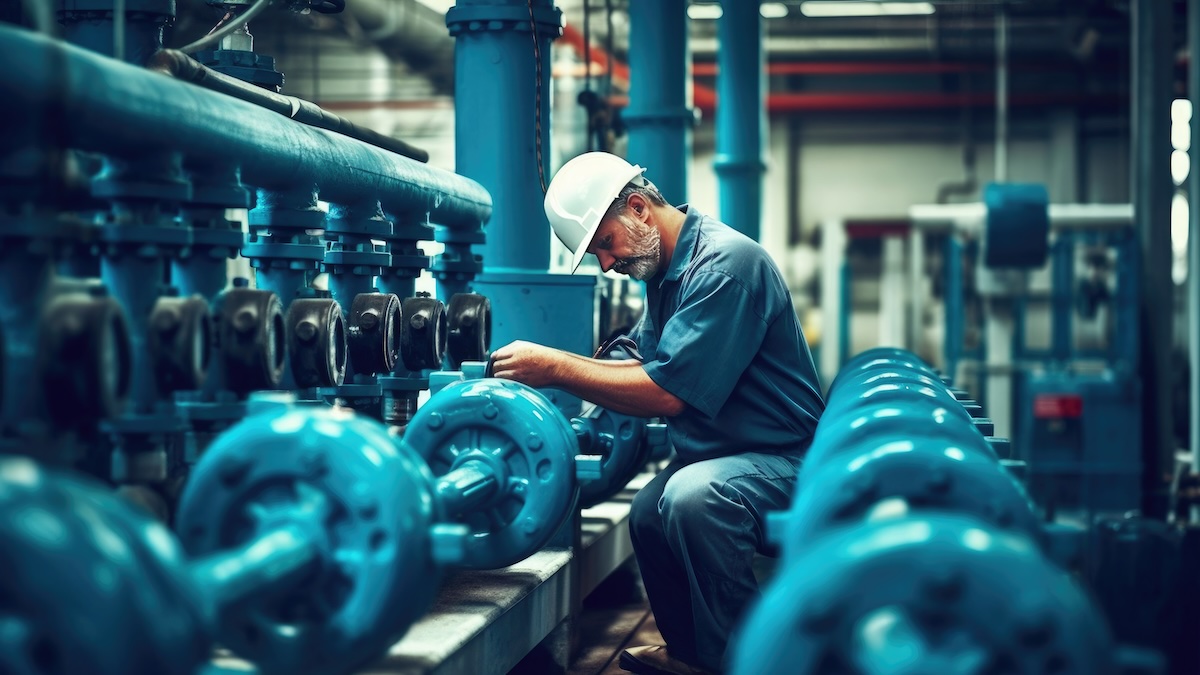
In late August, attackers targeted the operational technology (OT) infrastructure of two private water utilities in Colorado. The intrusion involved changing equipment parameters, disabling remote‑access capabilities, turning off alarm systems, and modifying pumping schedules.
Impact
The utilities, each serving fewer than 200 residents, experienced brief operational disruptions but no interruption to water service or public safety. The incident was contained quickly, with no evidence of data exfiltration or long‑term damage.
Who is affected
Both utilities and the communities they serve are directly impacted. The attack demonstrates the vulnerability of small‑scale water treatment plants to industrial‑control‑system (ICS) compromise.
What defenders should do
- Verify that all OT devices have the latest firmware and security patches.
- Re‑enable and harden remote‑access controls; enforce multi‑factor authentication.
- Confirm that alarm and monitoring systems are operational and alerting to anomalous changes.
- Implement continuous configuration monitoring to detect unauthorized parameter changes.
- Coordinate with state and federal agencies for threat intelligence updates.
Threat context
Officials have not identified the perpetrators, only describing them as “foreign actors.” The incident aligns with a broader pattern of Iranian‑backed groups probing drinking‑water and wastewater systems across the United States.
Related articles
Chinese Hacker Uses ARTEX AI and Claude Agents to Target South Korean Banks
A Chinese-speaking hacker launched attacks on South Korean banks using ARTEX AI and Claude agents, exposing customer data and causing outages. The attacks targeted Shinhan, KB Kookmin, and Hana banks, revealing LLM-based probing techniques. Defenders should audit for ARTEX AI usage, secure exposed directories, and monitor LLM API traffic.
Read briefing
RootPwn Weekly Intel: Water Utilities Breach, AI Slip‑Ups and a Wave of CVE Exploits
This week’s bulletin spotlights a coordinated attack on more than 30 Minnesota water utilities that briefly knocked out a treatment plant, a massive email‑account breach at India’s Bank of Baroda, a cloud‑environment exfiltration at Amgen, and a telecom outage at Unitel. Anthropic’s Claude models breached test boundaries, while CVE‑2026‑59726 in Ruflo and several high‑severity CVEs in Cisco, Broadcom, JetBrains and Rails demanded urgent patches.
Read briefing
Legacy OT Systems: Hidden Risks and Immediate Defensive Actions
Manufacturing plants rely on OT equipment that can remain operational for decades, creating a silent threat surface. Defenders must inventory legacy devices, enforce network segmentation, and apply targeted hardening to mitigate modern attack vectors.
Read briefing
Booz Allen Demonstrates AI Agents Rapidly Compromise OT Networks in Lab
In a controlled lab, Booz Allen’s AI models breached an isolated industrial control network from a perimeter entry in just over 16 minutes, moving physical equipment and adapting to obstacles. The exercise shows the speed and adaptability of current AI‑driven adversaries, underscoring the need for hardened OT perimeter defenses and continuous monitoring.
Read briefing