
Threat Intel
Corp MDM Android Spyware Targets Logistics Sector via Fake Google Play Pages
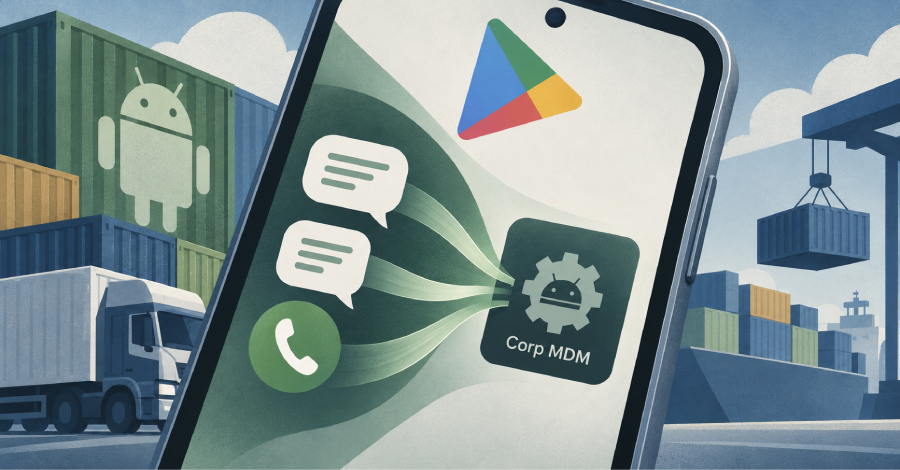
A targeted campaign is distributing Android spyware known as Corp MDM via fraudulent Google Play landing pages impersonating logistics brands. The malware, packaged as a system service, is designed to intercept inbound SMS traffic, manipulate call routing, and maintain persistent background execution using a hard-coded command-and-control infrastructure.
What Happened
Threat actors have launched a malicious operation aimed specifically at the logistics sector, utilizing counterfeit Google Play Store domains tied to brands such as CEVA and TKW Logistics. These fraudulent sites distribute a malicious Android Package Kit (APK) utilizing the package identifier com.corp.mdm and masquerading as a legitimate system service.
Security researchers note that the implant relies on a hard-coded command-and-control (C2) IP address (69.55.61.82), which also hosts credential-phishing pages and secondary Windows malware payloads.
Technical Impact & Capabilities
Once installed via sideloading, the Corp MDM application requests sensitive permissions related to SMS, telephony, and notifications. Its core functionality includes:
- Intercepting and exfiltrating newly received SMS messages.
- Configuring unauthorized call forwarding.
- Hiding its application launcher icon while executing a persistent foreground service.
- Communicating with the C2 infrastructure every 30 seconds via dedicated endpoints for device registration, telemetry heartbeats, and polling for operator commands.
Analysis suggests the implant was engineered with the assistance of artificial intelligence, evidenced by distinct code anomalies that occasionally impede its execution flow.
What Defenders Should Do
SecOps and mobile device management (MDM) administrators should implement immediate defensive controls:
- Block network traffic to the known C2 indicator:
69.55.61.82. - Enforce strict policies against sideloading and installation of applications from unknown sources across all corporate and BYOD Android fleets.
- Audit mobile endpoints for the presence of package name
com.corp.mdmor unauthorized applications lacking standard launcher icons. - Monitor inbound SMS and telephony permission usage for anomalies, particularly on devices assigned to logistics and supply chain personnel.
Related articles
Hirudo Android Malware Hijacks Banking Apps to Steal Credentials
Hirudo is an Android malware that replaces legitimate banking apps with malicious copies, disabling security checks to harvest credentials and remotely control devices. It targets banks in Indonesia, China, India, Mexico, Morocco, and Thailand, and is delivered via apps that masquerade as shopping or entertainment services. Defenders should verify app signatures, enforce Play Integrity, restrict Accessibility permissions, and deploy mobile security solutions to detect hooking engines.
Read briefing
Pegasus Zero‑Click Spyware: Detection and Mitigation for iOS and Android
Pegasus has been infecting mobile devices via zero‑click exploits, silently collecting messages, calls, location and audio. The threat remains active on both iOS and Android. Defenders should verify device integrity, monitor for abnormal data exfiltration, and apply vendor‑specific hardening steps.
Read briefing
Chrome 155.0.8059.79/80 Update Addresses 37 Vulnerabilities, 7 Critical
Google released Chrome 155.0.8059.79/80 on Oct 13‑14, patching 37 security flaws including seven rated Critical. The update fixes code‑execution vulnerabilities that could be triggered by malicious web pages. Defenders should apply the update immediately on Windows, macOS, Linux, and Android devices.
Read briefing
RemControl Android Banking Malware Targets European and Canadian Users via Fake IPTV Ads
RemControl, a new Android malware‑as‑a‑service platform, has been delivering banking trojans through fake TVTap IPTV ad sites. The campaign, active since May, targets users in Italy, France, Spain, Poland, Portugal, Canada and the Middle East. Defenders should block known malicious domains, enforce app‑store vetting, and monitor for phishing overlays on Android devices.
Read briefing