
Advisories
Elastic Launches AlertZero: AI‑Driven SOC Automation to Achieve Inbox Zero for Alerts
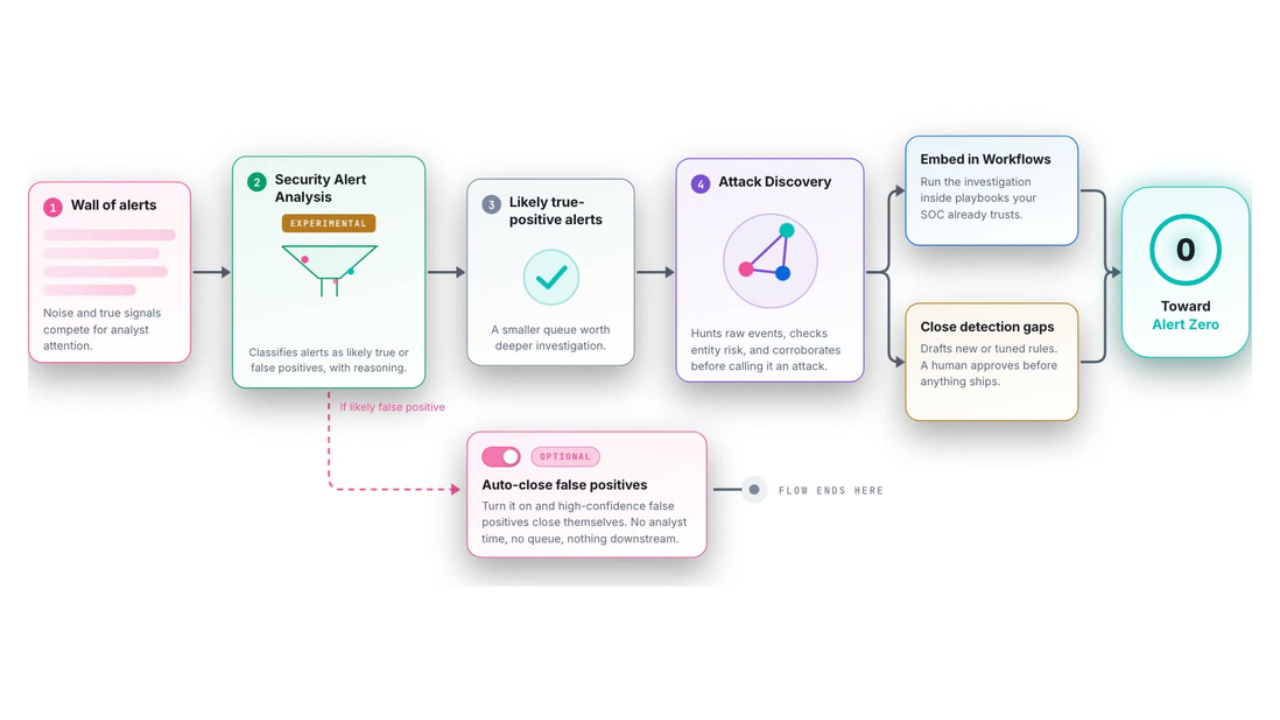
Elastic Security introduces AlertZero, an AI‑powered layer that automates alert triage, hunting, detection, and forensics through four dedicated agents. The system reduces queue volume, filters false positives, and proposes analyst‑approved actions, enabling teams to maintain full coverage without manual overload.
What Happened
Elastic Security rolled out AlertZero, a new AI‑driven layer that automates the entire alert lifecycle. The feature introduces four agents—Triage, Hunt, Detection, and Forensics—each running as a Watch that triggers on alerts or schedules.
Impact on SOC Operations
Teams that previously struggled with alert fatigue and limited analyst capacity can now reduce queue size, filter false positives, and receive evidence‑backed action proposals. The system keeps all actions under analyst approval, preserving control while accelerating response.
“The Hugging Face incident highlighted the need for correlation; AlertZero addresses that by connecting alerts into attack narratives.”
Key Features
- Four dedicated Watches with distinct responsibilities
- Proposed Actions requiring analyst approval
- Manual, assisted, or supervised autonomy levels
- Support for proprietary and open‑source models
- Runs on Elastic Cloud, self‑managed, or air‑gapped environments
How to Deploy
Add AlertZero to your Elastic Security deployment via the UI or API. Configure model preferences, set autonomy levels, and enable the Watches. Monitor the new alert queue view to see reduced volume and actionable proposals.
Related articles
Proofpoint Launches SOC Analyst Agent Powered by OpenAI Daybreak Models
Proofpoint has released a new SOC Analyst Agent that leverages OpenAI’s Daybreak models to streamline threat investigation, signal correlation, and repetitive analysis. The tool is aimed at SecOps teams seeking faster, AI‑driven insights. Defenders should assess integration with existing workflows and monitor model outputs for accuracy and bias.
Read briefing
Microsoft Patch Tuesday 2026: 972 CVEs, 113 Critical, Two Exploited Zero‑Days
Microsoft’s September 2026 Patch Tuesday saw 972 vulnerabilities patched, including 113 rated critical and two zero‑days that were already in the wild. CrowdStrike’s latest security releases emphasize supply‑chain protection and AI‑driven SOC evolution, underscoring the need for rapid patching and advanced detection.
Read briefing
Elastic Acquires Keep Alerting to Enhance AIOps and Workflow Automation
Elastic has acquired Keep Alerting, an open‑source AIOps platform that consolidates alerts, reduces noise, and automates incident remediation. The integration will bring Keep’s alert deduplication, correlation, and workflow engine into Elasticsearch and Kibana, benefiting SREs, engineers, and security teams. Defenders should review their alert pipelines, adopt Keep’s automation features, and monitor for new updates.
Read briefing
Elastic InfoSec Slashes SOC Costs 5× with Specialized Agent Workflow
Elastic InfoSec ran a head‑to‑head test of two agentic SOC models across 36,822 real alerts. A single, multi‑skill agent cost $3.42 per investigation, while a fleet of domain‑specific agents trimmed the bill to just $0.69—a 5.7× savings. At 100 alerts a day that translates to an $8,000 monthly cut. The post explains the two architectures, why the specialized workflow wins, and when each model is the right fit for your security ops budget.
Read briefing