
Malware
FakeSecurity JS‑Sniffer Campaign Targets Web Applications – Immediate Mitigation Steps
Group‑IB uncovered a new JavaScript sniffer, FakeSecurity, that injects malicious scripts into web pages to harvest credentials and session data. The campaign has affected multiple enterprise web applications, exploiting cross‑site scripting and insecure content delivery. Defenders should block known malicious domains, update WAF rules, and monitor for suspicious JavaScript payloads.
Group‑IB specialists identified a new JavaScript sniffer family dubbed FakeSecurity that injects malicious code into legitimate web pages. The malware harvests credentials, session cookies, and other sensitive data by exploiting XSS and insecure content delivery networks.
What happened
FakeSecurity was discovered during a routine threat‑intel feed review. The sniffer operates by loading a hidden script tag from a command‑and‑control domain that serves a payload designed to capture user input and transmit it back to the attacker.
Impact
- Multiple enterprise web applications reported credential theft and session hijacking.
- Affected systems include popular CMS platforms and custom web portals.
- Severity is high due to the ease of deployment and the potential for credential reuse.
Detection
Defenders should look for:
- Unexpected
scripttags referencing unknown domains. - Outbound HTTP requests to domains with a high reputation score for malicious activity.
- Unusual traffic patterns from web servers to external IPs during business hours.
Mitigation
- Update web application firewalls to block known FakeSecurity domains.
- Enforce strict content‑security policies that disallow inline scripts and external script loading from untrusted sources.
- Patch vulnerable CMS components and third‑party plugins that may be exploited for XSS.
- Deploy network segmentation to isolate critical web services from the rest of the infrastructure.
Next steps
Maintain continuous monitoring of web traffic and keep threat‑intel feeds current to detect emerging variants of the FakeSecurity sniffer.
Related articles
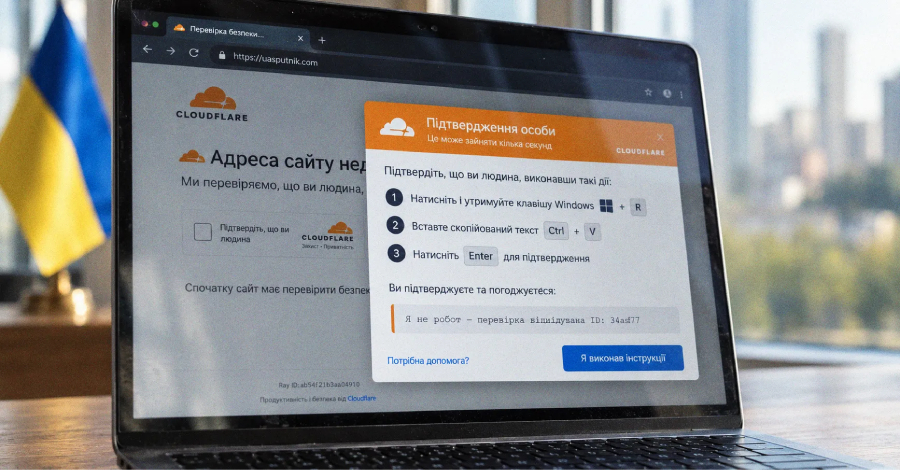
ClickFix Campaign Compromises Ukrainian Sites, Deploys Psychedelic Stealer via Fake Cloudflare Verification
An active ClickFix campaign has injected fake Cloudflare verification pages into legitimate Ukrainian business sites, tricking visitors into running an MSI installer that delivers the Psychedelic stealer. The malware harvests credentials, cryptocurrency wallet data, and establishes persistence via scheduled tasks. Defenders should block the attacker domains, detect MSI executions, and harden web applications against iframe injection.
Read briefing
ATMZOW JS‑Sniffer Linked to Hancitor‑Based Phishing Campaign Targeting US Bank Clients
Group‑IB analysts uncovered that the ATMZOW JavaScript sniffer is connected to a Hancitor malware chain used in a phishing operation aimed at customers of a U.S. bank. The campaign leverages compromised web pages to harvest credentials and deliver the Hancitor payload. Defenders should inspect inbound traffic for suspicious JS snippets, block known Hancitor domains, and enforce multi‑factor authentication for banking clients.
Read briefing
PhantomRaven: JavaScript Info Stealer Developed by Bug‑Bounty Threat Actor
CrowdStrike uncovered PhantomRaven, a JavaScript‑based information stealer created by a financially motivated threat actor who operates as a bug‑bounty hunter. The malware targets web applications, harvesting credentials and sensitive data via injected scripts. Defenders should inspect client‑side code, enforce strict CSP, and monitor for anomalous JavaScript activity.
Read briefing
UltraRank JavaScript Sniffer Infects 12 eCommerce Sites – Immediate Mitigation Steps
UltraRank’s latest campaign deployed a JavaScript‑sniffer to compromise 12 eCommerce websites. The malware harvests user data and injects malicious scripts, threatening customer privacy and site integrity. Defenders should scan for the sniffer payload, block its delivery, and patch any exposed endpoints.
Read briefing