
Advisories
FBI Arrests ShinyHunters Operatives Following FBIjobs.gov Breach
The FBI detained three individuals linked to the ShinyHunters group after a breach of the FBIjobs.gov domain exposed sensitive employee data. The attack leveraged a known Oracle vulnerability and was traced to an unpatched Accenture contractor. Defenders should verify Oracle patch status, review access controls on recruitment portals, and monitor for similar data exfiltration patterns.
What Happened
The FBI reported the arrest of a Canadian national in Pennsylvania and a separate detainment in Jordan of a key ShinyHunters member, Saif al‑Din Khader. These arrests follow earlier detentions of Dutch national Pepijn van der Stap and the group’s takeover of the FBIjobs.gov domain.
Impact
The breach compromised personal and medical data for FBI employees and local police officers, and exposed thousands of records. The attackers exploited a publicly known Oracle software vulnerability that had not been patched by the FBI’s contractor, Accenture.
What to Do
- Confirm all Oracle components are updated to the latest security patches.
- Audit and harden access controls on all public-facing recruitment portals.
- Implement continuous monitoring for anomalous data exfiltration, especially from privileged accounts.
- Review contractor security practices and enforce strict patch management policies.
Next Steps
Defenders should collaborate with law enforcement and threat intelligence feeds to track ShinyHunters activity and share indicators of compromise. Maintain an incident response plan that includes procedures for handling personal data breaches.
Related articles
ShinyHunters Group Faces Double Arrests; FBI Targets Operations
Two ShinyHunters operatives were detained—Saif al‑Din Khader in Jordan and Pepijn van der Stap in the Netherlands—after the FBI announced its intent to pursue the group. The attackers have targeted high‑profile victims, including the FBI, using social engineering and software exploits such as a PeopleSoft vulnerability.
Read briefing
FBI Arrests Suspect in ShinyHunters Data Breach of Internal Agent Records
In September, the ShinyHunters hacking group publicly claimed to have exfiltrated a large set of FBI agent data. The FBI has arrested an associate of the group, marking a significant internal security breach. Defenders should review internal data access controls and monitor for similar exfiltration attempts.
Read briefing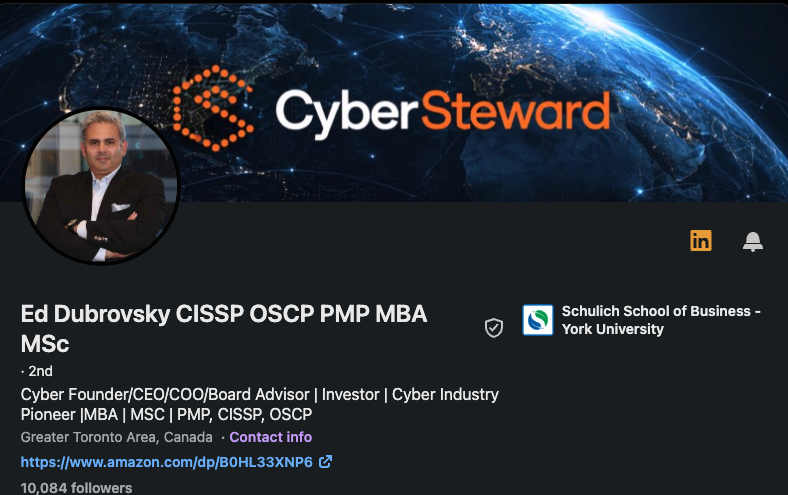
FBI Arrests Ransomware Negotiation Firm Founder Linked to ShinyHunters
The FBI arrested Edward Dubrovsky, co-founder of Cypfer and CyberSteward, in Pennsylvania on charges related to cyber extortion and conspiracy. This arrest connects to the ongoing investigation into the ShinyHunters hacking group, which previously compromised FBI data. Defenders should review policies regarding engagement with ransomware negotiation firms.
Read briefing
FBI Removes Accenture Contractor After Patch Failure Exposes Thousands of Employees in ShinyHunters Breach
The FBI terminated an Accenture contractor after a failure to apply an Oracle PeopleSoft patch enabled the ShinyHunters group to exfiltrate personal data of thousands of bureau employees. The breach exploited CVE‑2026‑35273 via a URL‑encoding trick that bypassed the WAF protecting the Environment Management Hub endpoint. Defenders should verify patch status, harden PeopleSoft deployments, and audit WAF rules for similar bypasses.
Read briefing