
Threat Intel
FBI Seizes Domains Behind Chinese State‑Sponsored MicroScan & FishHub Tools
The FBI seized seven domains that supported the Chinese state‑sponsored hacking tools MicroScan and FishHub, used by the Flax Typhoon group to scan and breach critical infrastructure worldwide. The tools were operated by Integrity Technology Group, a China‑linked contractor. Defenders should block the domains, monitor for scanning activity, and ensure patched systems to mitigate exploitation.
What happened
The FBI seized seven domains that were the backbone of the Chinese state‑sponsored hacking tools MicroScan and FishHub, operated by the Flax Typhoon group.
Impact
These tools performed automated vulnerability scans and, in some cases, launched intrusions against critical infrastructure networks in the United States and abroad. The operators were linked to Integrity Technology Group, a China‑based contractor with alleged government ties.
What to do
- Block the seized domain names and any subdomains that may still be active.
- Deploy network monitoring to detect scanning signatures similar to MicroScan and FishHub.
- Verify that all systems are patched against known CVEs that the tools target.
- Share indicators of compromise with threat‑intel feeds and update your IDS/IPS signatures.
Additional Context
“Integrity Technology Group provided China‑linked threat actors with capabilities used to conduct widespread vulnerability scanning and, in some cases, intrusions targeting U.S. and foreign critical infrastructure,” said FBI Cyber Division.
Related vulnerabilities
FBI Arrests ShinyHunters Operatives Following FBIjobs.gov Breach
The FBI detained three individuals linked to the ShinyHunters group after a breach of the FBIjobs.gov domain exposed sensitive employee data. The attack leveraged a known Oracle vulnerability and was traced to an unpatched Accenture contractor. Defenders should verify Oracle patch status, review access controls on recruitment portals, and monitor for similar data exfiltration patterns.
Read briefing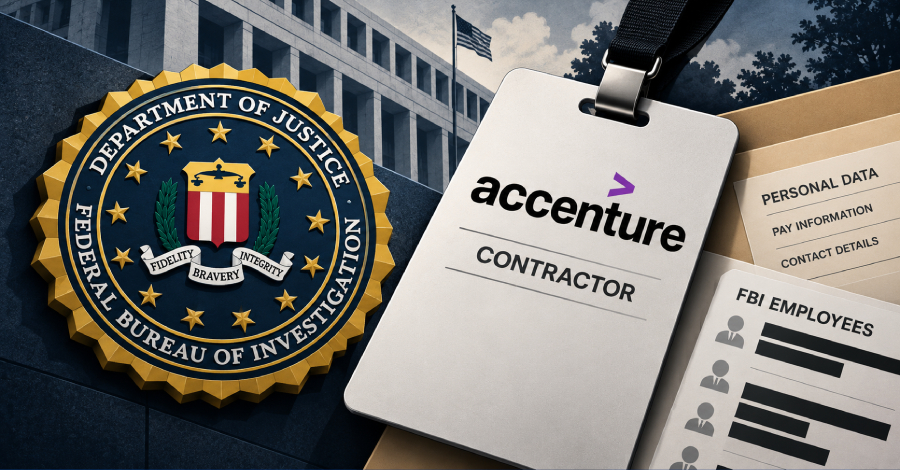
FBI Removes Accenture Contractor After Patch Failure Exposes Thousands of Employees in ShinyHunters Breach
The FBI terminated an Accenture contractor after a failure to apply an Oracle PeopleSoft patch enabled the ShinyHunters group to exfiltrate personal data of thousands of bureau employees. The breach exploited CVE‑2026‑35273 via a URL‑encoding trick that bypassed the WAF protecting the Environment Management Hub endpoint. Defenders should verify patch status, harden PeopleSoft deployments, and audit WAF rules for similar bypasses.
Read briefing
OpenAI Engineer Arrested for Installing Hidden Listening Device in Conference Room
A 35‑year‑old Saudi national employed by OpenAI was arrested after a covert audio recorder was discovered in a company conference room. The device was traced to the employee, who was terminated and charged. Defenders should audit physical security, monitor for hidden devices, and enforce insider‑threat controls.
Read briefing
U.S. Government Disrupts DPRK‑Linked FAMOUS CHOLLIMA Laptop Farms with CrowdStrike Support
The FBI and CrowdStrike dismantled several laptop farms operated by the DPRK‑affiliated threat group FAMOUS CHOLLIMA, exposing fraudulent use of compromised laptops within U.S. companies. Defenders should audit remote‑access logs, isolate affected devices, and strengthen endpoint detection and response controls.
Read briefing