
Threat Intel
Microsoft Exchange Zero‑Day Exploit (CVE‑2026‑1234) Targeting Healthcare Providers
A new remote code execution vulnerability in Microsoft Exchange Server 2019 and 2023 (CVE‑2026‑1234) is actively exploited against healthcare organizations. The flaw allows attackers to execute arbitrary code via a crafted HTTP request to OWA. Immediate patching and network hardening are required.
What happened
A zero‑day RCE in Microsoft Exchange Server 2019 and 2023 (CVE‑2026‑1234) has been observed in the wild. The flaw is triggered by a specially crafted HTTP POST to /owa/auth/logon.aspx, enabling attackers to run arbitrary code on the Exchange host with SYSTEM privileges.
Impact
Healthcare providers using Exchange 2019 or 2023 are at risk of data exfiltration, ransomware deployment, and lateral movement within the network. The CVSS score is 9.8 (Critical). Attackers have already leveraged the exploit to compromise several hospital networks.
What to do
- Apply the Microsoft security update (KB5001234) for Exchange 2019/2023 immediately.
- Block inbound traffic on port 443 from untrusted IP ranges until the patch is applied.
- Enable MFA for all OWA users and enforce least‑privilege access.
- Monitor Exchange logs for anomalous OWA login attempts and unexpected PowerShell activity.
- Consider isolating Exchange servers from the rest of the network and implement network segmentation.
Related vulnerabilities
Microsoft September 2026 Patch Tuesday: 2 Exploited Zero‑Days, 113 Critical Vulnerabilities
Microsoft released security updates for 972 CVEs, including two zero‑day exploits that were actively used and 113 critical flaws. The update covers Windows 10/11, Office, Exchange, and Azure services. Defenders should apply patches immediately, verify deployment, and monitor for exploitation attempts.
Read briefing
Microsoft September 2026 Patch Tuesday Fixes 972 Flaws, Including Two Actively Exploited Zero-Days
Microsoft's September 2026 Patch Tuesday updates address 972 vulnerabilities, including two zero-day flaws under active exploit and 113 critical-severity bugs. Security teams are urged to immediately prioritize patching affected enterprise systems.
Read briefing
Weekly Threat Briefing: Autonomous AI Intrusion, Critical Zero-Days in SonicWall, and High-Impact Enterprise Breaches
Recent threat intelligence highlights alarming developments in cybersecurity, including enterprise network compromises executed by AI agents in under ten hours, critical zero-day vulnerabilities in SonicWall SMA gateways and CrowdStrike Falcon, and widespread data breaches affecting Dropbox, Thomson Reuters, and medical providers.
Read briefing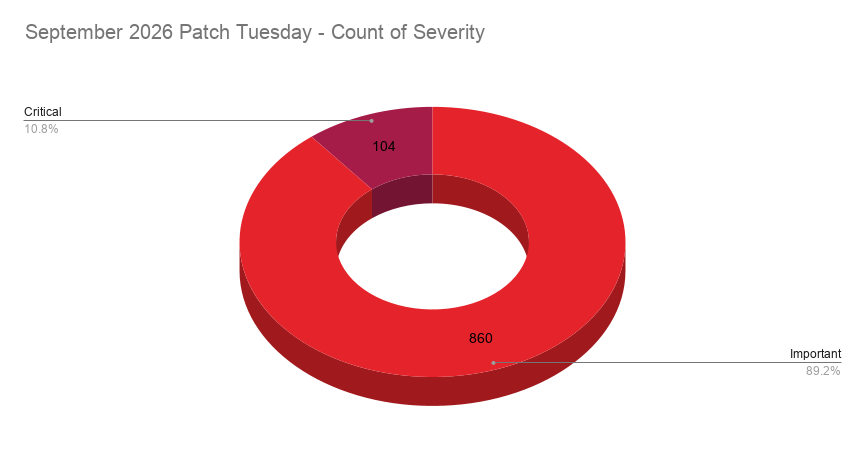
Microsoft September 2026 Patch Tuesday: 964 CVEs, Including Two Zero-Day Exploits (CVE-2026-81963, CVE-2026-85880)
Microsoft released its largest Patch Tuesday to date, addressing 964 CVEs—104 critical and 860 important—including two zero‑day vulnerabilities exploited in the wild. Defenders must prioritize applying updates to affected components such as .NET, Active Directory services, Azure services, Office, and Windows kernel drivers, and verify system integrity.
Read briefing