
Vulnerabilities
Microsoft Releases 570 Vulnerability Fixes, Including 3 Zero‑Days and 60 Critical Issues
Microsoft’s latest Patch Tuesday fixed 570 security flaws across Windows and related products, including three zero‑day vulnerabilities and 60 critical bugs that could allow remote control or privilege escalation. Defenders should apply updates immediately, verify affected components, and monitor for exploitation of the newly disclosed CVEs.
What Happened
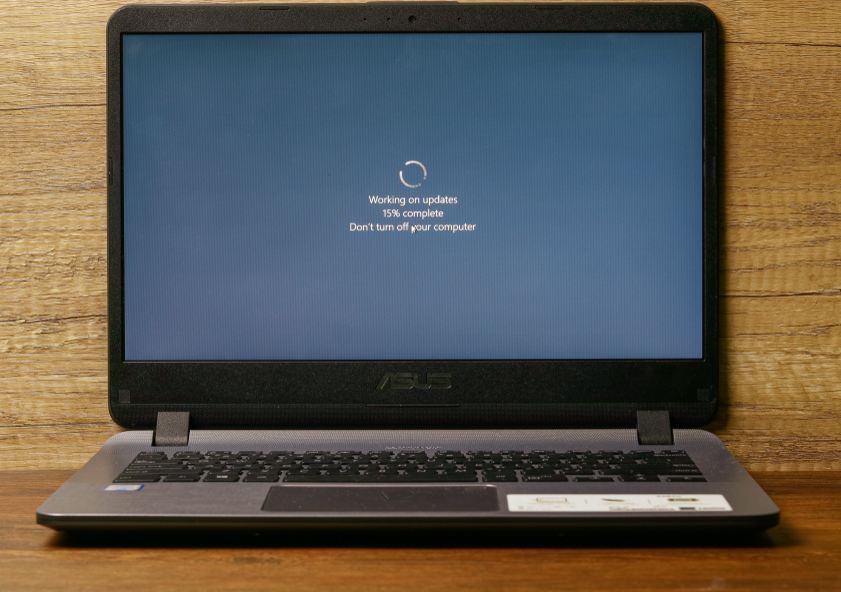
Microsoft released a Patch Tuesday update addressing at least 570 security holes across Windows OS and other Microsoft products, nearly triple the number fixed in the previous month.
Impact
Of the patches, 60 were rated critical, enabling attackers to gain remote control with minimal user interaction. Three zero‑day flaws were also fixed, two of which are actively exploited.
Immediate Actions
- Apply the latest updates to all Windows machines and related Microsoft products.
- Verify that the update includes the CVE‑2026‑56155 (ADFS), CVE‑2026‑56164 (SharePoint), CVE‑2026‑50661 (BitLocker), and CVE‑2026‑48561 (Copilot) fixes.
- Enable automatic updates where possible to reduce exposure time.
Specific CVEs to Watch
- CVE‑2026‑56155 – ADFS elevation of privilege.
- CVE‑2026‑56164 – SharePoint privilege escalation.
- CVE‑2026‑50661 – BitLocker security feature bypass.
- CVE‑2026‑48561 – Copilot remote code execution via malicious website.
AI‑Driven Discovery
Microsoft attributes the surge in discovered flaws to AI tools that accelerate vulnerability hunting across codebases.
Defenders should anticipate more frequent, AI‑identified patches and maintain rigorous patch management processes.
Related vulnerabilities
Microsoft October 2026 Patch Tuesday: 1,413 CVEs, 3 Zero‑Days, 75 Critical Vulnerabilities
Microsoft released security updates for 1,413 CVEs, including three zero‑days—one actively exploited—and 75 critical flaws. The update covers Windows, Office, and Azure services. Defenders should apply patches immediately, verify affected components, and monitor for exploitation attempts.
Read briefing
Microsoft Patch Tuesday 2026: 972 CVEs, 113 Critical, 2 Exploited Zero‑Days
Microsoft’s September 2026 Patch Tuesday saw the release of 972 security fixes, including 113 critical issues and two zero‑days that had already been weaponized. The updates span Windows, Office, and other key Microsoft products, underscoring the urgency for rapid patch deployment across all environments.
Read briefing
Microsoft Patch Tuesday 2026: 972 CVEs, 113 Critical, 2 Exploited Zero‑Days
Microsoft released security updates for 972 CVEs in September 2026, including 113 critical issues and two zero‑days that were actively exploited. Defenders must prioritize patching affected systems, validate deployment, and monitor for exploitation indicators.
Read briefing
Microsoft Patch Tuesday 2026: 972 CVEs, 113 Critical, 2 Exploited Zero‑Days
Microsoft released updates for 972 vulnerabilities in September 2026, including 113 critical flaws and two zero‑days that were actively exploited. Defenders must prioritize patching, verify deployment, and monitor for exploitation indicators.
Read briefing