
Advisories
Microsoft September 2026 Patch Tuesday Addresses Record 974 Vulnerabilities
Microsoft's September 2026 Patch Tuesday marks its largest security update to date, addressing 974 vulnerabilities, including two actively exploited zero-days. Sysadmins and SecOps teams must prioritize the deployment of fixes covering critical components like Hyper-V, Windows HTTP.sys, and Exchange Server. Additionally, Adobe released advisories covering 170 vulnerabilities across its product ecosystem.
What Happened
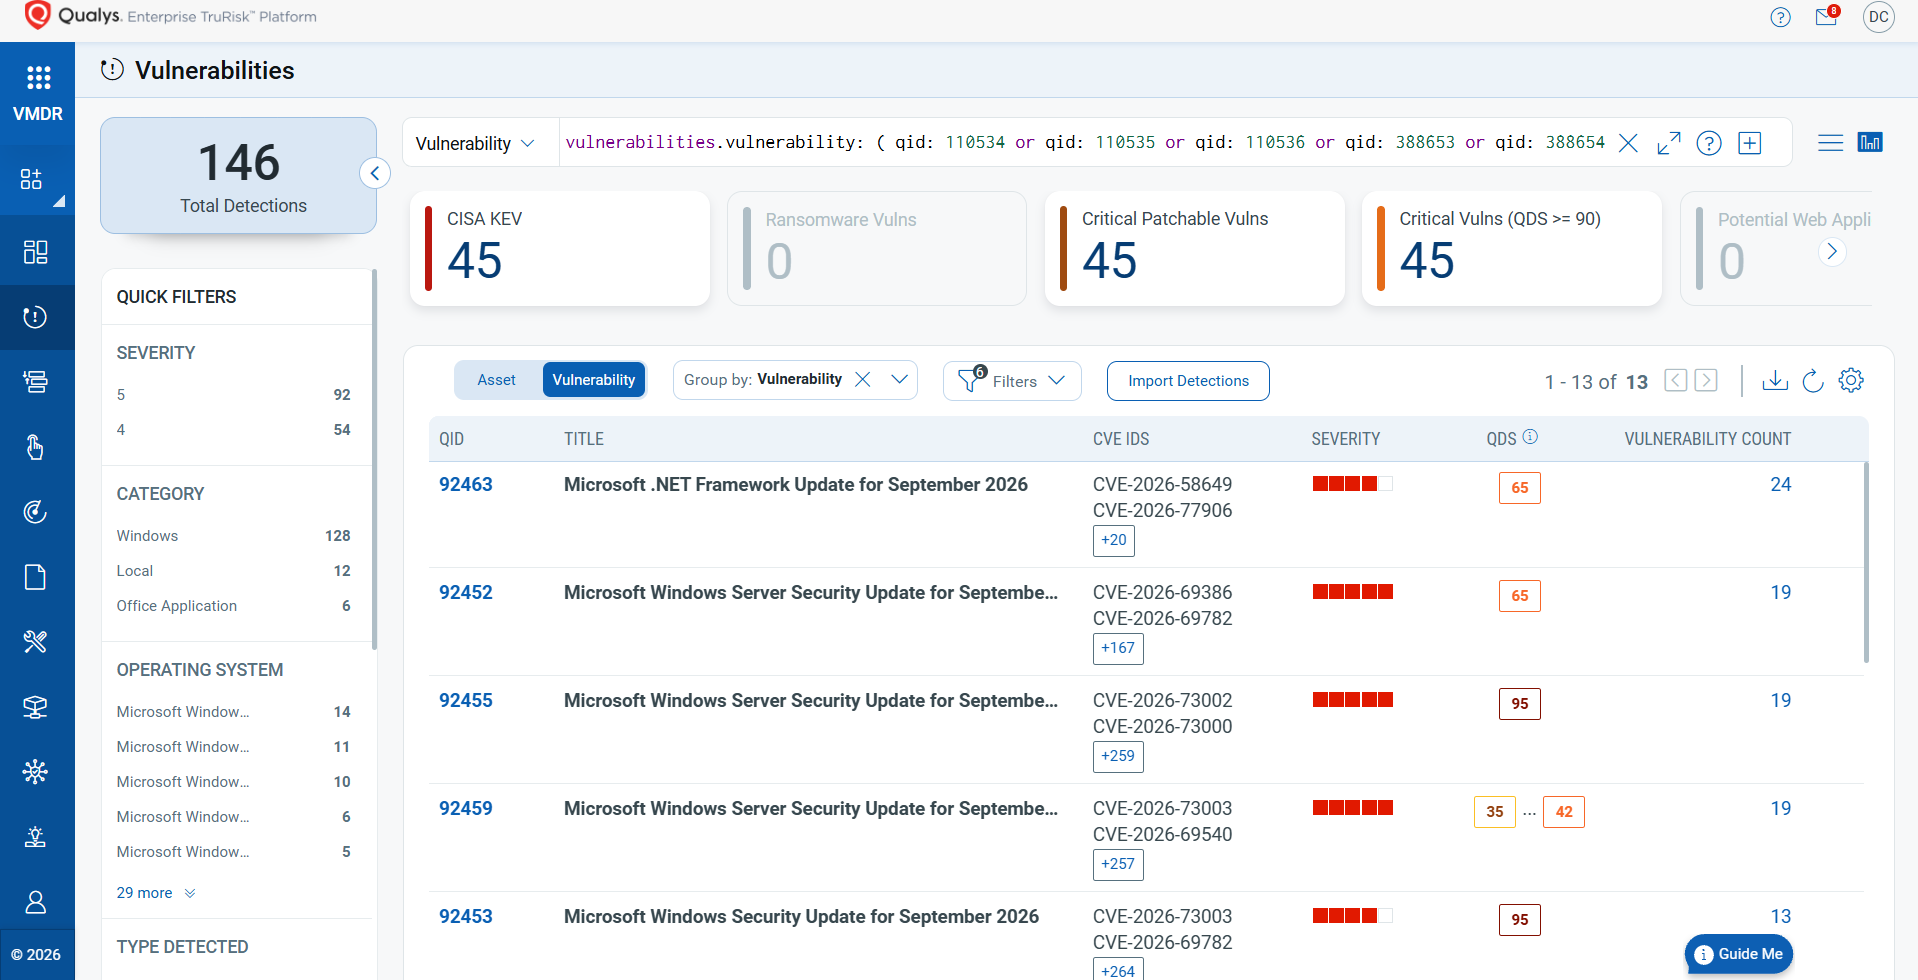
Microsoft has issued its largest security update ever for September 2026, delivering patches for 974 distinct vulnerabilities across its product ecosystem. The release includes 113 critical-severity and 860 important-severity flaws, alongside two vulnerabilities confirmed to be under active exploitation in the wild. Notably, the update covers core infrastructure and developer tooling such as Windows HTTP.sys, Windows Hyper-V, Exchange Server, Entra ID, GitHub Copilot, and Visual Studio Code. Concurrently, Adobe published nine advisories addressing 170 vulnerabilities.
Vulnerability Breakdown
The vast volume of patches spans multiple vulnerability classes, heavily weighted toward elevation of privilege and remote code execution vectors:
- Elevation of Privilege: 438 flaws (27 critical, 411 important)
- Remote Code Execution: 253 flaws (82 critical, 171 important)
- Information Disclosure: 173 flaws (2 critical, 171 important)
- Denial of Service: 56 flaws (56 important)
- Security Feature Bypass: 19 flaws (1 critical, 18 important)
- Spoofing: 16 flaws (1 critical, 15 important)
Impact
Due to the massive scope of the update—surpassing recent months which averaged 400 to 570 fixes—organizations face a high operational burden to maintain patch hygiene. Unpatched systems remain exposed to potential remote code execution, privilege escalation, and denial-of-service vectors, compounded by the presence of active exploitation vectors in the wild. Edge (Chromium-based) is notably absent from this month's Microsoft advisories.
What to Do
SecOps and sysadmins should immediately ingest vulnerability telemetry, prioritize endpoints running exposed services like Hyper-V and Exchange Server, and expedite patch deployment to mitigate zero-day risk.
- Run internal vulnerability scans using authenticated agents to map affected hosts against the September 2026 dataset.
- Prioritize remediation for the two actively exploited flaws and the 113 critical-severity CVEs.
- Review Adobe advisories and schedule corresponding application updates to address the 170 newly disclosed third-party vulnerabilities.
Related vulnerabilities
Microsoft September 2026 Patch Tuesday Fixes 972 Flaws, Including Two Actively Exploited Zero-Days
Microsoft's September 2026 Patch Tuesday updates address 972 vulnerabilities, including two zero-day flaws under active exploit and 113 critical-severity bugs. Security teams are urged to immediately prioritize patching affected enterprise systems.
Read briefing
Microsoft Unleashes 972 CVE Fixes on Patch Tuesday, Including 2 Exploited Zero‑Days and 113 Critical Flaws
Microsoft’s September 2026 Patch Tuesday update tackles 972 CVEs—two of which are actively exploited zero‑days and 113 critical vulnerabilities. The patch covers Windows, Office, and other Microsoft components, tightening defenses across the ecosystem. Security teams should apply the fixes immediately and monitor for any lingering exploitation attempts.
Read briefing
Microsoft Patch Tuesday 2026: 972 CVEs, 113 Critical, Two Exploited Zero‑Days
Microsoft’s September 2026 Patch Tuesday saw 972 vulnerabilities patched, including 113 rated critical and two zero‑days that were already in the wild. CrowdStrike’s latest security releases emphasize supply‑chain protection and AI‑driven SOC evolution, underscoring the need for rapid patching and advanced detection.
Read briefing
Microsoft Patch Tuesday: 972 CVEs, 113 Critical, 2 Exploited Zero‑Days
Microsoft’s September 2026 Patch Tuesday saw the release of security updates for 972 vulnerabilities, including 113 critical flaws and two zero‑days that had already been leveraged by attackers. The roll‑out underscores the ongoing urgency of patching across the Microsoft ecosystem and highlights the scale of the patching effort required to stay ahead of emerging threats.
Read briefing