
Threat Intel
Mirage Kitten APT Deploys NodeRabbit and PollCat RATs via Trojanized Coding Challenges
Kaspersky researchers have uncovered new campaigns by the Mirage Kitten threat group targeting aviation and FinTech sectors in the Middle East and Africa. The attacks utilize two previously undocumented cross-platform remote access trojans, NodeRabbit and PollCat, delivered via malicious job application coding challenges.
What Happened
The Mirage Kitten advanced persistent threat (APT) group has launched a targeted campaign against aviation and financial technology organizations across the Middle East and Africa. Researchers identified a shift in the group's tooling, moving away from traditional C, C++, and Go binaries to leverage two new, cross-platform remote access trojans (RATs): NodeRabbit and PollCat.
Delivery occurs primarily through spear-phishing on professional networks like LinkedIn and job search platforms. Attackers lure targets with fake engineering assessments packaged as software development archives, such as 'Front-Technical-Challenge.zip'.
Technical Impact & Delivery Mechanism
- NodeRabbit: A cross-platform RAT developed in Node.js targeting Windows, Linux, and macOS systems. Advanced variants have been identified on enterprise systems in Afghanistan, Egypt, and Ethiopia.
- PollCat: An obfuscated JavaScript-based cross-platform RAT deployed alongside or within the same malicious project structures.
- Initial Access: Victims download an Amazon S3-hosted archive containing a seemingly legitimate assessment app (TaskFlow) built with Express, React, and Vite.
- Evasion Tactics: The accompanying README file instructs candidates not to modify 'server.js'—claiming it is bug-free—while prohibiting AI code assistants to prevent automated auditing from flagging malicious first-line imports of unauthorized npm packages.
What Defenders Should Do
- Warn HR and recruitment teams regarding targeted spear-phishing campaigns masquerading as technical interviews or coding challenges on LinkedIn.
- Implement strict endpoint monitoring for unauthorized execution of Node.js runtimes and suspicious npm package installations within development environments.
- Scan development archives downloaded from external sources, specifically auditing project dependencies and backend entry points (such as server.js) prior to execution.
- Block known indicators of compromise, including the identified S3 bucket infrastructure used for payload hosting.
Related articles
Star Blizzard Shifts to RedFlick Phishing, Deploys CosmicPulse Backdoor
Star Blizzard, a Russia‑linked APT group, has moved from ClickFix to a new phishing technique called RedFlick, enabling delivery of the CosmicPulse backdoor with reduced user interaction. The change targets Ukrainian‑linked NGOs, think tanks, and journalists, increasing compromise likelihood and evasion of detection. Defenders should update email filters, deploy EDR signatures, and monitor for CosmicPulse indicators.
Read briefing
MovieReaper Campaign Uses Compromised Torrents and Solana Blockchain for C2
A new multi-stage malware framework dubbed MovieReaper is distributing trojanized installers via compromised torrent storage repositories, impacting users and organizations globally. The campaign leverages the Solana blockchain to conceal its command and control infrastructure and employs evasion techniques to bypass sandbox detection.
Read briefing
North Korean APT Breaches South Korean Media and Auto Firms via New Linux Toolkit on HAProxy Load Balancers
A suspected North Korean APT deployed a previously undocumented Linux espionage toolkit, dubbed "TED," to compromise HAProxy load balancers in South Korean media and automotive companies. The attackers leveraged the compromised appliances to harvest credentials, redirect traffic, and execute drive‑by downloads, fitting the DPRK pattern of long‑term espionage via trusted software. Rapid7 links the activity to APT37 with medium confidence, highlighting the dual focus on information control and manufacturing IP.
Read briefing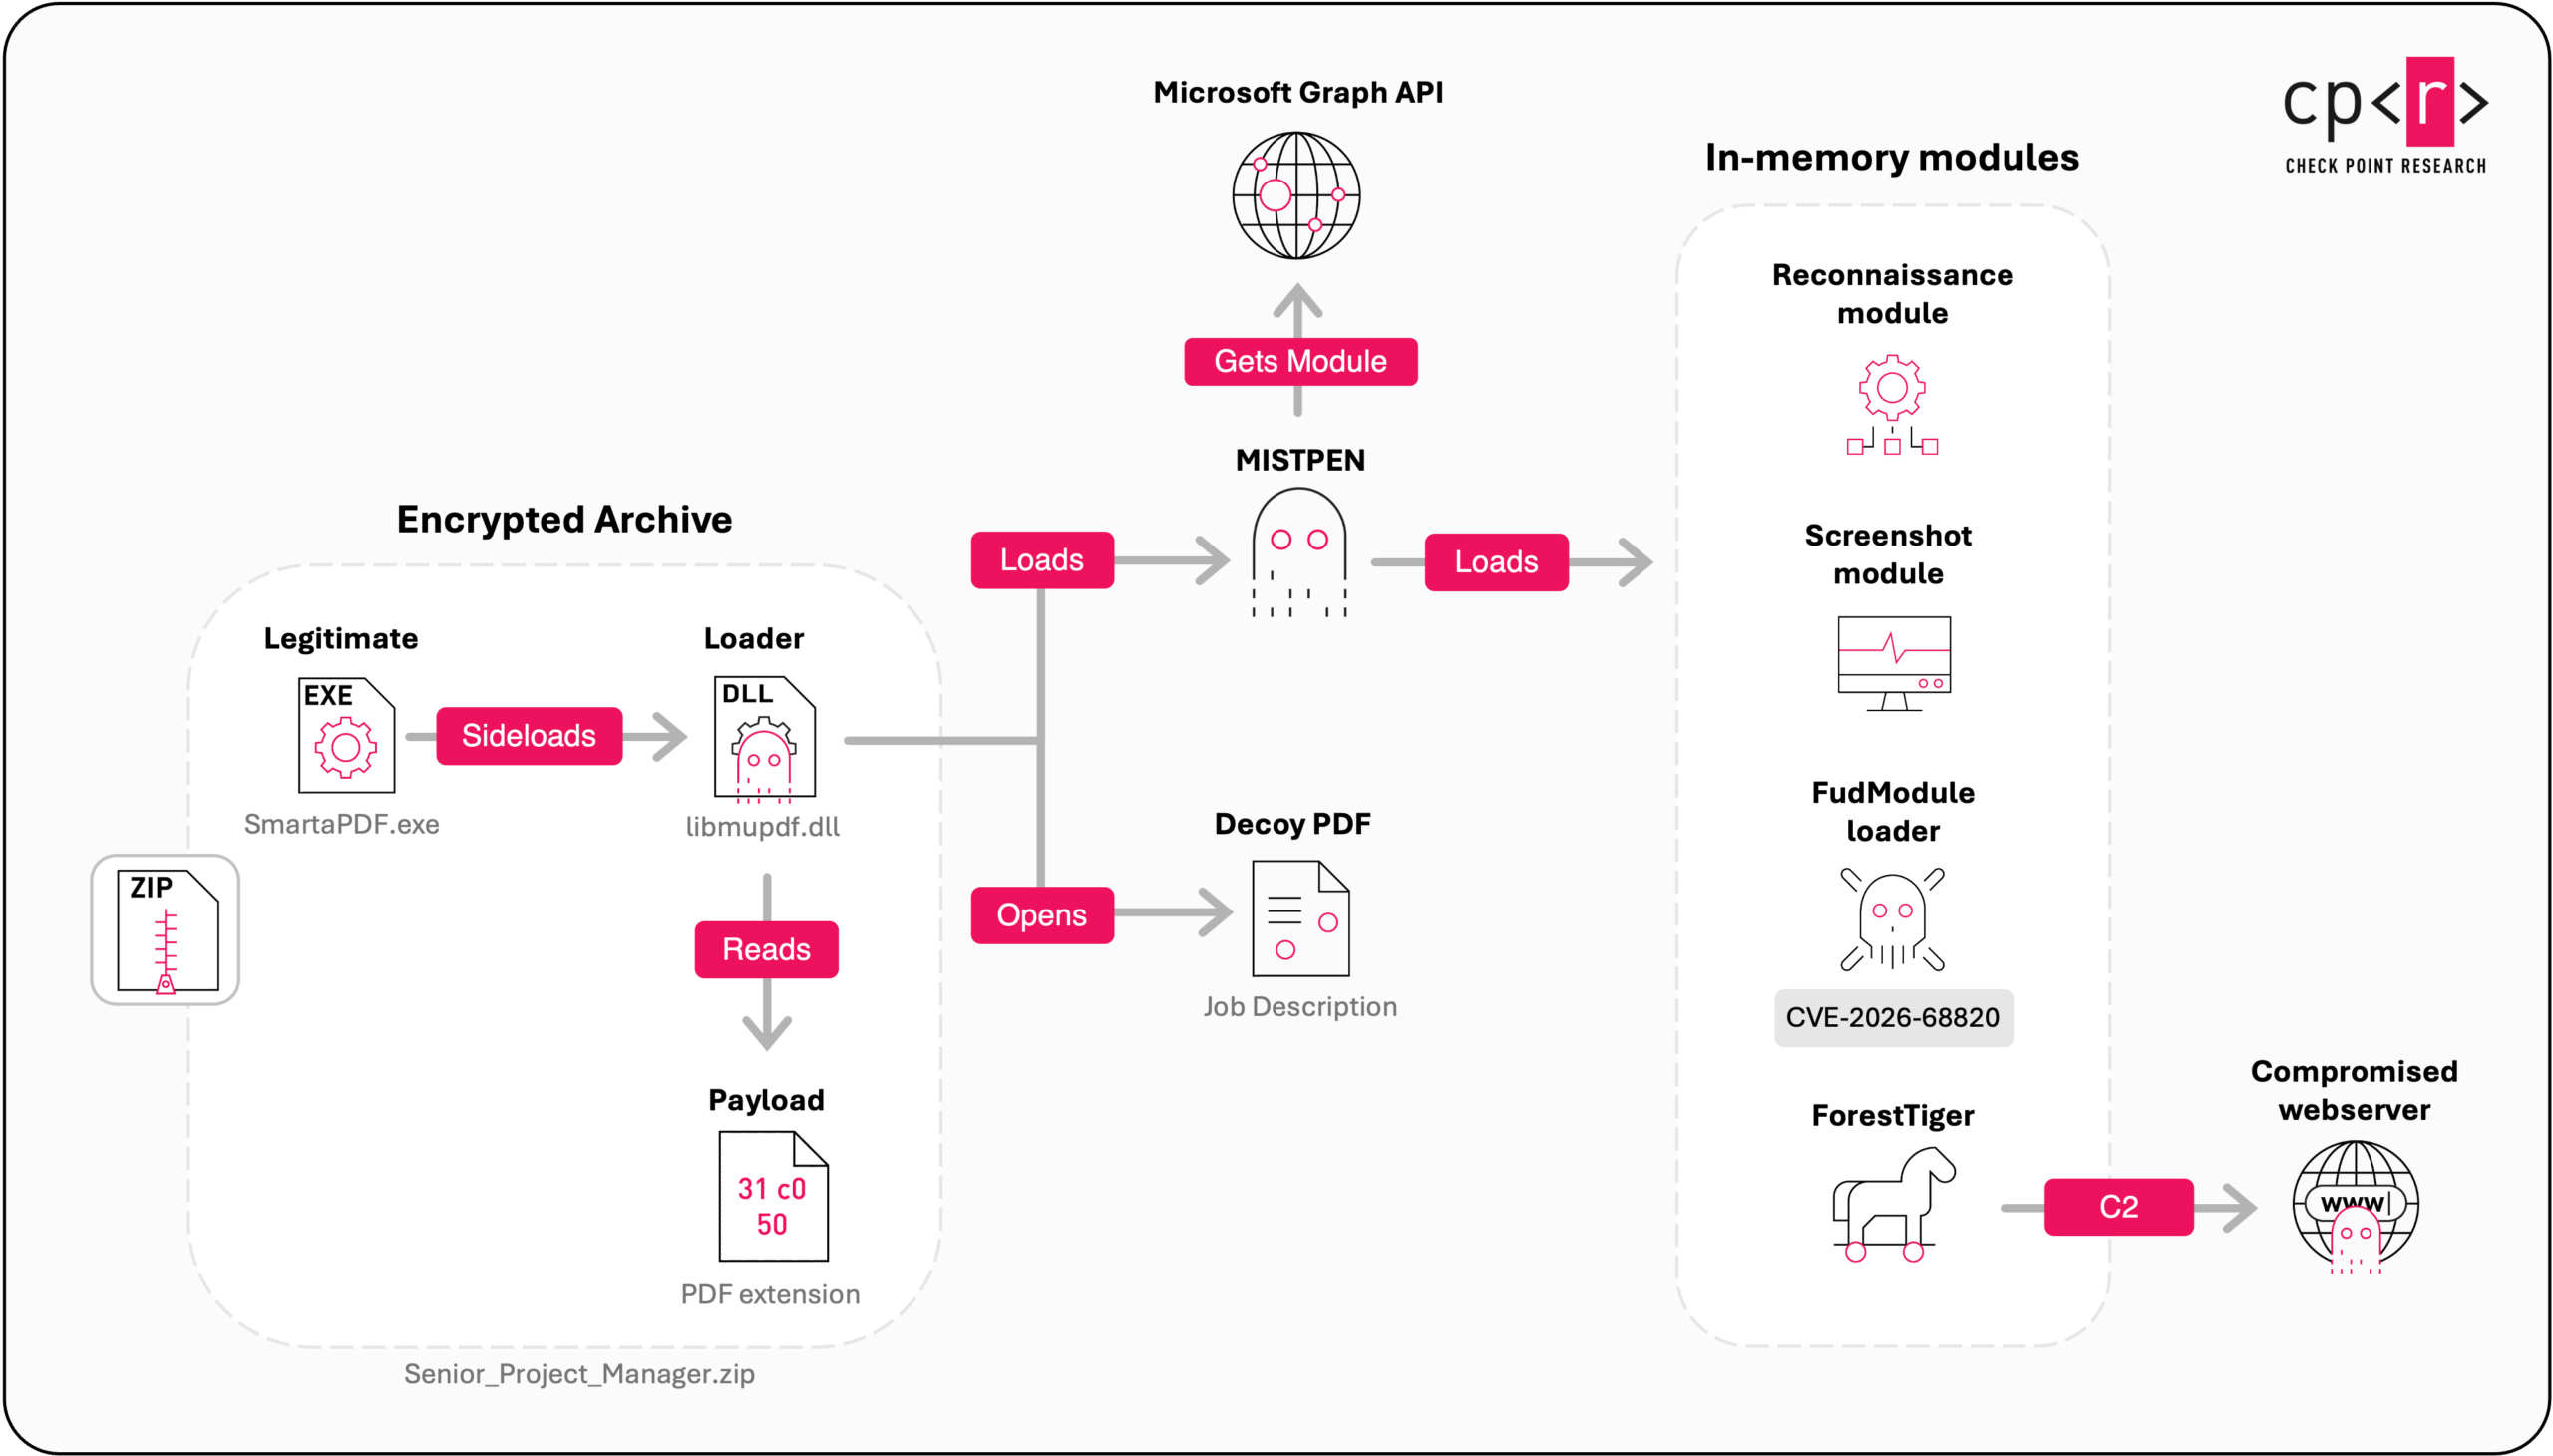
Operation Dream Job: From Job Offers to Zero‑Day Attacks on Defense Sectors
Check Point Research has traced a fresh wave of the Operation Dream Job campaign, a Lazarus‑linked effort that turns enticing job ads into a multi‑stage breach. The attackers now use a trojanized PDF viewer, the SecurityPDF app, to deliver a new kernel‑mode rootkit (FudModule) via the zero‑day CVE‑2026‑68820 in Microsoft’s AFD.sys driver. They also weaponize CVE‑2025‑49113 in Roundcube to plant RelayShell webshells, turning compromised servers into covert C2 relays. The campaign targets aerospace, aviation and defense firms worldwide, leveraging spear‑phishing, SEO‑boosted fake recruitment sit
Read briefing