
Cloud Security
TeamFiltration Brute-Force Campaign Compromises Microsoft 365 Service Accounts
An active threat campaign tracked as UNK_CondorFiltration utilized AWS infrastructure to target over 5,700 Microsoft 365 accounts across 28 tenants in July and August 2026. Researchers attribute seven successful compromises directly to unmanaged service accounts utilizing unrotated default passwords and lacking multi-factor authentication.
What Happened
Security researchers have detailed a targeted brute-force campaign codenamed UNK_CondorFiltration, which leveraged nearly 1,500 unique AWS EC2 IP addresses to assault Microsoft 365 tenants. The activity spanned three distinct operational waves between late July and mid-August 2026, primarily focusing on financial and retail organizations in Chile. Attackers executed credential-spraying techniques against more than 5,700 accounts.
Impact
The campaign resulted in the successful compromise of seven Microsoft 365 accounts. Notably, all compromised entities were unmanaged functional or service accounts rather than individual employee profiles. Investigators found that six of the seven accounts were breached within seven minutes of the attack wave, pointing to the use of static, non-rotated default credentials assigned during initial provisioning.
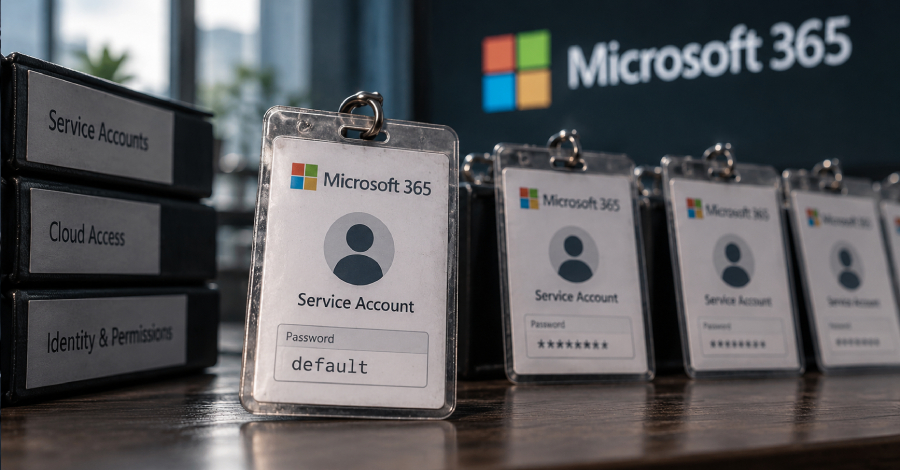
Every successful compromise has been linked to unmonitored service accounts with a default password.
What to Defend
Defenders and system administrators managing cloud identity providers must audit tenant environments for unmonitored non-human identities. Key remediation steps include:
- Enforce mandatory multi-factor authentication (MFA) across all functional, service, and administrative accounts without exception.
- Implement strict password rotation policies for non-human identities to eliminate static, vendor-supplied default credentials.
- Monitor sign-in logs for high-velocity authentication attempts originating from cloud hosting provider IP ranges such as AWS EC2.
- Identify and disable dormant or orphaned service accounts that are no longer required for active business operations.
Related articles
Falcon Data Security for SaaS Enhances Microsoft 365 Data Protection
Falcon Data Security for SaaS now protects SharePoint, OneDrive, and Copilot, enabling automated discovery and classification of sensitive data across Microsoft 365. The update applies to all tenants with the service enabled and offers tighter compliance controls. Defenders should enable coverage, set classification policies, and integrate alerts into existing workflows.
Read briefing
Mitigating Stale Sharing Risks in Microsoft 365 Through Access Governance
Microsoft 365 environments frequently accumulate stale file-sharing permissions and orphaned links, leaving sensitive enterprise data exposed. SecOps and sysadmins must implement centralized access governance and owner-driven reviews to audit permissions and revoke unnecessary access.
Read briefing
Proofpoint Expands AI Investigations to Microsoft 365 and Insider Risk Platforms
Proofpoint has rolled out updates to its security portfolio, adding AI-powered investigative capabilities for Microsoft 365 environments alongside enhanced tracking for enterprise AI usage. The updates aim to streamline incident triage and improve visibility into potential data exfiltration vectors involving generative AI tools.
Read briefing
FortiBleed Attackers Lock Out Legitimate Users on Fortinet Devices
Attackers using compromised credentials and brute‑force methods have taken control of over 86,000 Fortinet FortiGate firewalls and SSL‑VPN appliances worldwide, creating new accounts and deleting legitimate ones to lock out defenders. The campaign, linked to a Russian initial‑access broker, underscores the need for immediate credential hygiene, MFA, and network segmentation.
Read briefing