
Threat Intel
ThreatsDay Bulletin: AI‑Powered Zero‑Day Chain, 543K Live Secrets, Model Inspection RCE
ThreatsDay highlighted an AI‑driven zero‑day exploitation chain, a list of 543,000 exposed secrets, and a remote code execution flaw in model inspection tools. Defenders using ML inference services and secret repositories should audit, patch, and harden their systems immediately.
What Happened
ThreatsDay released a bulletin detailing an AI‑driven zero‑day exploitation chain, a catalog of 543,000 publicly exposed secrets, and a remote code execution (RCE) vulnerability in model inspection tools. The zero‑day chain leverages machine‑learning inference services to identify and chain multiple legacy flaws, while the RCE allows attackers to execute arbitrary code during model validation.
Impact
- Organizations using cloud‑based ML inference platforms or on‑prem model serving are at risk of automated exploitation.
- Any service that stores or caches secrets in public or shared repositories may have exposed credentials for years.
- Systems that rely on third‑party model inspection libraries could be compromised without a patch.
Mitigation Steps
- Audit all ML inference endpoints for outdated libraries and apply vendor patches immediately.
- Implement strict secret management: rotate credentials, use vaults, and scan repositories for exposed keys.
- Disable or harden model inspection features; validate inputs against strict schemas before execution.
- Deploy runtime protection (WAF, RCE mitigations) and monitor for anomalous inference traffic.
Next Steps
Regularly review threat intelligence feeds and apply the principle of least privilege to all ML and secret‑handling components.
Related articles
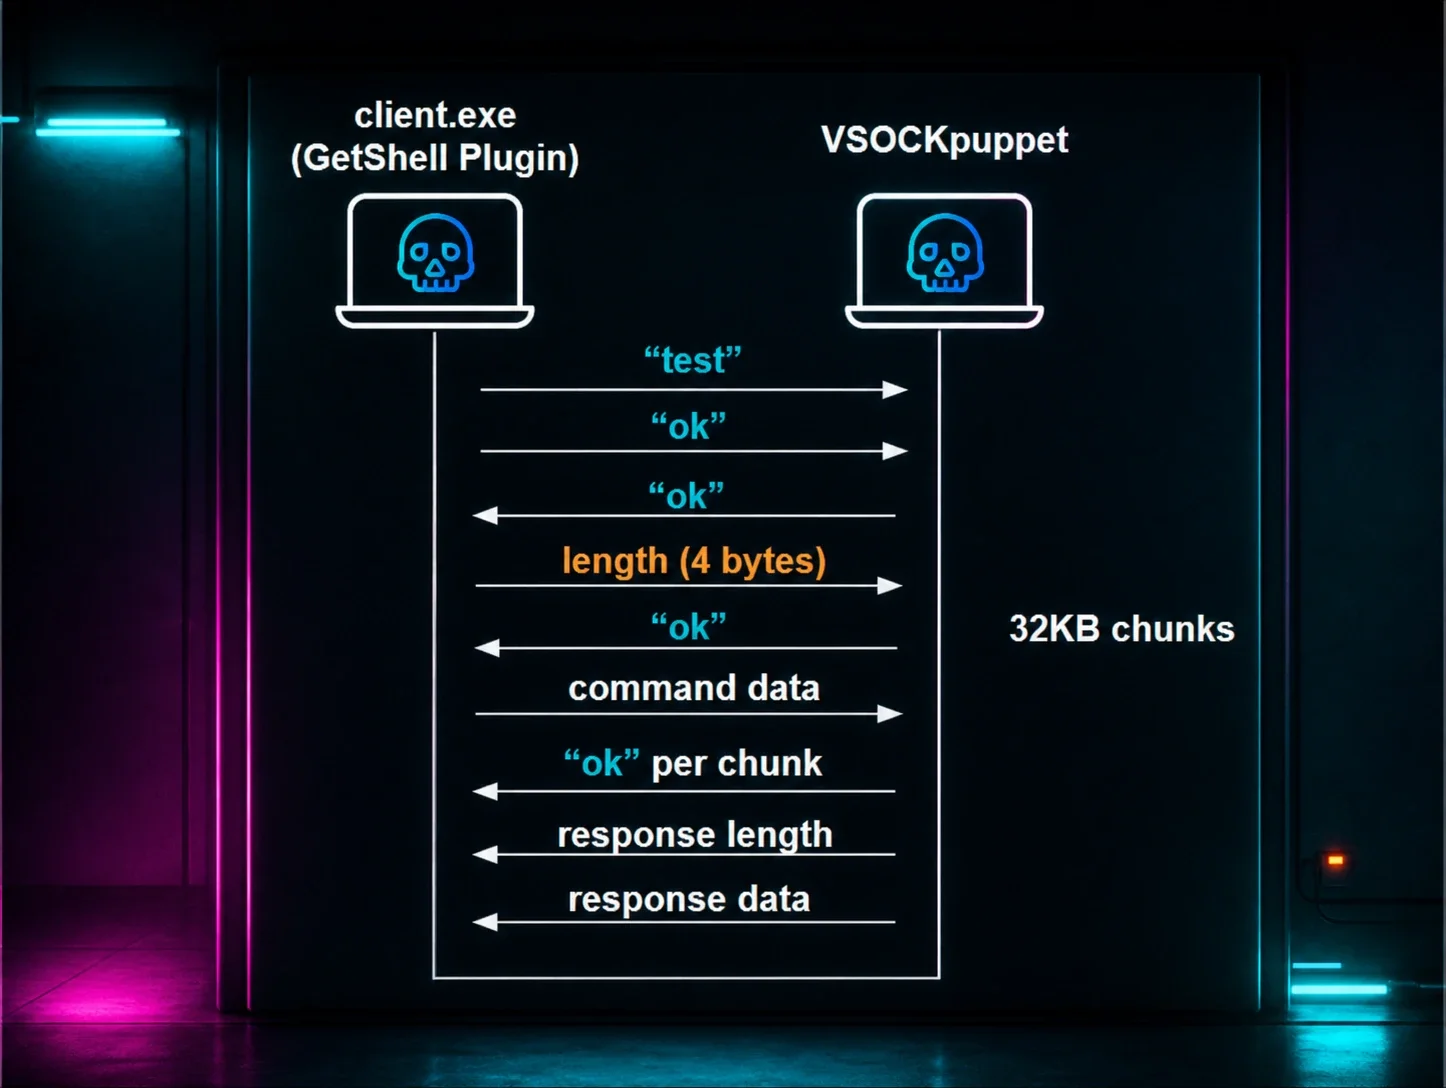
VM Escape via VSOCK: Multi‑Step Attack on ESXi Hypervisors
Huntress uncovered a sophisticated attack chain that exploits potential zero‑day flaws in VMware ESXi, using VSOCK for covert communication to break out of guest VMs. The technique targets the hypervisor layer, threatening all virtualized workloads. Defenders should patch ESXi, disable VSOCK where possible, and monitor hypervisor logs for anomalous activity.
Read briefing
CrowdStrike Enhances Falcon with Real‑Time Supply‑Chain Defense
CrowdStrike has rolled out a new supply‑chain protection layer inside its Falcon endpoint sensor, blocking malicious open‑source packages as they download. The update expands Falcon’s threat‑intelligence reach, allowing defenders to stop supply‑chain attacks before code ever executes on the host. RootPwn breaks down how the feature works, its impact on the attack surface, and what it means for organizations still hunting for zero‑day supply‑chain exploits.
Read briefing
Citrix NetScaler Zero‑Day RCE Vulnerabilities Exploited in the Wild – Immediate Action Required
Two unpatched zero‑day vulnerabilities in Citrix NetScaler allow remote code execution and are actively exploited. The flaws were disclosed by the Dutch NCSC and confirmed by researchers, but no patches exist yet. Defenders must isolate or shut down affected appliances, monitor traffic, and apply mitigations as soon as updates become available.
Read briefing
OpenAI Codex configuration flaw enables user-triggered RCE; patch now
Zero Day Initiative disclosed a Pwn2Own vulnerability in OpenAI Codex that lets an attacker run arbitrary code when a user opens a crafted page or file. The issue stems from insufficient sanitization of configuration settings and is tracked as CVE-2026-19590 with a CVSS 7.8 score. Defenders should apply OpenAI's update, restrict untrusted content, and monitor for unexpected local execution.
Read briefing