
Vulnerabilities
Citrix NetScaler Zero‑Day RCE Vulnerabilities Exploited in the Wild – Immediate Action Required
Two unpatched zero‑day vulnerabilities in Citrix NetScaler allow remote code execution and are actively exploited. The flaws were disclosed by the Dutch NCSC and confirmed by researchers, but no patches exist yet. Defenders must isolate or shut down affected appliances, monitor traffic, and apply mitigations as soon as updates become available.
What Happened
On September 26 2026, reports surfaced that two critical zero‑day vulnerabilities in Citrix NetScaler appliances were being actively exploited in the wild. The flaws enable remote code execution with no authentication and are currently unpatched.
“The Dutch NCSC pre‑notification warned of two zero‑day flaws.”
Impact
All NetScaler versions that have not applied the forthcoming patches are at risk. Attackers can gain full control of the appliance, pivot to internal networks, and exfiltrate data.
Immediate Actions
Defenders should immediately:
- Identify all NetScaler deployments and verify their version.
- If possible, isolate or shut down the appliances from the network.
- Apply any available mitigations (e.g., firewall rules blocking exploit traffic).
- Monitor logs for indicators of compromise such as unexpected RCE attempts.
Next Steps
Stay tuned for official patches from Citrix. Until then, maintain strict network segmentation and consider temporary hardening measures such as disabling unused services.
Related vulnerabilities
Citrix NetScaler Zero-Day Exploitation Targets Government and Finance Sectors
Citrix’s NetScaler ADC and Gateway appliances were hit by two critical zero-day vulnerabilities (CVE‑2026‑88771/72) that enabled remote code execution. Security firms Mandiant and GTIG confirmed attacks from early September, affecting government, finance, education, and legal organizations across North America and Europe. Administrators should immediately isolate affected devices, apply Citrix patches, and monitor for exploitation indicators.
Read briefing
Citrix NetScaler RCE Vulnerability (CVE‑2026‑107406) Requires Immediate Patch
Citrix has disclosed a critical memory‑overflow flaw in NetScaler ADC and Gateway appliances that can be leveraged for remote code execution or denial‑of‑service when configured as a SAML IdP or SP. Affected systems must be upgraded to the latest patched releases without delay. No active exploits reported yet, but defenders should verify patch status and monitor traffic.
Read briefing
Ivanti Connect Secure Zero‑Day Exploited: Immediate Patch Required
An actively exploited authentication‑bypass zero‑day (CVE‑2026‑104935) has been found in Ivanti Connect Secure. The flaw affects versions 22.8R2.4 and earlier, 25.1.2.2 and earlier, and 25.1.1.1 and earlier, allowing unauthenticated remote attackers to run arbitrary commands. Defenders must patch immediately and run the Integrity Checker Tool.
Read briefing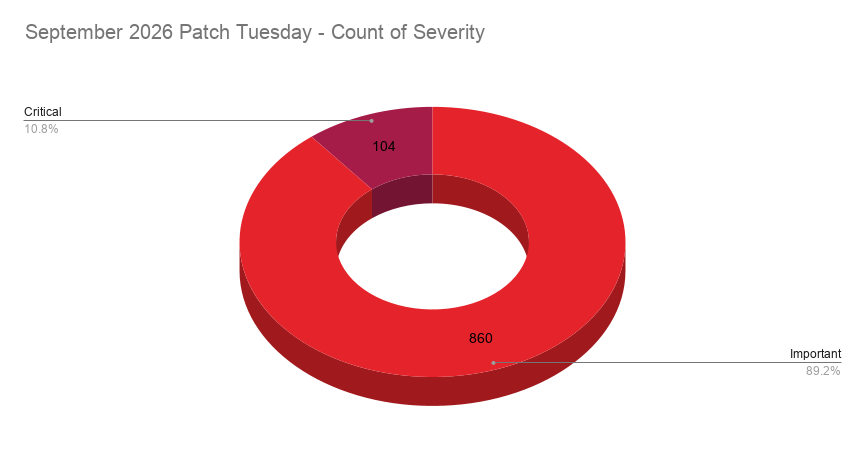
Microsoft September 2026 Patch Tuesday: 964 CVEs, Including Two Zero-Day Exploits (CVE-2026-81963, CVE-2026-85880)
Microsoft released its largest Patch Tuesday to date, addressing 964 CVEs—104 critical and 860 important—including two zero‑day vulnerabilities exploited in the wild. Defenders must prioritize applying updates to affected components such as .NET, Active Directory services, Azure services, Office, and Windows kernel drivers, and verify system integrity.
Read briefing