
Vulnerabilities
Citrix NetScaler Zero-Day Exploitation Targets Government and Finance Sectors
Citrix’s NetScaler ADC and Gateway appliances were hit by two critical zero-day vulnerabilities (CVE‑2026‑88771/72) that enabled remote code execution. Security firms Mandiant and GTIG confirmed attacks from early September, affecting government, finance, education, and legal organizations across North America and Europe. Administrators should immediately isolate affected devices, apply Citrix patches, and monitor for exploitation indicators.
What Happened
Citrix disclosed two critical vulnerabilities in NetScaler ADC and NetScaler Gateway—CVE‑2026‑88771 and CVE‑2026‑88772—that allow attackers to execute arbitrary code remotely. Mandiant and GTIG’s investigations show that the zero‑day campaign began in early September and continued through the month, with attacks observed against a range of organizations.
Impact
Targeted entities include government agencies, financial services firms, educational institutions, and legal and professional service organizations in North America and Europe. Exploitation could lead to full compromise of the affected appliances, enabling lateral movement and data exfiltration.
Mitigation Steps
- Immediately disconnect NetScaler ADC and Gateway appliances from the internet until a patch is applied.
- Apply the latest Citrix security updates released over the weekend that address CVE‑2026‑88771 and CVE‑2026‑88772.
- Verify that the patches are correctly installed and that the vulnerable code paths are no longer reachable.
- Enable logging and monitoring for anomalous traffic or exploitation attempts on the appliances.
- Conduct a post‑incident review to confirm that no persistence mechanisms remain.
“The zero‑day campaign has been ongoing since at least early September,” said Mandiant’s report.
Related vulnerabilities
Citrix NetScaler ADC Vulnerabilities CVE-2026-88771/72 Actively Exploited; Bitget $387M Crypto Theft
Citrix NetScaler ADC and Gateway are under active exploitation due to CVE-2026-88771 and CVE-2026-88772, allowing unauthenticated remote code execution and denial‑of‑service. Bitget cryptocurrency exchange suffered a $387 million theft by North Korean actors. Defenders must patch immediately, monitor for suspicious activity, and review exposed service accounts.
Read briefing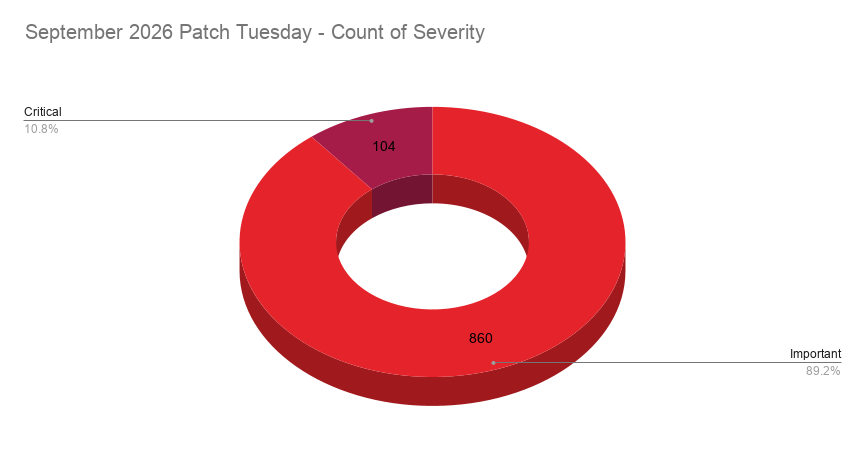
Microsoft September 2026 Patch Tuesday: 964 CVEs, Including Two Zero-Day Exploits (CVE-2026-81963, CVE-2026-85880)
Microsoft released its largest Patch Tuesday to date, addressing 964 CVEs—104 critical and 860 important—including two zero‑day vulnerabilities exploited in the wild. Defenders must prioritize applying updates to affected components such as .NET, Active Directory services, Azure services, Office, and Windows kernel drivers, and verify system integrity.
Read briefing
CISA Adds CVE‑2026‑88779 to Known Exploited Vulnerabilities Catalog
CISA has added CVE‑2026‑88779, a Citrix NetScaler memory‑buffer overflow that allows attackers to gain full control of exposed assets, to its KEV catalog. Federal agencies must prioritize patching this high‑risk flaw per BOD 26‑04, while all organizations are encouraged to follow the same risk‑based approach. Defenders should verify patch status, monitor for exploitation indicators, and consider submitting unlisted KEVs.
Read briefing
Citrix NetScaler RCE Vulnerability (CVE‑2026‑107406) Requires Immediate Patch
Citrix has disclosed a critical memory‑overflow flaw in NetScaler ADC and Gateway appliances that can be leveraged for remote code execution or denial‑of‑service when configured as a SAML IdP or SP. Affected systems must be upgraded to the latest patched releases without delay. No active exploits reported yet, but defenders should verify patch status and monitor traffic.
Read briefing