
Threat Intel
US Political Campaigns Spend $17M on AI Tools: Security Implications for Defenders
FEC filings reveal that 523 federal campaigns have disclosed $17M in spending on AI vendors such as OpenAI and Anthropic. While many expenses are listed as office costs, the use of these services raises data privacy, policy compliance, and supply‑chain risks. Defenders should audit vendor contracts, enforce usage policies, and monitor API activity to mitigate potential threats.
What Happened
Federal election commission data from 2020‑2025 shows 523 campaigns and committees reporting spending on AI services. At least $17M was disclosed, with OpenAI and Anthropic being the most common vendors.
Impact on Security
AI tools are typically accessed via cloud APIs, exposing campaign data to third‑party providers. Vendor policies (e.g., OpenAI’s prohibition of political content) can be bypassed, creating compliance gaps. The use of these services may also introduce supply‑chain vulnerabilities if the models are not properly vetted.
“More than 70% of Americans would think less of a candidate if they used AI to write a speech.”
What Defenders Should Do
- Review all vendor contracts for AI services and verify that political usage clauses are enforced.
- Implement data‑loss‑prevention controls on any content sent to external AI APIs.
- Monitor API usage logs for anomalous activity or policy violations.
- Educate campaign staff on the risks of sharing sensitive information with AI services.
- Coordinate with legal and compliance teams to ensure adherence to federal election laws and vendor policies.
Key Takeaways
AI adoption is accelerating in political campaigns, but the lack of transparency and potential policy violations create new security challenges. Defenders must proactively manage these risks to protect campaign integrity.
Related articles
US‑China AI Safety Channel Established: Implications for Incident Response
The United States and China have agreed to create a dedicated communication channel for AI‑related incidents, while continuing trade and military dialogue. The agreement aims to prevent escalation of AI mishaps and streamline crisis management between the two powers. Defenders should review cross‑border incident response procedures and update AI‑incident reporting protocols accordingly.
Read briefing
AI Platforms Become New Attack Vectors: Hackers Hijack Claude, ChatGPT and More
As AI tools like Claude, ChatGPT and Grok become integral to daily workflows, threat actors are turning these trusted platforms into launchpads for malware, phishing, and data theft. By weaponizing shareable AI artifacts, exploiting sponsored search results and embedding malicious instructions in seemingly legitimate AI conversations, attackers can deliver ransomware, credential stealers and other payloads with minimal user suspicion. Recent campaigns—FakeAgent’s Claude Artifact redirect to SectopRAT and a fake Apple‑support guide on claude.ai/share that installs the MacSync stealer—show how q
Read briefing
SecOps Briefing: Security Risks of AI Tutoring Platforms for Children
AI tutoring tools are proliferating, but many lack robust security controls. Defenders should audit data flows, enforce strict access controls, and monitor for exfiltration or malicious content. This briefing outlines key vulnerabilities and mitigation steps.
Read briefing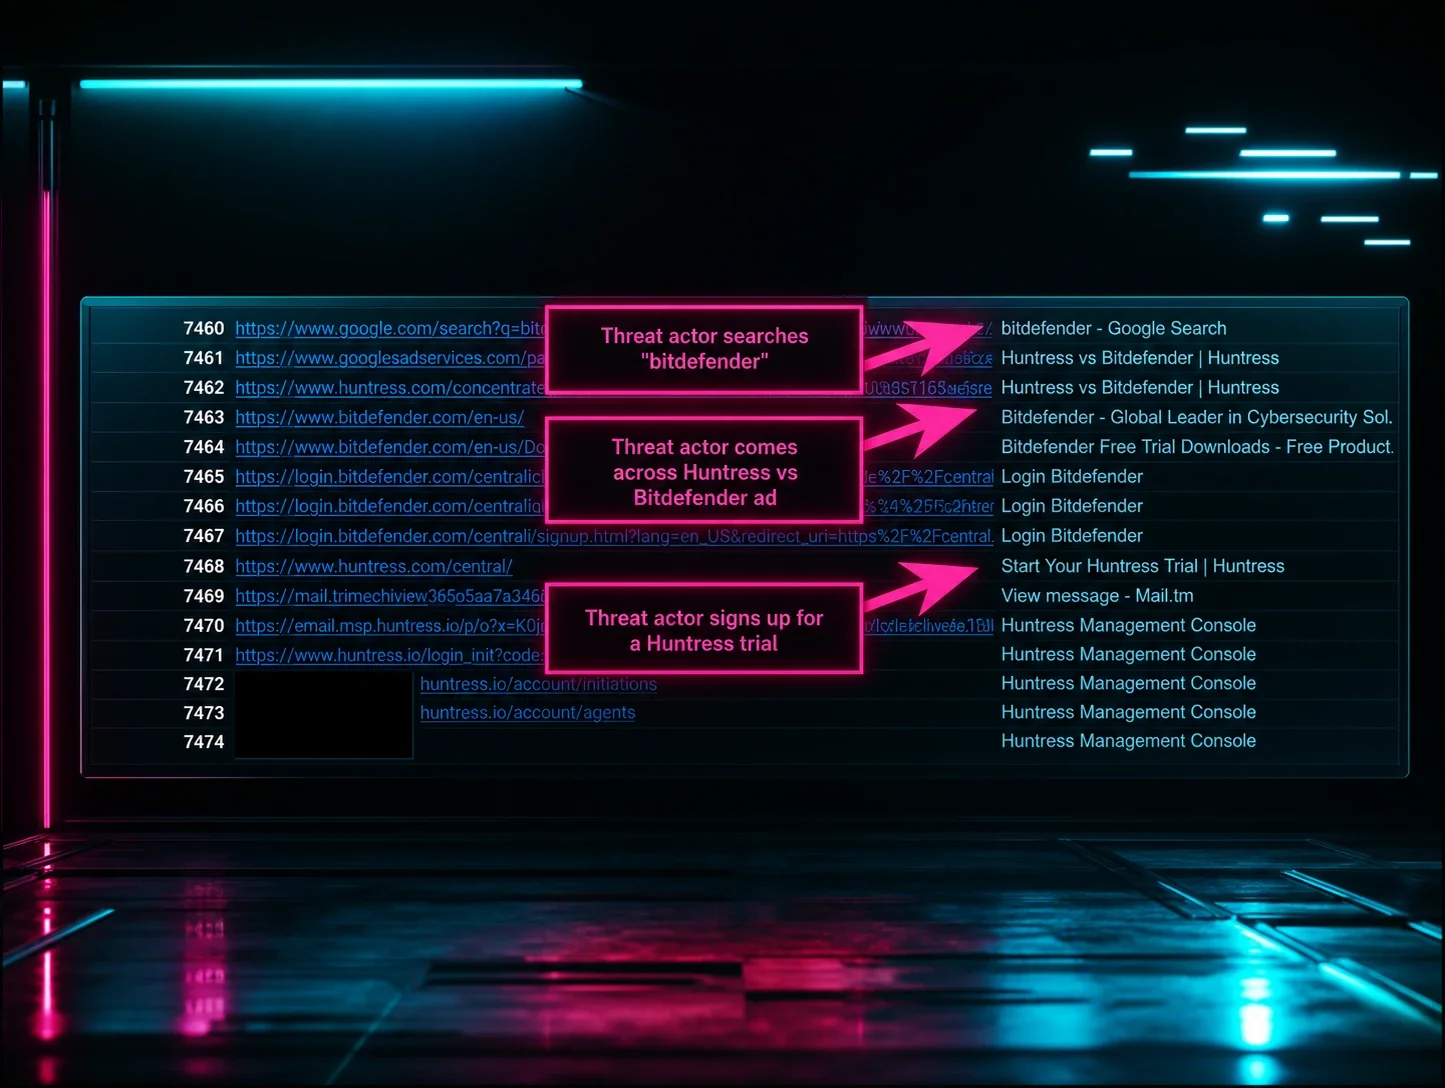
Attacker Installs Huntress Agent, Reveals AI‑Driven Workflow and Targeting Tactics
An adversary installed the Huntress endpoint agent on a compromised host, exposing their use of agentic AI to automate threat hunting, search for tools such as Evilginx, and focus on software‑development firms. Defenders should verify agent integrity, monitor for unauthorized agent installations, and harden target industries.
Read briefing