
Threat Intel
Bomgar RMM Compromise Surge: Immediate Defensive Actions
Huntress SOC reports a spike in attacks targeting Bomgar RMM instances. Defenders should verify patch status, enforce MFA, isolate compromised endpoints, and monitor for lateral movement. Immediate remediation can limit attacker persistence.
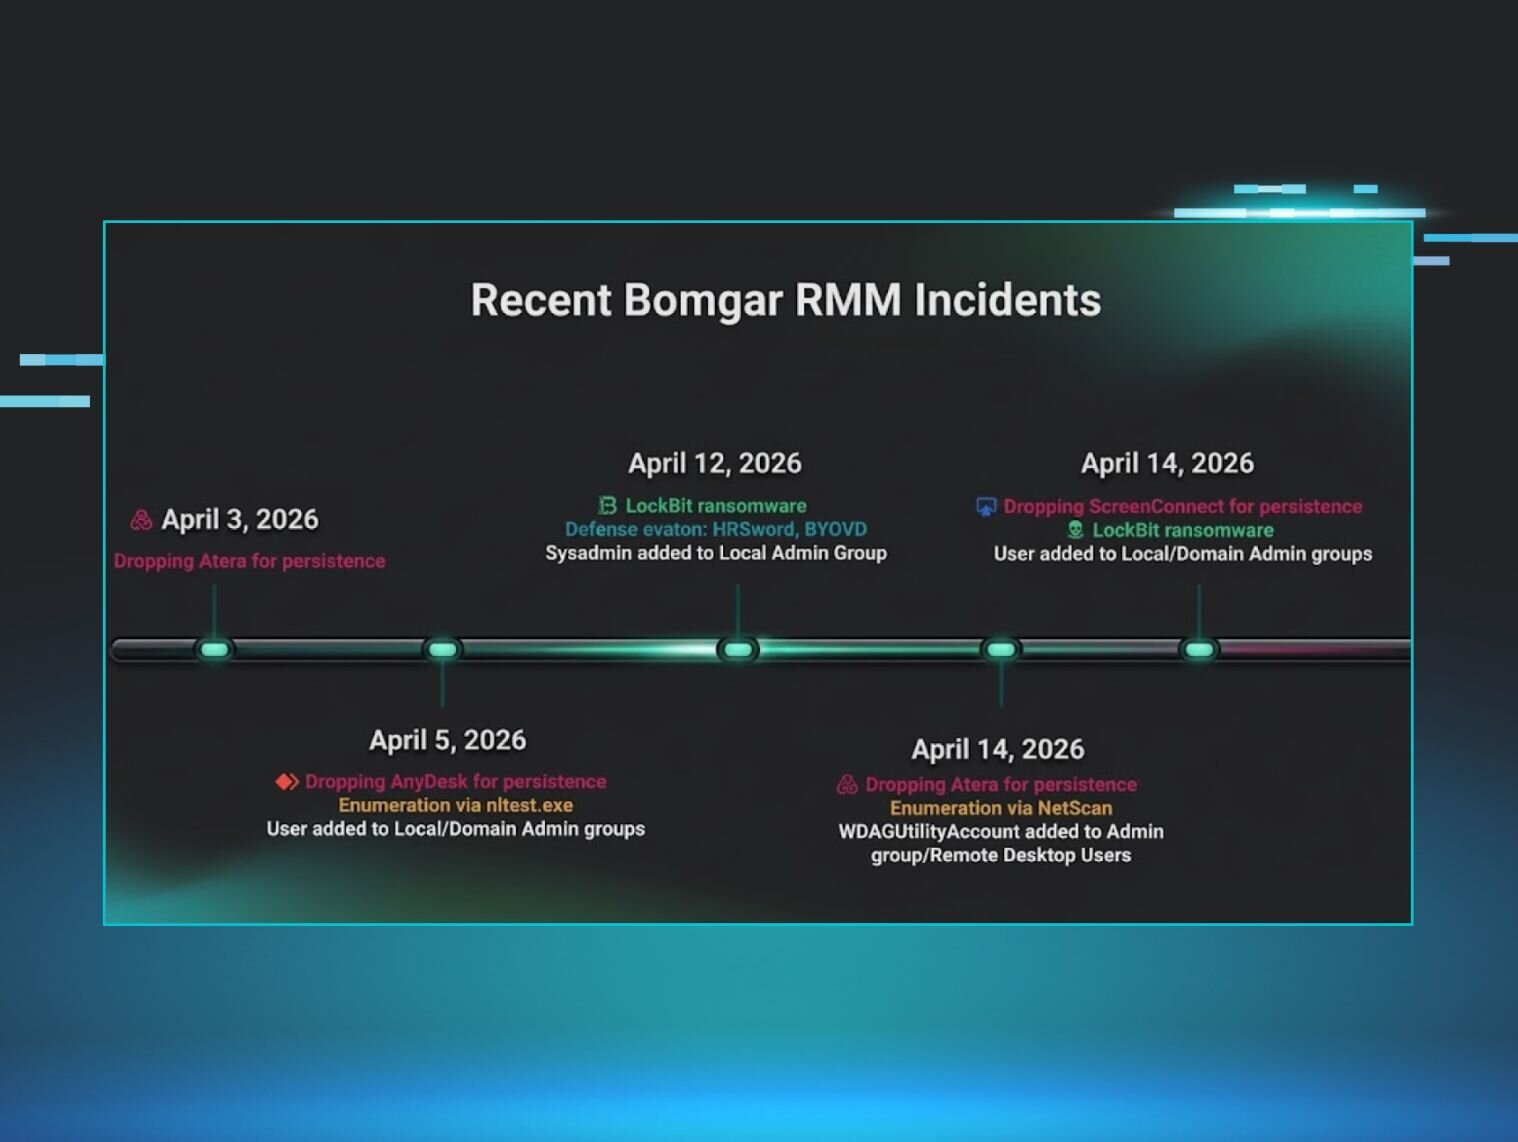
Huntress SOC has observed a recent uptick in incidents where attackers compromise Bomgar Remote Monitoring and Management (RMM) instances. The attacks leverage the RMM’s privileged access to pivot into corporate networks.
What Happened
Multiple organizations reported unauthorized access to Bomgar RMM servers, with attackers using stolen credentials and exploiting known vulnerabilities in older releases.
Impact
Compromised RMM instances grant attackers full control over the host machine, enabling lateral movement, data exfiltration, and persistence. The risk is elevated for environments that rely on Bomgar for remote support or system management.
What to Do
- Verify that all Bomgar RMM servers are running the latest version (currently 2024.3 or newer).
- Enforce multi‑factor authentication for all RMM accounts and disable legacy authentication protocols.
- Isolate any RMM instance that shows anomalous activity and perform a forensic review of logs.
- Restrict network access to RMM servers to a narrow IP range and apply strict firewall rules.
- Implement continuous monitoring for lateral movement indicators such as unexpected SMB traffic or new scheduled tasks.
Prompt remediation and strict access controls are essential to prevent attackers from using RMM as a foothold in your network.
Related vulnerabilities
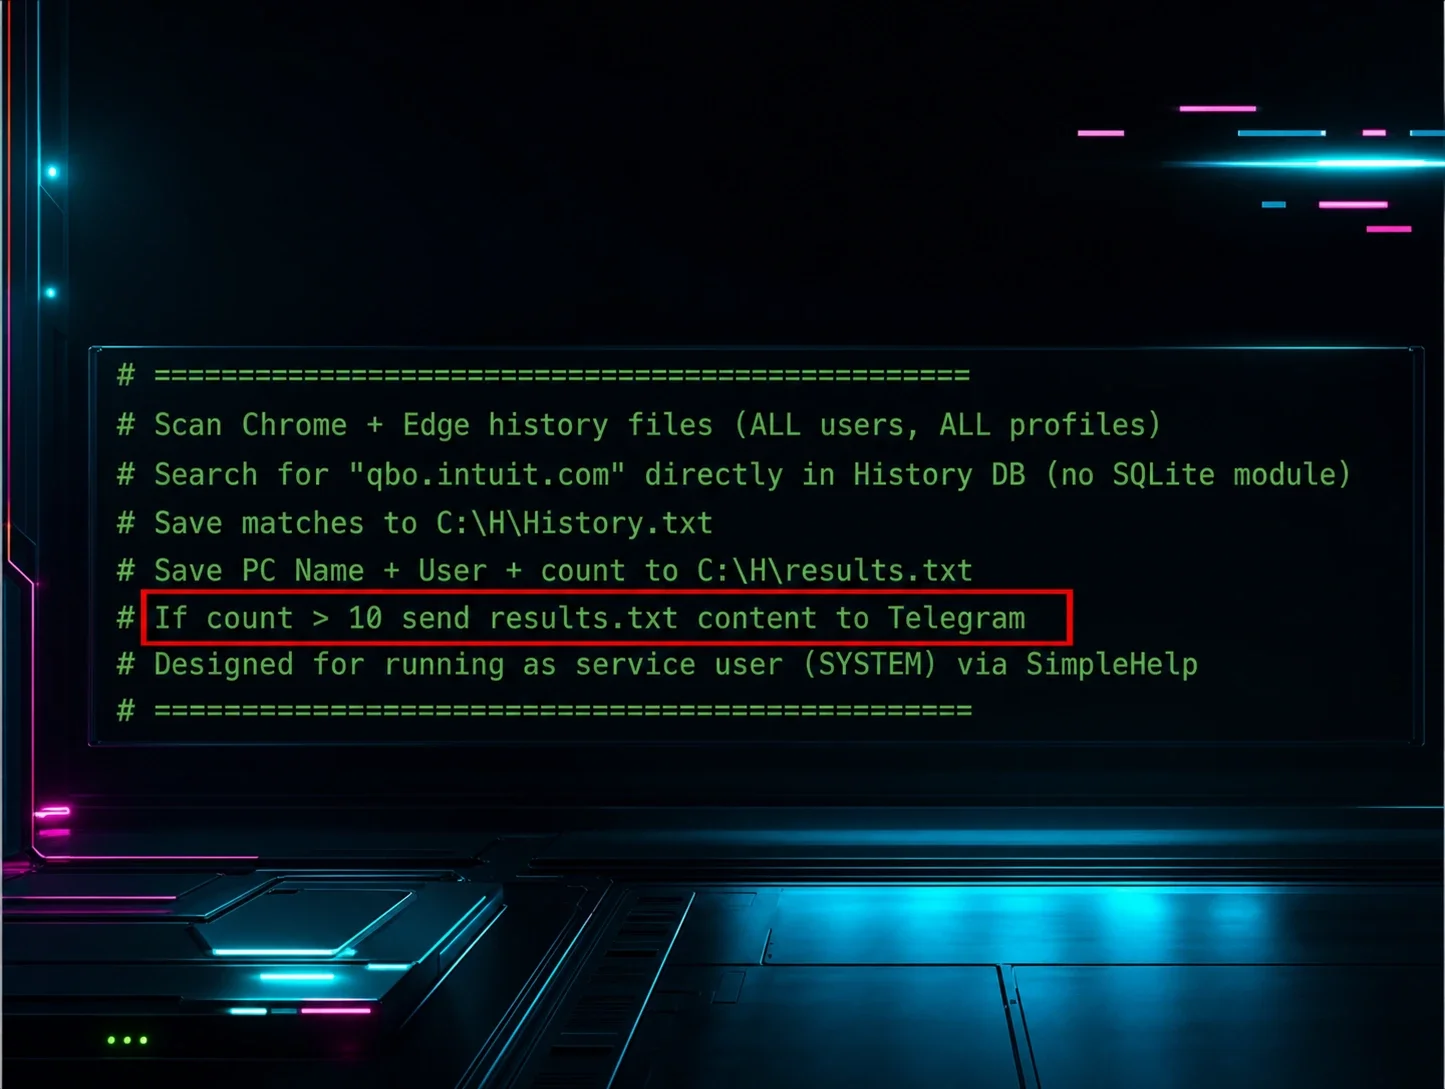
RMM Abuse Surge: Threat Actors Use Daisy‑Chain RMM Tools for Initial Access, Persistence, and Detection Evasion
Cybercriminals are increasingly exploiting remote monitoring and management (RMM) platforms to gain footholds, maintain persistence, and evade detection. Defenders should audit RMM permissions, enforce least‑privilege, monitor for anomalous RMM activity, and segment RMM traffic. Immediate action can prevent lateral movement and data exfiltration.
Read briefing
Mysterious Team Bangladesh: Global Hacktivist Threat Assessment
A new analysis from Group‑IB details the operational footprint of the Mysterious Team Bangladesh, a hacktivist group with worldwide reach. The briefing outlines their tactics, potential targets, and recommended defensive actions for SecOps teams.
Read briefing
Huntress Tragic Quadrant Highlights RMM Abuse, AiTM, and ClickFix as Top Threats for Businesses
The Huntress Tragic Quadrant ranks the most damaging cyber threats to enterprises, spotlighting Remote Management Tool abuse, Account Impersonation via AiTM, and the ClickFix phishing framework. Defenders must prioritize endpoint visibility, email hardening, and user training to counter these tactics. Immediate actions include patching RMM software, tightening MFA, and deploying anti‑phishing solutions.
Read briefing
Azure Portal XSS Spoofing Vulnerability (CVE-2026-83946) – Immediate Patch Required
A cross‑site scripting flaw in Azure Portal allows attackers to spoof the portal interface, potentially tricking users into submitting credentials or executing malicious actions. The vulnerability is exploitable without authentication and can be leveraged to perform phishing or credential theft. Defenders should apply the latest Azure updates and monitor for anomalous portal activity.
Read briefing