
Malware
BUGHATCH Malware: In-Memory PowerShell Implant from CUBA Campaign
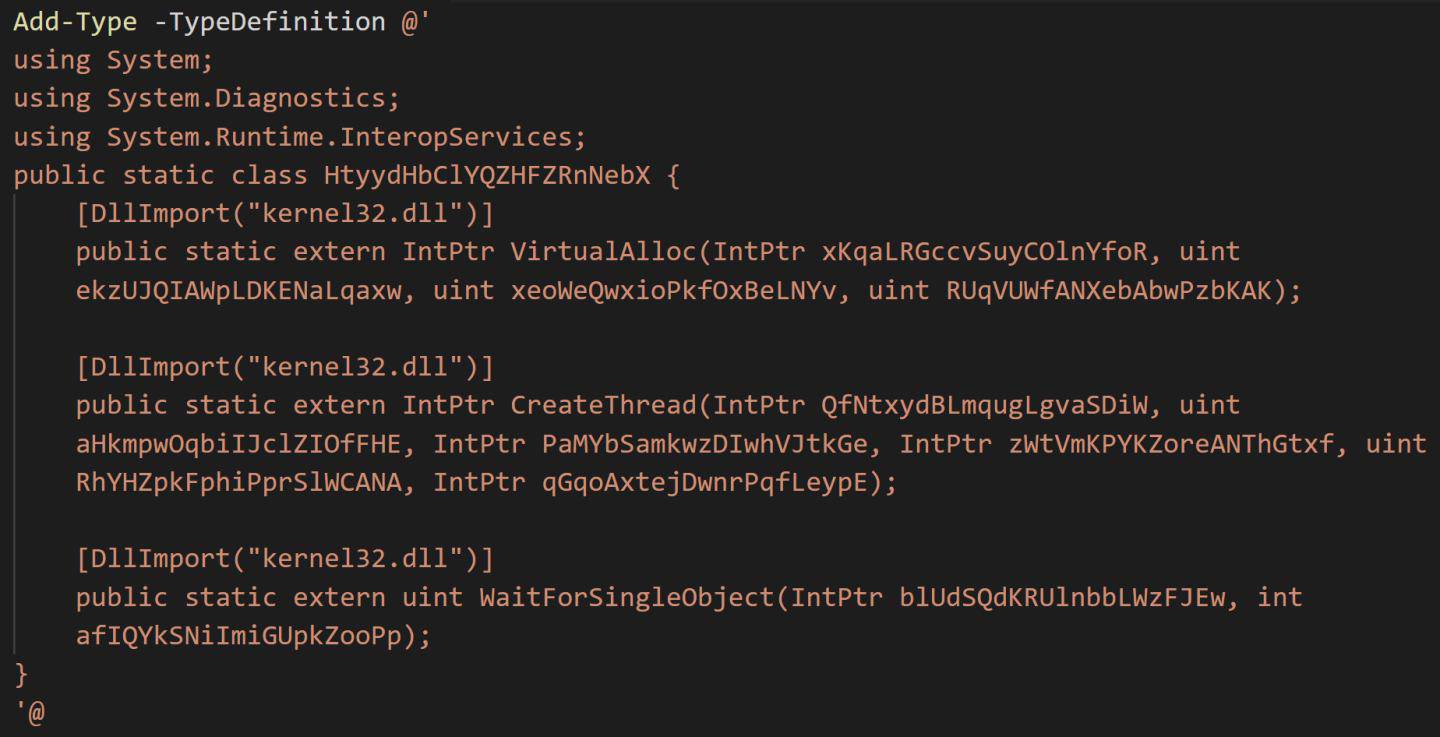
BUGHATCH is a custom C2 implant discovered in February 2022 during the CUBA ransomware operation. The tool is delivered via an obfuscated PowerShell dropper, loads in memory, and can download and execute arbitrary code using reflection, shellcode, or system commands. Defenders should block the dropper, monitor for suspicious download activity, and deploy the provided YARA rule.
What Happened
In early 2022, analysts uncovered BUGHATCH, a lightweight implant used by the threat actor behind the CUBA ransomware campaign. The malware is injected into memory by an obfuscated PowerShell script, which the actor refers to as TERMITE.
Capabilities
- Downloads additional payloads from a command‑and‑control server.
- Executes arbitrary code via reflection, shellcode injection, or direct system commands.
- Maintains in‑memory persistence, avoiding disk artifacts.
Detection & Mitigation
Elastic Security has released a YARA rule that matches the in‑memory dropper signature. Defenders should:
- Block execution of the identified PowerShell script or enforce script‑block policies.
- Monitor outbound HTTP/HTTPS traffic for unexpected download requests from unknown hosts.
- Deploy the YARA rule across endpoint detection platforms and SIEMs.
Additional Resources
Elastic Security Labs publishes the full analysis and YARA rule on their website. The report also maps BUGHATCH actions to MITRE ATT&CK techniques.
Related articles
DYNOWIPER Wiper Attack on Poland’s Energy Infrastructure: What SecOps Need to Know
A coordinated destructive campaign on 29 Dec 2025 deployed the DYNOWIPER wiper against Poland’s renewable energy farms and a major CHP plant, wiping data from Windows systems. Defenders must patch exposed Fortinet devices, enforce MFA, and deploy canary file monitoring to detect and stop the malware.
Read briefing
ClickFix Campaign Compromises Ukrainian Sites, Deploys Psychedelic Stealer via Fake Cloudflare Verification
An active ClickFix campaign has injected fake Cloudflare verification pages into legitimate Ukrainian business sites, tricking visitors into running an MSI installer that delivers the Psychedelic stealer. The malware harvests credentials, cryptocurrency wallet data, and establishes persistence via scheduled tasks. Defenders should block the attacker domains, detect MSI executions, and harden web applications against iframe injection.
Read briefing
Elastic Security Labs Releases NETWIRE Configuration Extractor to Aid Detection
Elastic Security Labs has released a free tool that dynamically extracts encrypted configuration data from the NETWIRE RAT, a malware variant that has risen in prevalence since 2022. The extractor uses YARA and Capstone to locate RC4 keys and decrypt payloads, enabling defenders to expose C2 endpoints and credentials quickly.
Read briefing
RemControl Android Banking Malware Targets European and Canadian Users via Fake IPTV Ads
RemControl, a new Android malware‑as‑a‑service platform, has been delivering banking trojans through fake TVTap IPTV ad sites. The campaign, active since May, targets users in Italy, France, Spain, Poland, Portugal, Canada and the Middle East. Defenders should block known malicious domains, enforce app‑store vetting, and monitor for phishing overlays on Android devices.
Read briefing