
Vulnerabilities
Carbonato Botnet Deploys AI Agents on Exposed Docker Hosts
The Carbonato botnet infects servers with unauthenticated Docker daemons on port 2375, installs the Hermes Agent AI framework, and uses Telegram to exfiltrate AI API keys. Defenders should audit Docker exposure, harden daemon security, monitor for Hermes Agent activity, and revoke compromised keys.
What Happened
ThreatDown researchers uncovered the Carbonato botnet, which targets Docker daemons exposed on port 2375 without authentication. The malware drops the open‑source Hermes Agent AI framework onto the host, then uses a Telegram bot to issue commands and exfiltrate stolen AI API keys.
Impact
Compromised hosts become command‑and‑control nodes that can spread to other reachable Docker services. The botnet harvests credentials for AI services, potentially enabling attackers to generate content, bypass rate limits, or incur charges.
What to Do
- Audit all Docker daemons for unauthenticated access on port 2375 and close the port or enable TLS authentication.
- Check for the Hermes Agent binary or related process names and remove any unauthorized instances.
- Block outbound traffic to Telegram’s API endpoints or enforce strict egress policies for container hosts.
- Revoke any AI API keys that may have been exfiltrated and rotate credentials.
- Apply the latest Docker security patches and follow Docker hardening guidelines.
Related vulnerabilities
ConnectWise Control Remote Support Breach: AI-Driven Attack Exploits Zero‑Day RCE
A sophisticated AI‑driven assault on ConnectWise Control exposed a zero‑day RCE flaw, compromising remote‑support agents and enabling lateral movement. The breach underscores the need for immediate patching, segmentation, and MFA enforcement.
Read briefing
CrowdStrike Deploys On‑Device AI for Real‑Time Data Classification in Falcon Data Security
CrowdStrike, in partnership with Intel, has unveiled a next‑generation feature for Falcon Data Security that leverages on‑device language models running on dedicated AI hardware. The new capability instantly tags and classifies sensitive information—such as PII, PHI, and financial data—directly on endpoints, eliminating the need to ship raw data to the cloud. This reduces latency, preserves privacy, and tightens compliance controls while maintaining the same high detection accuracy that Falcon is known for. The move underscores CrowdStrike’s commitment to edge‑AI security and sets a new standa
Read briefing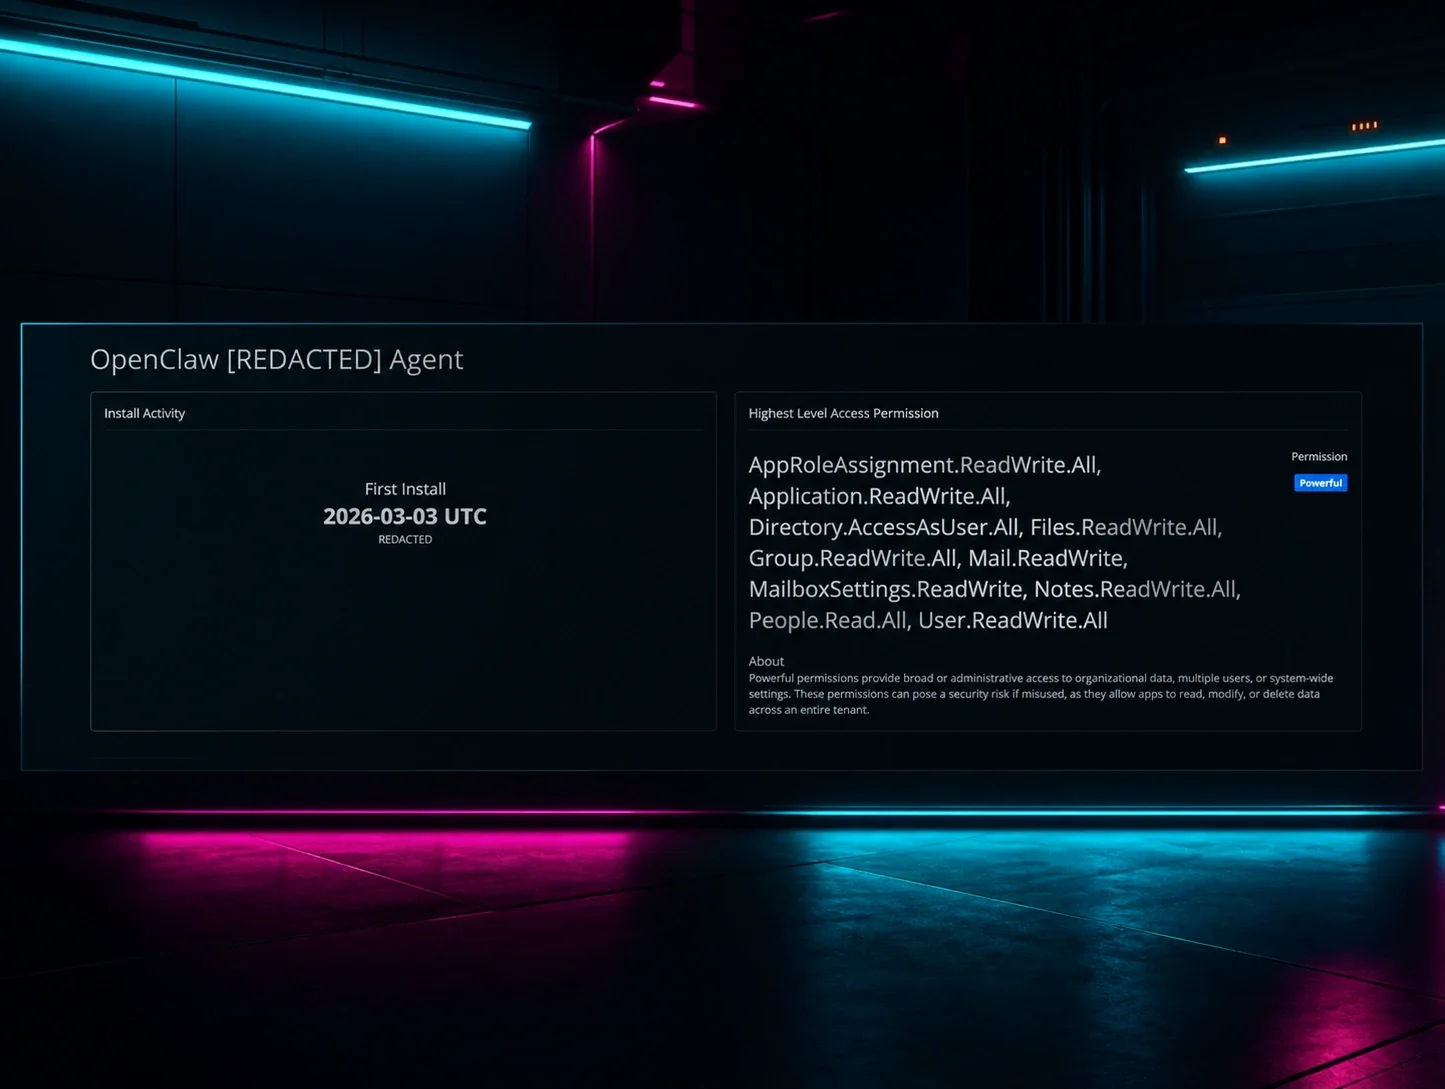
OpenClaw AI Agents Pose Identity and Data Risks with Broad Cloud Permissions
OpenClaw AI agents that are granted wide cloud permissions can expose user identities and sensitive data to attackers. The risk is high for any organization deploying these agents without proper access controls. Defenders should audit permissions, enforce least privilege, and monitor for anomalous activity.
Read briefing
CVE-2026-54128: Windows DHCP Client Remote Code Execution Vulnerability
Microsoft has identified a remote code execution flaw in the Windows DHCP client that can be triggered by malicious DHCP servers. The vulnerability allows attackers to run arbitrary code on affected hosts. Defenders should verify patch status, monitor DHCP traffic, and apply mitigations.
Read briefing