
Vulnerabilities
CISA Adds WordPress Remote File Inclusion CVE-2026-87902 to KEV Catalog
CISA has added CVE-2026-87902, a WordPress Core Remote File Inclusion flaw, to its Known Exploited Vulnerabilities catalog after confirmed active exploitation. Federal agencies must prioritize patching, and all organizations should treat the vulnerability as high risk and follow remediation guidance.
What Happened
CISA has added CVE-2026-87902, a WordPress Core Remote File Inclusion flaw, to its Known Exploited Vulnerabilities catalog after confirmed active exploitation.
Impact
The vulnerability allows attackers to execute arbitrary code on any publicly exposed WordPress site, including federal agencies that run the platform. A successful exploit grants full control of the affected server.
Remediation
- Apply the latest WordPress core patch immediately.
- Verify that the patch is in effect by checking the WordPress version number.
- Audit exposed assets for signs of compromise before and after patching.
- Implement network segmentation and web application firewall rules to block remote file inclusion attempts.
Policy Context
Federal Civilian Executive Branch agencies must follow BOD 26‑04, which prioritizes rapid remediation of KEV catalog vulnerabilities on publicly exposed assets. The directive also requires agencies to confirm whether a system was compromised before applying a patch.
Next Steps
All organizations should treat CVE-2026-87902 as a high‑risk vulnerability and follow the mitigation guidance. If you discover an exploited vulnerability not yet listed in the KEV catalog, submit it via the CISA KEV Nomination Form.
Related vulnerabilities
WordPress CVE-2026-87902 Exploitation: Attackers Writing Malicious Files to Disk
WordPress sites vulnerable to CVE‑2026‑87902 are now being exploited to write arbitrary files that execute shell commands. The flaw, a path‑traversal bug in get_page_template(), allows unauthenticated attackers to achieve remote code execution under specific conditions. Defenders should patch to 7.1.2 or later, verify file integrity, and monitor for suspicious file writes.
Read briefing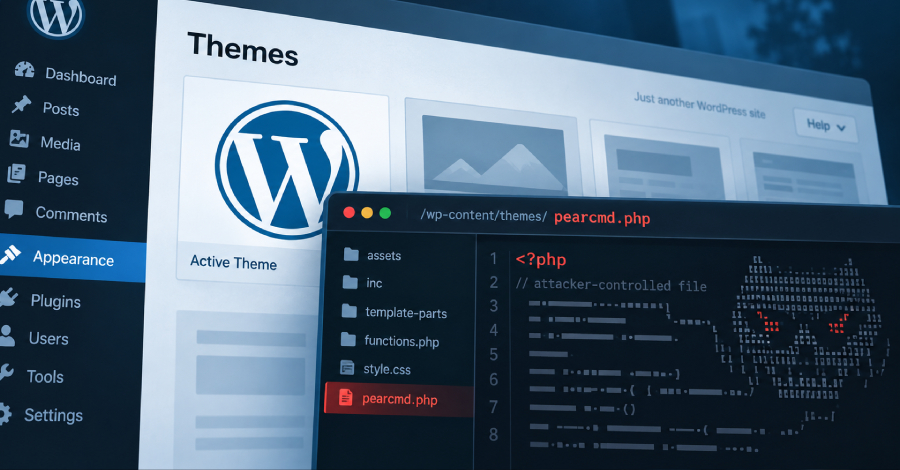
Active Exploitation of Critical WordPress RCE Vulnerability CVE-2026-87902
Threat actors are actively exploiting a critical 9.2-rated remote code execution vulnerability in WordPress, tracked as CVE-2026-87902, shortly after public disclosure. Unauthenticated attackers leverage insecure page-template resolution via get_page_template() to include local PHP files such as pearcmd.php, provided specific directory and file prerequisites are met. Defenders must audit theme configurations, apply official updates, and monitor for unauthorized file writes.
Read briefing
Critical WordPress Path Traversal Vulnerability (CVE-2026-87902) Under Active Exploitation
A critical path traversal vulnerability in WordPress, tracked as CVE-2026-87902 with a CVSS score of 9.2, is being actively exploited in the wild shortly after disclosure. Unauthenticated attackers can leverage this flaw for remote code execution under specific server and theme conditions. SecOps and sysadmins must immediately audit active themes and apply official patches.
Read briefing
CISA Adds CVE-2026-21589 to Known Exploited Vulnerabilities Catalog
CISA has added CVE-2026-21589, a file and directory disclosure flaw in multiple Atlassian products, to its Known Exploited Vulnerabilities catalog. Federal agencies must prioritize patching and verify that exposed assets are not compromised. All organizations should adopt risk‑based remediation for KEV entries.
Read briefing