
Threat Intel
Cobalt Gang 2019 Phishing Campaign Targeting Global Financial Institutions
In 2019, the Cobalt Gang executed a sophisticated phishing operation aimed at financial institutions worldwide. The campaign leveraged spear‑phishing emails with malicious attachments to gain initial access. Defenders should review email filtering rules, enforce MFA, and conduct targeted user training.
What Happened
The Cobalt Gang, a known threat actor, launched a phishing campaign in 2019 that targeted financial institutions across the globe. Attackers sent spear‑phishing emails containing malicious attachments designed to bypass email security and deliver malware into corporate networks.
Impact
Victims experienced initial credential compromise, lateral movement within banking networks, and in some cases, exfiltration of sensitive financial data. The campaign highlighted the persistent risk to the banking sector from targeted phishing.
Mitigation Steps
- Enforce strict email attachment filtering and sandboxing for unknown senders.
- Deploy and enforce multi‑factor authentication for all remote access and privileged accounts.
- Conduct regular phishing awareness training focused on spear‑phishing indicators.
- Implement endpoint detection and response (EDR) to detect malicious attachment execution.
- Maintain up‑to‑date threat intelligence feeds to recognize known Cobalt Gang indicators.
Detection Tips
Look for anomalous outbound traffic from compromised endpoints, especially to known Cobalt Gang infrastructure, and monitor for execution of suspicious Office macros or scripts.
Related articles
Industrialized MaaS Drives Fake Coretax App Fraud in Indonesia
During Indonesia’s tax season, attackers pushed a counterfeit Coretax mobile application using a shared malware‑as‑a‑service platform. The infrastructure enables rapid brand abuse and phishing, targeting taxpayers and financial institutions. Defenders should block known malicious domains, monitor for Coretax app impersonations, and harden endpoint detection.
Read briefing
Mexican PhaaS Operation Targets 20+ Banks with Real‑Time Phishing, AI Vishing, and Mobile RAT
A Mexican PhaaS campaign has been uncovered that delivers real‑time phishing, AI‑driven vishing, and a mobile RAT to more than twenty financial institutions. Defenders should immediately review email and voice traffic, enforce MFA, and deploy endpoint detection for mobile devices.
Read briefing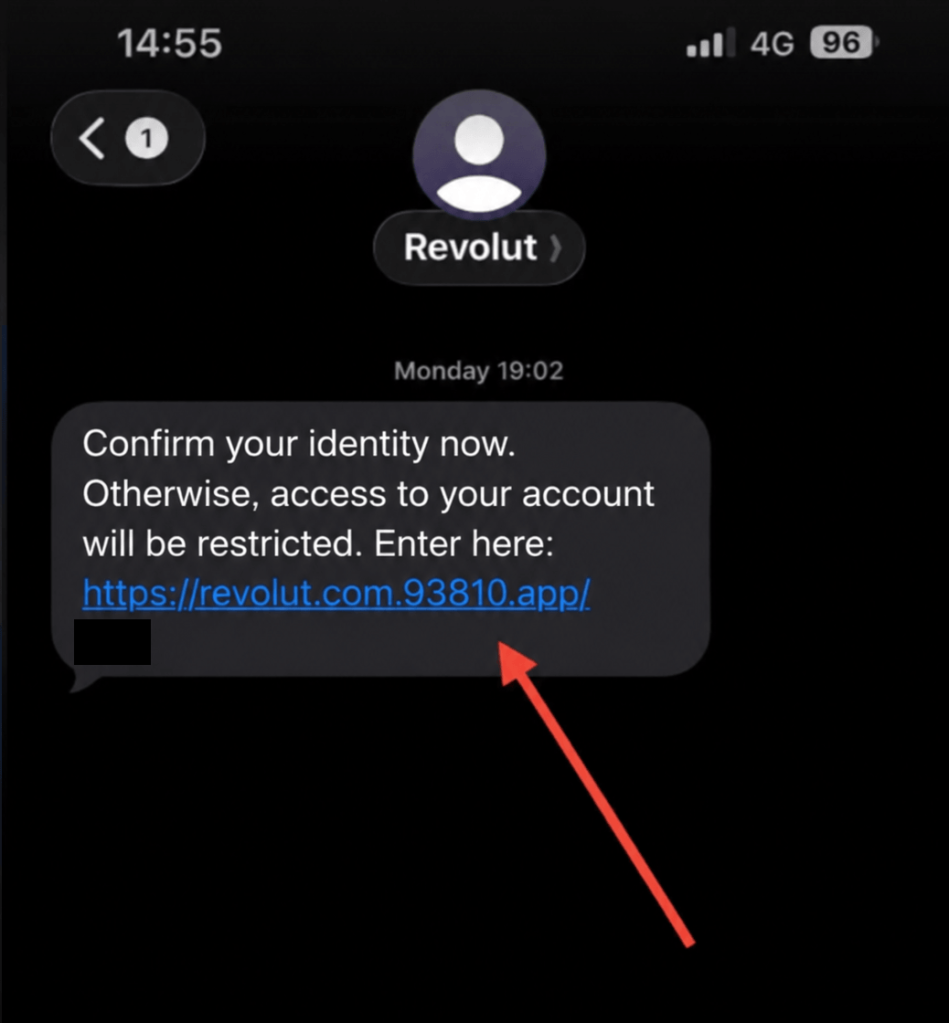
Revolut Customers Targeted by Phishing Texts After Data Breach
Revolut customers received suspicious SMS messages that appeared to come from the bank days after a breach that exposed personal and financial data. The phishing campaign mimics official alerts, requests camera access, and requests passwords, potentially enabling account takeover. Defenders should verify messages, block malicious domains, and enforce two‑factor authentication.
Read briefing
Saudi Manpower Provider Scam: 1,001 Fake Domains Identified by Group‑IB
Group‑IB uncovered 1,001 domains used in a phishing campaign that impersonated a Saudi manpower provider, targeting users in KSA. Defenders should block these domains, update filtering rules, monitor for new registrations, and educate users to mitigate credential theft and potential malware delivery.
Read briefing