
Threat Intel
Mexican PhaaS Operation Targets 20+ Banks with Real‑Time Phishing, AI Vishing, and Mobile RAT
A Mexican PhaaS campaign has been uncovered that delivers real‑time phishing, AI‑driven vishing, and a mobile RAT to more than twenty financial institutions. Defenders should immediately review email and voice traffic, enforce MFA, and deploy endpoint detection for mobile devices.
What happened
Group‑IB exposed a Mexican PhaaS operation that has been targeting over twenty banks. The service delivers real‑time phishing emails, AI‑powered vishing calls, and a remote access trojan (RAT) designed for mobile devices.
Impact
More than 20 financial institutions in Mexico are exposed to credential theft, phone‑based social engineering, and potential remote compromise of mobile endpoints. The campaign’s real‑time nature allows attackers to adapt quickly to victim responses.
What defenders should do
- Enable and enforce multi‑factor authentication across all user accounts.
- Deploy advanced email protection that detects phishing in real time and blocks malicious attachments or links.
- Implement voice‑call monitoring or caller‑ID verification to detect vishing attempts.
- Use mobile endpoint detection and response (EDR) to detect and isolate RAT activity.
- Conduct regular phishing awareness training focused on recognizing AI‑generated content.
Mitigation guidance
Defenders should treat this PhaaS as a persistent threat actor offering a full service. Continuous monitoring, rapid incident response, and cross‑team collaboration are essential to contain and remediate the attacks.
Related articles
UNC6671’s BlackFile Vishing Campaign Targets Microsoft 365 & Okta – Defenders’ Response
In early 2026, UNC6671 launched a vishing‑based extortion operation, leveraging adversary‑in‑the‑middle techniques to compromise SSO and bypass MFA on Microsoft 365 and Okta. The group uses Python and PowerShell scripts to exfiltrate data before demanding ransom. Defenders should monitor voice‑phishing indicators, enforce MFA, and scrutinize SSO logs for anomalous activity.
Read briefing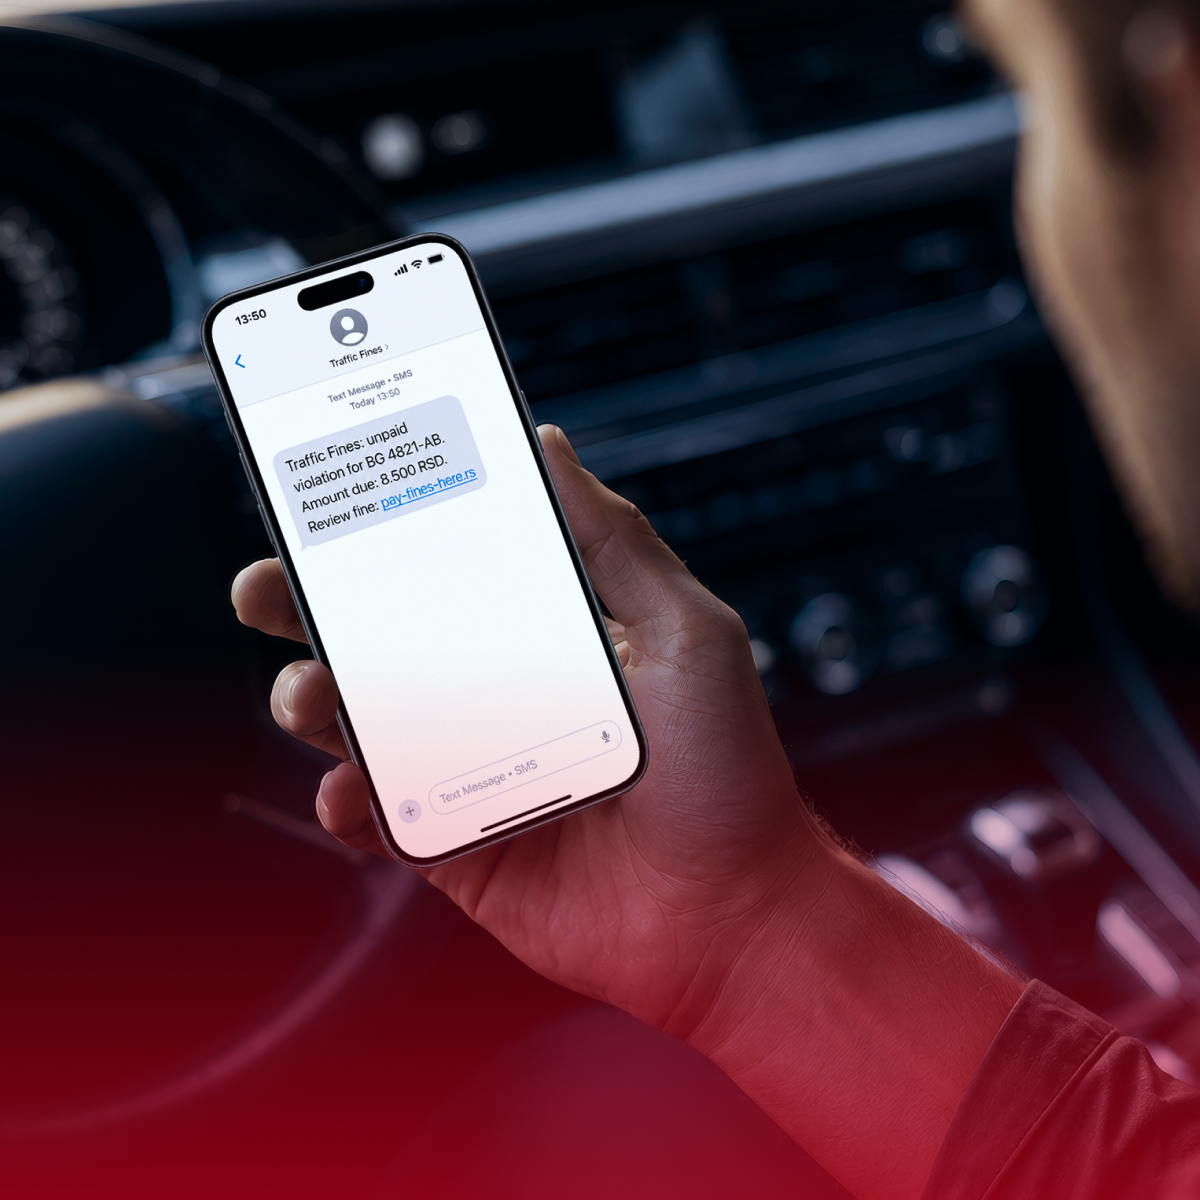
SMS Phishing Targeting Serbian Road Users via Fake State Authority – Global Threat
An SMS phishing operation impersonating Serbia’s state road authority has been linked to the Darcula and Phoenix PhaaS platforms, affecting motorists in Serbia and other countries. The campaign uses spoofed numbers and fake traffic fines to lure victims into revealing credentials. Defenders should verify SMS authenticity, block spoofed numbers, and monitor for related phishing indicators.
Read briefing
Group‑IB Launches Unified Fraud Protection Platform for Digital Identity Security
Group‑IB has introduced a comprehensive Fraud Protection platform that consolidates threat intelligence, XDR, and email protection into a single solution. The platform targets organizations seeking to safeguard digital identities against fraud, phishing, and brand abuse. Defenders should evaluate integration options and enable real‑time monitoring to strengthen their security posture.
Read briefing
Hirudo Android Malware Hijacks Banking Apps to Steal Credentials
Hirudo is an Android malware that replaces legitimate banking apps with malicious copies, disabling security checks to harvest credentials and remotely control devices. It targets banks in Indonesia, China, India, Mexico, Morocco, and Thailand, and is delivered via apps that masquerade as shopping or entertainment services. Defenders should verify app signatures, enforce Play Integrity, restrict Accessibility permissions, and deploy mobile security solutions to detect hooking engines.
Read briefing