
Threat Intel
SMS Phishing Targeting Serbian Road Users via Fake State Authority – Global Threat
An SMS phishing operation impersonating Serbia’s state road authority has been linked to the Darcula and Phoenix PhaaS platforms, affecting motorists in Serbia and other countries. The campaign uses spoofed numbers and fake traffic fines to lure victims into revealing credentials. Defenders should verify SMS authenticity, block spoofed numbers, and monitor for related phishing indicators.
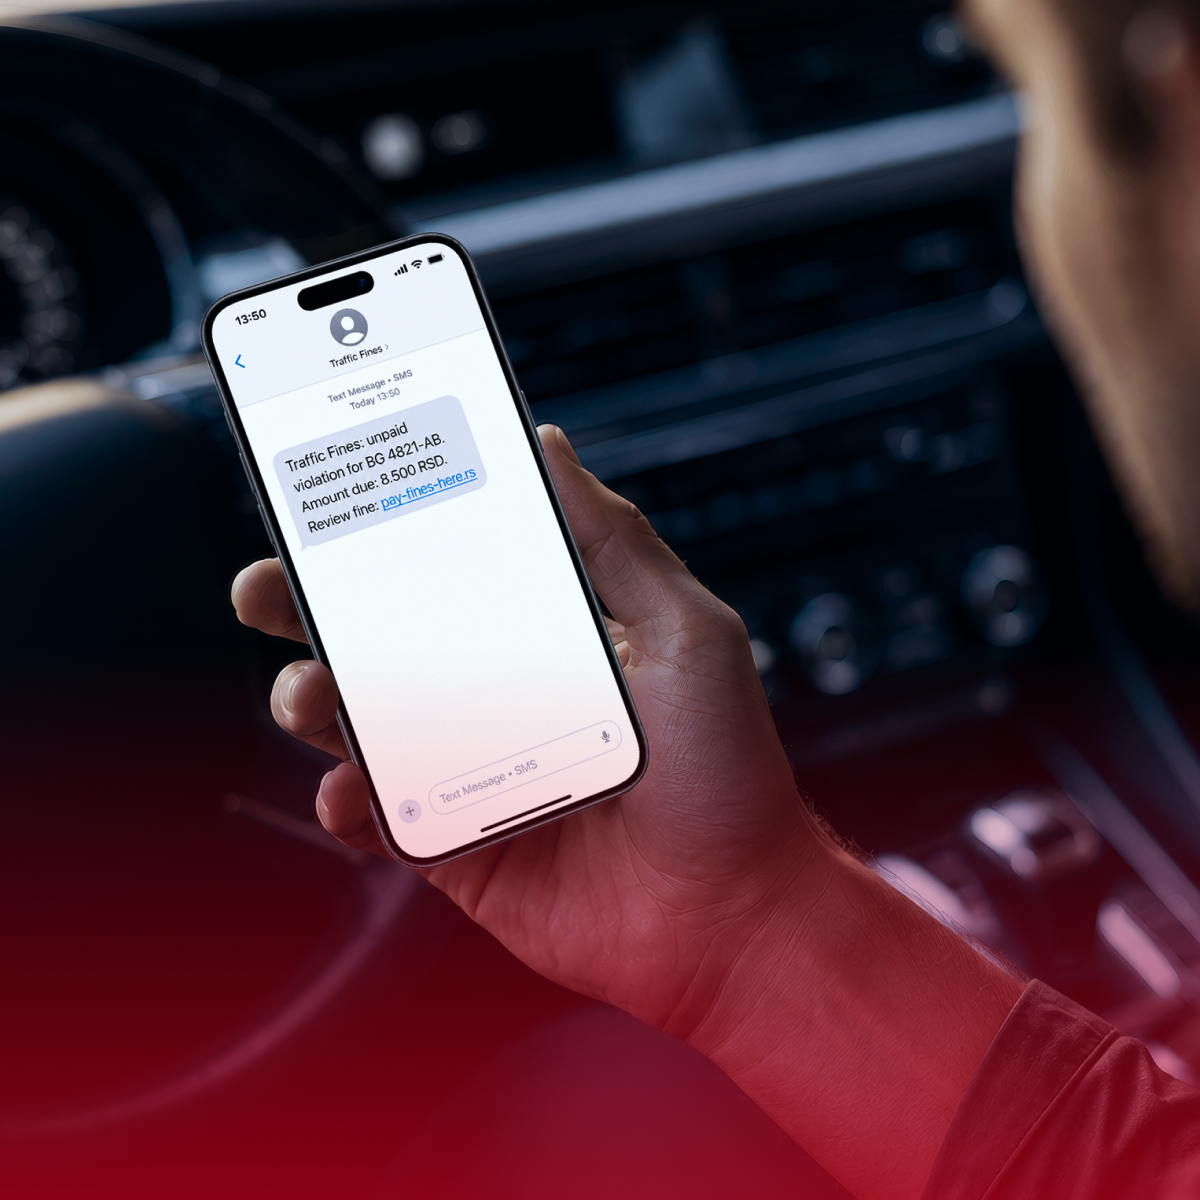
SMS phishing operation impersonating Serbia’s state road authority has targeted motorists with fake traffic fines.
What Happened
Attackers sent spoofed SMS messages that appear to come from the official road authority, offering a link to pay alleged fines. The link leads to a phishing site that harvests credentials.
Impact
- Serbian motorists receiving the messages.
- Potential credential compromise for victims worldwide.
- Campaign linked to the Darcula and Phoenix PhaaS platforms.
What Defenders Should Do
- Verify SMS authenticity: check sender ID against known official numbers.
- Block known spoofed numbers and domains used by the campaign.
- Educate users about fake traffic fine messages and encourage reporting.
- Monitor logs for traffic to the identified phishing domains.
- Implement multi‑factor authentication for critical accounts.
Mitigation Resources
Use Group‑IB’s Unified Risk Platform to detect and block similar phishing attempts across SMS and web channels.
Related articles
Saudi Manpower Provider Scam: 1,001 Fake Domains Identified by Group‑IB
Group‑IB uncovered 1,001 domains used in a phishing campaign that impersonated a Saudi manpower provider, targeting users in KSA. Defenders should block these domains, update filtering rules, monitor for new registrations, and educate users to mitigate credential theft and potential malware delivery.
Read briefing
Industrialized MaaS Drives Fake Coretax App Fraud in Indonesia
During Indonesia’s tax season, attackers pushed a counterfeit Coretax mobile application using a shared malware‑as‑a‑service platform. The infrastructure enables rapid brand abuse and phishing, targeting taxpayers and financial institutions. Defenders should block known malicious domains, monitor for Coretax app impersonations, and harden endpoint detection.
Read briefing
Fake Celine Dion Ticket Scam Targets Fans via Social Media and Impersonating Sites
Group‑IB uncovered a multi‑layered phishing scheme selling counterfeit Celine Dion concert tickets. The attack uses social‑network messages and spoofed distributor sites to lure buyers. Defenders should block malicious domains, monitor for ticket‑related phishing, and educate users.
Read briefing
Corp MDM Android Spyware Targets Logistics Sector via Fake Google Play Pages
A targeted campaign is distributing Android spyware known as Corp MDM via fraudulent Google Play landing pages impersonating logistics brands. The malware, packaged as a system service, is designed to intercept inbound SMS traffic, manipulate call routing, and maintain persistent background execution using a hard-coded command-and-control infrastructure.
Read briefing