
Threat Intel
CTM360 Report Highlights ClickFix as Leading Initial-Access Technique Using Malicious Copy-Paste
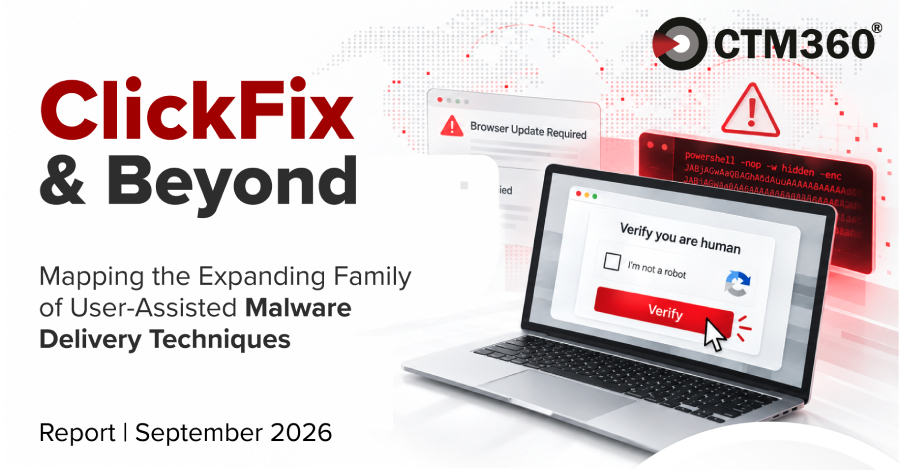
Recent threat intelligence from CTM360 analyzes over 17,000 URLs utilizing the ClickFix social engineering technique, which bypasses traditional security controls through manual user execution. Accounting for nearly half of Microsoft Defender Experts initial-access cases in 2025, the method relies on fake error prompts and clipboard manipulation rather than software exploits.
What Happened
Research published by CTM360 details the evolution of ClickFix from a novel tactic in late 2023 into a subscription-based cybercrime product featuring on-chain infrastructure. Attackers compromise legitimate or newly registered websites to display fabricated system errors, such as failed browser rendering, storage warnings, or bogus human verification checks. The interface instructs the user to apply a provided remedy by copying a script, opening a native administrative console (such as PowerShell or Terminal), and pasting the payload.
Because the command is executed directly by an authenticated user inside a legitimate, signed system binary, the activity evades standard file-based detection mechanisms, vulnerability scanners, and email gateway filters. Telemetry highlights the rapid scale of adoption: Microsoft attributed 47% of its managed initial-access cases to ClickFix in 2025, and ESET observed sustained multi-hundred percent growth across consecutive reporting periods.
Impact and Scope
- Platforms Affected: Windows, macOS, and Linux systems.
- Attack Vector: Social engineering via copy-and-paste command execution (tracked by MITRE as T1204.004).
- Infrastructure: Distributed across over 17,000 analyzed URLs, utilizing blockchain-based contracts to dynamically rotate lure hosts and evade domain-blocklists.
- Risk Profile: Leaves no file on disk during the initial vector and utilizes legitimate administrative binaries, generating minimal behavioral noise for standard EDR rules that rely solely on file reputation.
What Defenders Should Do
Traditional domain blocking and standard attachment analysis are insufficient to mitigate ClickFix campaigns due to rapid infrastructure rotation and the lack of payload downloads. SecOps and sysadmins should implement targeted detection and prevention measures:
- Deploy endpoint detection rules to alert on suspicious clipboard write operations immediately preceding the invocation of shells like PowerShell, CMD, or Terminal.
- Monitor for anomalous interactive command-line executions involving encoded strings, web requests (Invoke-WebRequest, curl), or execution from user profile temp directories.
- Restrict or audit the use of administrative shells via AppLocker, Software Restriction Policies, or endpoint privilege management to limit unauthorized script execution.
- Conduct focused security awareness training targeting modern social engineering tactics, specifically instructing users never to copy and paste troubleshooting commands into system prompts based on web browser instructions.
Related articles
ClickFix Attacks: User-Executed Malicious Commands
ClickFix attacks rely on deceiving users into executing malicious commands, often via copy-pasted instructions. Defenders should focus on user awareness training and implement browser/endpoint security controls to prevent command execution. CrowdStrike Falcon offers layered protection against this technique.
Read briefing
ClickFix Social Engineering: Defend Against User-Pasted Command Execution
CrowdStrike published guidance on ClickFix attacks, in which victims are persuaded to copy and run malicious commands in their own shells or browsers. The technique targets employees, contractors, and any user with terminal or browser access. Defenders should treat user-initiated command execution as a high-risk indicator and combine browser controls, endpoint detection, identity monitoring, and SOC triage.
Read briefing
Microsoft KB5002914 Patch Breaks Excel Copy‑Paste, Silent Failure – Workaround Available
Microsoft’s September 2026 KB5002914 security update has introduced a silent copy‑paste defect in Excel for the 2024, 2021, 2019 and 2016 families. Users report that the source remains highlighted while the destination stays unchanged, with no error message. Microsoft has confirmed the issue and is investigating a fix. As a stop‑gap, uninstalling the KB via command‑line restores normal functionality. The update also addressed several remote‑code‑execution and information‑disclosure flaws in the same Patch Tuesday release.
Read briefing
LLM Safety Classifier Evasion Exploited: What SecOps Must Know
CrowdStrike’s Cyber Superintelligence Lab discovered that the leading publicly available content safety classifiers can be bypassed through a request‑aggregate‑bypass technique. The attack allows malicious actors to inject disallowed content into LLM outputs, undermining automated moderation. Defenders should augment LLM pipelines with layered filtering, monitor for anomalous request patterns, and enforce strict content‑policy enforcement.
Read briefing