
Threat Intel
CyberXero AI‑Powered Campaign Compromises 628,000 Ukrainian Records via WordPress Exploits
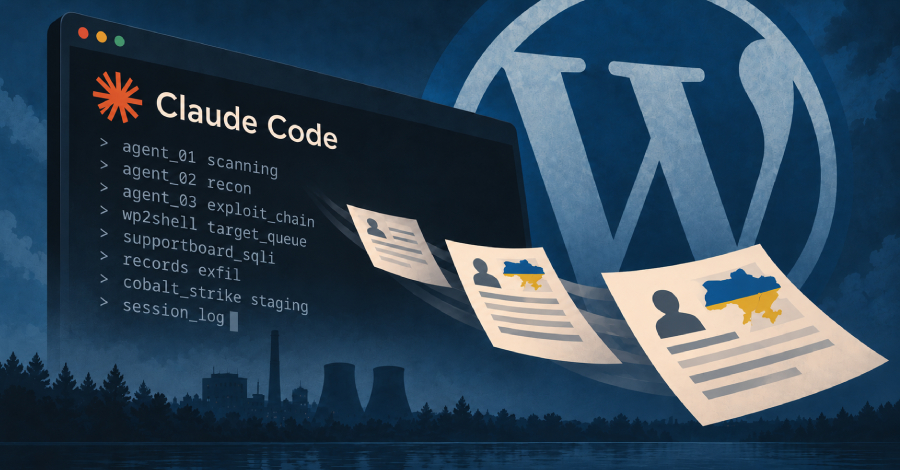
CyberXero, a Russian‑speaking threat actor, used Anthropic’s Claude Code to orchestrate an AI‑augmented attack that leveraged WordPress vulnerabilities (CVE‑2026‑63030, CVE‑2026‑60137, CVE‑2026‑4815) and Cobalt Strike to compromise 429 admin panels and exfiltrate 628,000 records from Ukrainian organizations. The campaign also targeted critical infrastructure in Ukraine and other countries. Defenders should patch the CVEs, monitor for unauthorized admin activity, and inspect exposed directories for AI logs and stolen data.
What Happened
CyberXero, a Russian‑speaking initial‑access broker, launched a dual‑pipeline campaign in October 2026. The operation combined commodity tools such as Cobalt Strike with an AI orchestration layer powered by Anthropic’s Claude Code to automate exploitation of known WordPress flaws and to conduct manual attacks on Ukrainian energy and critical‑infrastructure assets.
Impact
The automated pipeline scanned 4,708 WordPress sites, successfully gaining control of 429 admin panels. From four Ukrainian organizations, the attackers exfiltrated more than 628,000 records tied to individuals. Confirmed compromises also appear in Poland, China, and the Netherlands.
Exfiltration was confirmed through a leaked open directory (46.21.250.135) that exposed AI session logs, plaintext tokens, exploitation toolkits, and victim data.
Technical Details
- Targeted WordPress CVEs: CVE‑2026‑63030 (wp2shell), CVE‑2026‑60137 (wp2shell), CVE‑2026‑4815 (Support Board SQL injection)
- Tools: Cobalt Strike, custom scripts, AI agent configurations
- Campaign phases: global automated WordPress/e‑commerce attack; curated manual attacks on Ukrainian utilities, including a heating provider in Kharkiv
What to Do
- Patch all WordPress installations against CVE‑2026‑63030, CVE‑2026‑60137, and CVE‑2026‑4815 immediately.
- Audit admin access logs for unauthorized logins and anomalous activity.
- Search for exposed directories or files that may contain AI session logs or stolen data.
- Implement network segmentation and restrict outbound traffic from critical‑infrastructure systems.
- Maintain an inventory of critical assets and monitor for signs of targeted reconnaissance.
Related vulnerabilities
CVE‑2026‑108455: PowerPoint Information Disclosure – Update Omission Clarified
Microsoft Office PowerPoint’s information disclosure vulnerability (CVE‑2026‑108455) was fixed in the October 2026 security update, but the CVE was omitted from the advisory list. Defenders should verify the update is installed; no further action is required if already updated.
Read briefing
Critical Cisco Hardening Release: ASA, FTD, FMC Patch Internal Exploits
Cisco’s security team has rolled out a hardening update for its Secure Firewall Adaptive Security Appliance, Threat Defense, and Management Center software, addressing a suite of internally discovered flaws. Eight CVEs (CVE‑2026‑20329 through CVE‑2026‑20336) cover issues ranging from static credential exposure to authentication bypass, with two vulnerabilities already being actively exploited. No workarounds exist; customers must install the patches promptly to mitigate the critical risk.
Read briefing
Critical Apache Zookeeper Vulnerabilities Threaten Data Integrity & Confidentiality – Patch Immediately
A batch of CVEs—CVE‑2026‑59739, ‑59969, ‑79993, ‑84439, ‑84501—has been uncovered in Apache Zookeeper 3.8.x (pre‑3.8.7) and 3.9.x (pre‑3.9.6). These flaws enable attackers to read sensitive data, tamper with stored values, and bypass security controls. Immediate patching and configuration hardening are required to mitigate the risk of data breaches and integrity violations.
Read briefing
Google Chrome Faces 20+ CVEs – Update Now to Patch Critical Vulnerabilities
The French CERT has issued an urgent alert after discovering a bundle of 20+ CVEs in Google Chrome that can be exploited to trigger unspecified security failures. Affected are all Chrome releases older than 153.0.8010.47 on Linux and Windows, and 153.0.8010.48 on macOS. The vulnerabilities were disclosed in a Google release on 15 September 2026. Immediate upgrade to the latest stable channel is mandatory to close the gaps.
Read briefing