
Threat Intel
Disruption of Chinese Phishing Kit Ecosystem: Storm-2990 & YAM Store
Microsoft’s Digital Crimes Unit exposed a Chinese‑language phishing kit ecosystem, including the Storm‑2990 developers and the YAM Store marketplace (Storm‑3119). The network distributed over 1 billion phishing emails and SMS to more than 75 000 organizations in healthcare, finance, wholesale, and IT sectors across Japan, the U.S., Australia, and India. Defenders should block known phishing kit domains, monitor for compromised cloud credentials, and apply Microsoft Defender detections.
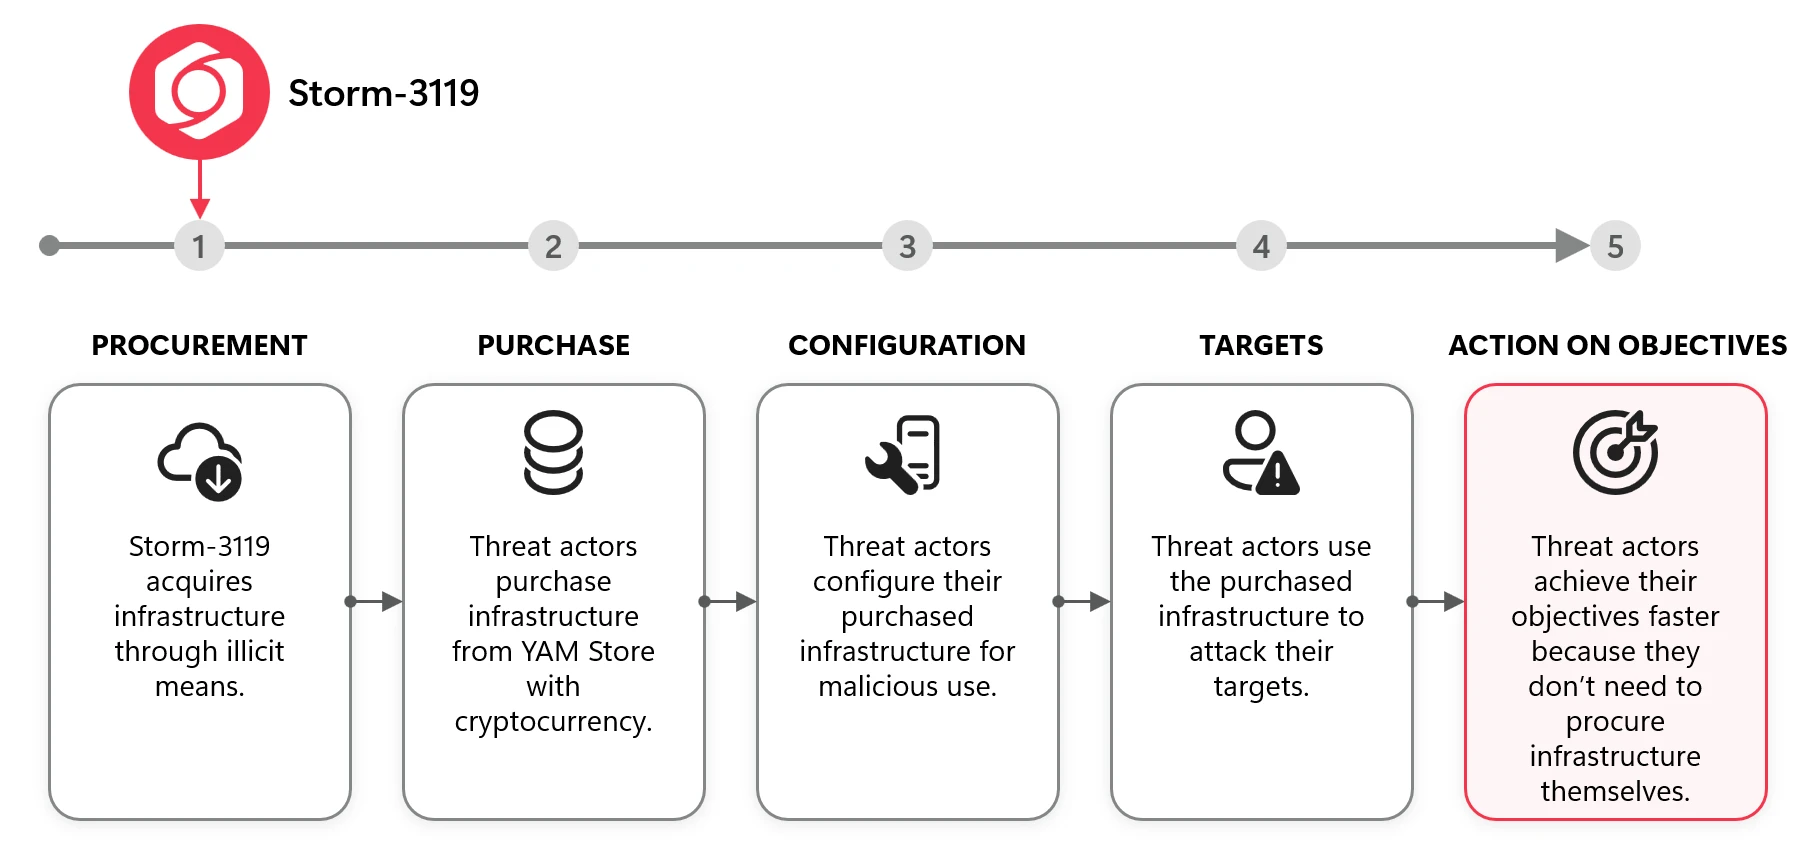
Microsoft’s Digital Crimes Unit (DCU) has dismantled a Chinese‑language phishing kit ecosystem that operated under the code names Storm‑2990 (developers) and Storm‑3119 (YAM Store marketplace). The network sold three phishing kits—CoGUI (NX/FA), Haozi (Phoenix), and Iron Man System—to threat actors who used them to send more than 1 billion phishing emails and SMS messages.
Microsoft’s research uncovered the ecosystem, revealing a coordinated supply chain of kit developers, infrastructure dealers, and end‑user threat actors.
Impact
- Targeted over 75 000 organizations worldwide, primarily in healthcare, financial services, wholesale distribution, and IT.
- Attacks originated from Japan, the United States, Australia, and India.
- Phishing kits leveraged compromised or fraudulent Microsoft and Google cloud environments.
Mitigation & Detection
- Block known phishing kit domains and IP ranges identified by Microsoft Defender.
- Enable Microsoft Defender for Office 365 and Microsoft Defender for Endpoint to detect and block kit‑related URLs.
- Inspect cloud environments for unauthorized access and validate credentials against known compromised lists.
- Apply the latest Microsoft Defender threat intelligence feeds to update firewall and DNS filtering rules.
Next Steps for Defenders
- Review email and SMS logs for large volumes of outbound messages matching known kit signatures.
- Conduct a threat hunting exercise focused on the three kit families (CoGUI, Haozi, Iron Man System).
- Coordinate with law enforcement if you identify infrastructure linked to Storm‑2990 or Storm‑3119.
- Share indicators of compromise with Microsoft’s threat intelligence community.
Related articles

BlueKit Phishing-as-a-Service Enables Rapid Account Hijacking
BlueKit, a turnkey phishing platform, lets attackers launch sophisticated account‑hijacking campaigns in minutes. The kit includes a command center, tracking, and a library of 97 brand templates. Defenders should block known BlueKit domains, monitor for phishing emails, and harden MFA on high‑risk accounts.
Read briefing
Tycoon 2FA AiTM: The Phishing‑as‑a‑Service Threat That Bypasses MFA on Entra ID & Google Workspace
Tycoon 2FA, the top‑selling phishing‑as‑a‑service kit, has evolved into a sophisticated adversary‑in‑the‑middle tool that captures MFA‑protected session tokens for Microsoft 365 and Google Workspace. After a March 2026 takedown, operators pivoted to device‑code phishing and OAuth abuse, keeping the kit at the forefront of global phishing trends. Elastic’s new detection rules map telemetry fingerprints across both platforms, enabling rapid incident containment in under ten seconds via Elastic Workflows.
Read briefing
P7 DarkSword iOS Exploit Kit Adds Keychain Theft and Remote Command Capability
A new P7 variant of the DarkSword iOS exploit kit has been identified, featuring a smaller on‑device footprint, on‑device keychain and crypto‑wallet theft, and two‑way command and control. The kit targets iOS 18.4–18.7 and has been used in campaigns across Saudi Arabia, Turkey, Malaysia, Ukraine, and by a Chinese‑speaking actor. Defenders should update iOS, enforce app‑whitelisting, and monitor for suspicious network traffic to mitigate the threat.
Read briefing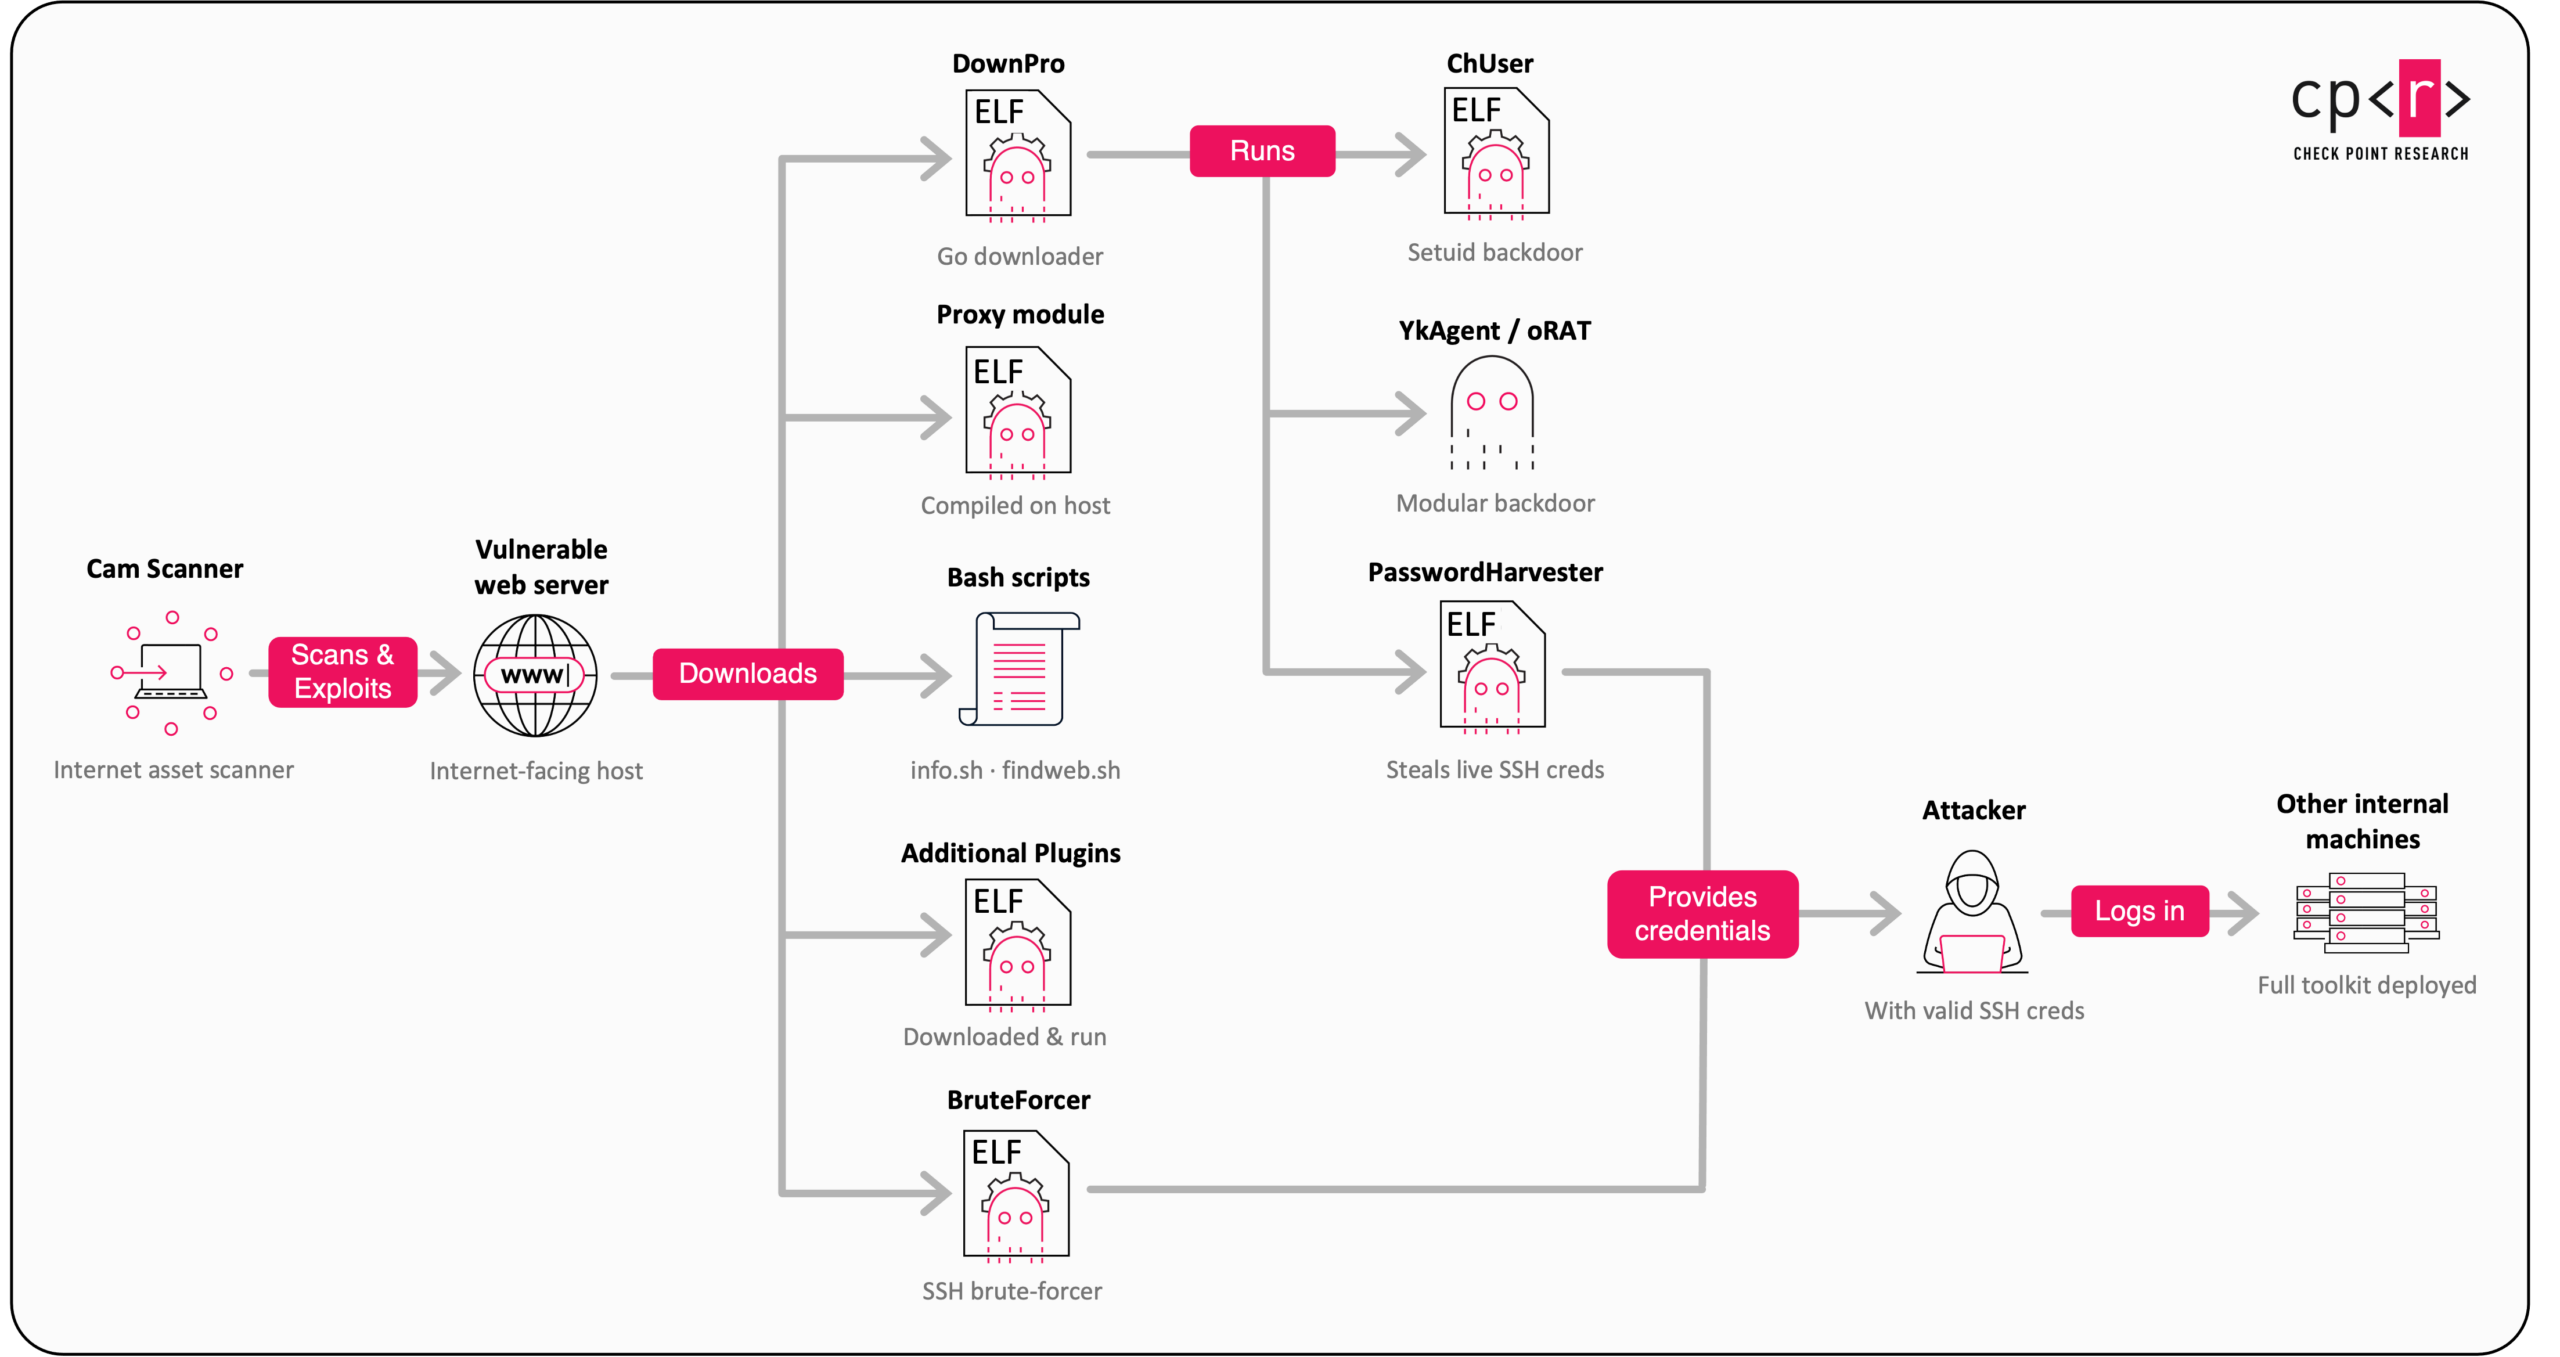
Chinese‑speaking gang hijacks Brazilian government sites to weaponise SEO for phishing and gambling scams
Since mid‑2025, a Chinese‑speaking cyber‑crime cluster dubbed Gambling Goblin has been infiltrating Brazilian government and educational web servers. By installing custom Apache modules, the attackers silently reverse‑proxy visitors to a vast network of phishing pages that masquerade as trusted app stores. The compromised high‑reputation domains are then leveraged to boost the attackers’ own content in search results, driving traffic to gambling and sports‑betting sites. The group deploys a heavily obfuscated Linux toolkit—including backdoors, credential stealers and reconnaissance agents—maki
Read briefing