
Threat Intel
Elastic 2022 Global Threat Report Preview: Endpoint Defense Evasion and Credential Dumping Trends
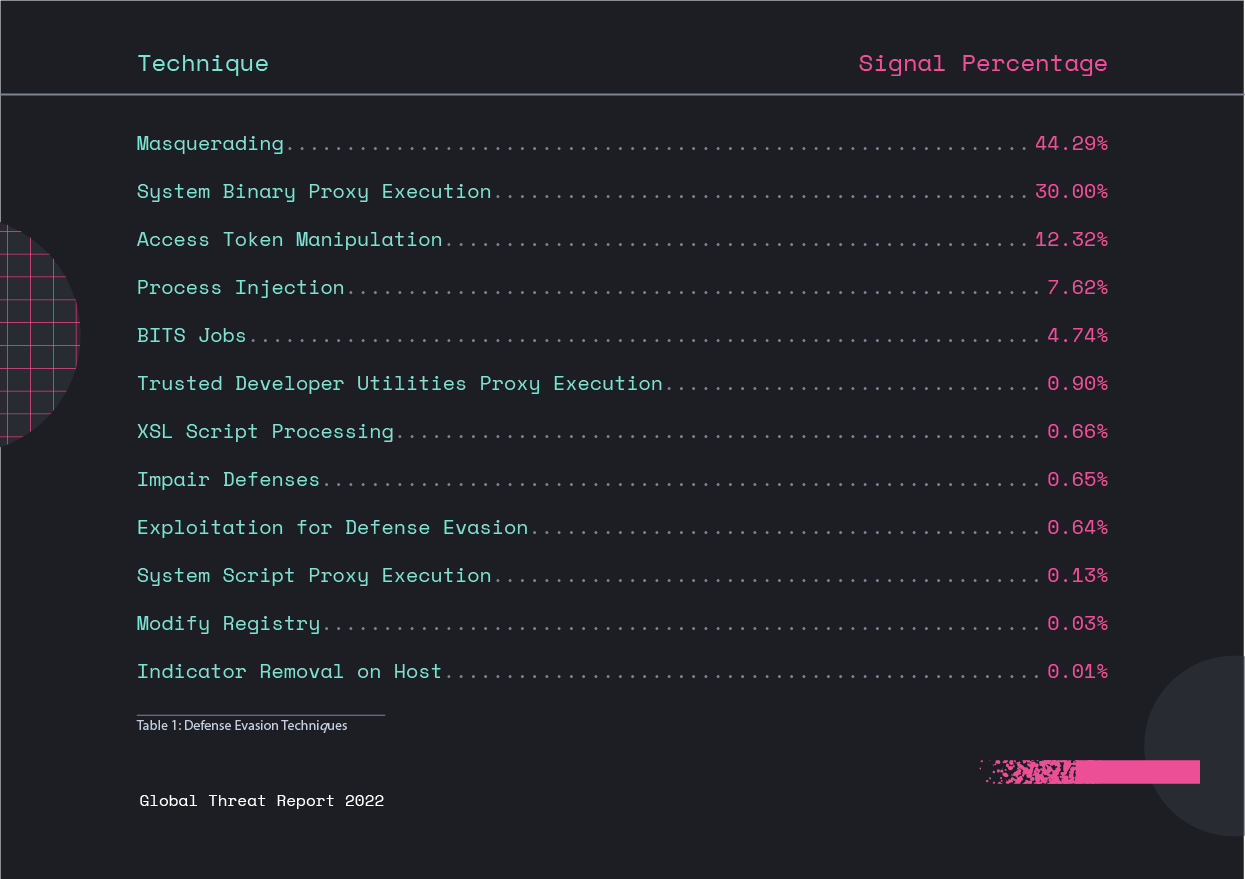
Elastic Security Labs released a preview of its 2022 Global Threat Report, revealing that 72% of defense‑evasion tactics involve masquerading and proxy execution of system binaries, while 77% of credential‑access attempts rely on OS credential dumping with known utilities. The findings underscore the need for defenders to harden endpoint detection and improve credential‑management controls. Security teams should review their monitoring and response playbooks accordingly.
What Happened
Elastic Security Labs published a preview of its 2022 Global Threat Report, summarizing the most common tactics seen against endpoints over the past year.
Impact
Defenders operating Windows, Linux, and macOS endpoints face a high volume of attacks that use:
- Masquerading and system binary proxy execution – 72% of all defense‑evasion techniques.
- OS credential dumping with standard utilities – 77% of all credential‑access techniques.
What to Do
Immediate actions for SecOps teams:
- Validate that endpoint detection and response (EDR) solutions are configured to alert on binary proxy execution and suspicious process spawning.
- Implement least‑privilege access controls and monitor for credential‑dumping tools such as Mimikatz, ProcDump, and built‑in utilities.
- Deploy file integrity monitoring to detect unauthorized modifications to system binaries.
- Regularly review and update run‑time whitelists to block known malicious utilities.
Next Steps
Elastic will release the full 2022 Global Threat Report with detailed recommendations. Security teams should stay tuned to Elastic Security Labs for actionable guidance and to adjust their playbooks based on the latest threat landscape.
Related articles
Elastic Security Labs Unveils Monthly Threat Insight Series – Guidance for SecOps
Elastic Security Labs has launched a monthly multipart series that expands on the Global Threat Report, covering topics such as defense evasion and credential access. The series offers actionable insights for SecOps teams to refine detection and response. Defenders should subscribe, review the latest editions, and integrate findings into their Elastic Security stack.
Read briefing
Elastic Global Threat Report Reveals Trends and Guidance for SecOps
Elastic Security’s first Global Threat Report outlines the latest threat landscape, highlights emerging attack techniques, and offers actionable guidance for defenders. The report is built from anonymized telemetry and open detection artifacts, providing a transparent view of how Elastic’s security features perform in the field. SecOps teams can use the findings to fine‑tune detection rules, prioritize mitigations, and stay ahead of ransomware and in‑memory threats.
Read briefing
GreyNoise Launches Project Swarm to Open Deception Network for Edge Defense
GreyNoise has introduced Project Swarm, a collaborative research initiative that opens its proprietary deception platform to the global security community. Designed to counter advanced threat actors targeting network perimeters, the project aims to improve visibility into blind spots across edge devices like firewalls and VPN gateways.
Read briefing
Iranian Targeted Malware Campaign: CHOSEN BRICK Exploits Dissidents, Activists, and Journalists
The National Cyber Security Centre (NCSC) has identified a new Iranian‑originated malware family, CHOSEN BRICK, that is specifically targeting dissidents, activists and journalists. The malware is delivered via spear‑phishing emails and exploits a Windows credential‑dumping tool to gain persistence. Defenders should block the associated domains, update endpoint protection, and enforce multi‑factor authentication for all users.
Read briefing